Version 8.6.0 Release Candidate 2 has been released. It's now entering the stabilisation phase for the developers, and the test phase for the users.
RPMs are available in the php:remi-8.6 stream for Fedora ≥ 43 and Enterprise Linux ≥ 8 (RHEL, CentOS, Alma, Rocky...) and as Software Collection in the remi-safe repository (or remi for Fedora)
⚠️ The repository provides development versions which are not suitable for production usage.
RC7 was GOLD, so version 8.6.0 GA was just released, at the planned date.
A great thanks to Matteo Beccati, Joe Ferguson and Daniel Scherzer, our Release Managers, to all developers who have contributed to this new, long-awaited version of PHP, and to all testers of the RC versions who have allowed us to deliver a good-quality version.
RPMs are available in the php:remi-8.6 module for Fedora and Enterprise Linux ≥ 8 and as Software Collection in the remi-safe repository.
For memory, this is the result of 6 months of work for me to provide these packages, starting in July for Software Collections of alpha versions, in September for module streams of RC versions, and also a lot of work on extensions to provide a mostly full PHP 8.6 stack.
PIN and touch for encrypted storage, login, screen unlock, sudo, and polkit
Lab work conducted November 3, 2026 Prepared November 3, 2026
Why I built this lab
My goal wasn't to eliminate very strong, high-entropy passwords or recovery credentials. It was to virtually eliminate their use during normal daily operations, reserving them for emergencies such as lost security keys, hardware failures, or other serious recovery situations. I wanted to rely on either my primary or backup FIDO2 security key for nearly all routine authentication—ideally 99% of the time or more.
A password that isn't routinely entered presents fewer opportunities for someone watching or for keylogging malware to capture it. Although a keylogger could still capture a security key's PIN, knowing that PIN alone doesn't ordinarily replace possession of the registered hardware key. Another important advantage is the physical-presence requirement. Even if a registered security key remains inserted in the computer, someone attempting to authenticate remotely with a stolen PIN generally cannot complete a new authentication that requires physically touching the key. This provides another layer of protection, although it does not prevent attacks against an already compromised or unlocked system, nor does it eliminate the risks associated with retained password fallbacks. For me, minimizing routine password exposure while preserving strong emergency recovery options is a practical application of defense in depth.
Policy boundary. This lab accepts either a registered key with its PIN and touch or the retained password fallback. It does not require a key in addition to the account password. Someone who knows a valid fallback password can still authenticate without the key. The benefit here is reduced routine password use, not removal of every password-based route.
The two Yubico Security Key NFC devices completed the reported tests across all four USB ports of one Dell Latitude E6430 ATG. Both Identiv uTrust devices enrolled successfully and sometimes unlocked the disk, but later disk-unlock tests were intermittent. I cannot recommend those two uTrust devices for dependable boot unlocking on this machine. Their cause of failure remains unresolved.
This work took place on November 3, 2026, during my first day testing Fedora Linux 45. Several hours of successful testing with the Yubico keys are encouraging. They are not a long-term reliability study or a compatibility guarantee for other systems.
Use a disposable lab machine
Do not perform this procedure on a production machine. Storage selection during installation can erase data; authentication and boot changes can lock you out. Back up important data, retain the disk passphrase and account password, and have working recovery media before attempting the lab. Use these steps at your own risk.
How to use this guide
Follow Steps 1 through 10 in sequence. Read the device-identification gate before copying any disk command. Each stage includes an observable success check. The final sections record recovery behavior, failures, and the limits of the experiment. The companion article is a shorter account of the findings; this guide contains the repeatable procedure.
What was tested
Component
Lab record
Computer
Dell Latitude E6430 ATG; one physical test machine
Operating system
Clean Fedora Linux 45 Workstation installation; GNOME with GDM
Kernel captured after update
7.2.15-300.fc45.x86_64
systemd captured in boot log
262.1-1.fc45
PAM packages captured
pam-u2f and pamu2fcfg 1.4.0-8.fc45
Storage
Samsung SSD 870 EVO 2 TB; LUKS2 with Btrfs for root and home
First Yubico key
Security Key NFC, USB-A; firmware 5.7.4
Second Yubico key
Security Key NFC, USB-A; firmware 5.8.0
Other keys retained
Two Identiv uTrust FIDO2 security keys
Authentication policy
Key PIN and touch; account-password fallback retained
I use “YubiKey” informally in the lab conversation. The captured device information identifies these two devices as Yubico Security Key NFC models. This is not a test of every YubiKey product or every firmware release. No uTrust firmware revision was established in the record.
Two enrollments for each physical key
Disk unlocking and operating-system authentication are separate paths. A LUKS enrollment authorizes the key to unlock the encrypted volume. A PAM registration authorizes it for the local account. Completing one does not complete the other. Polkit and sudo used the existing shared PAM configuration; no separate key profile was added to each application.
My earlier Fedora 42 article covered Cinnamon and LightDM (Murphy, 2025). This installation used GNOME and GDM, distribution packages, and authselect. Do not combine the earlier article’s manual configuration with this procedure.
The original November 3 lab did not configure SSH, remote desktop, browser passkeys, a TPM unlock policy, measured boot, or new authorization rules. The optional SSH extension at the end was completed on November 17. Full disk encryption here means the main system and user-data volume is encrypted; the EFI and /boot partitions remain outside it.
Step 1 Install Fedora Linux with encrypted storage
I performed a clean installation rather than upgrading the previous system. The recorded image was Fedora-Workstation-Live-45-1.4.x86_64.iso. I checked the downloaded image against its published checksum and wrote the installer with Rufus 4.7.2231 using DD image mode. Use the checksum supplied for the exact image you download; this guide does not publish a reusable checksum value.
The boot-media check failed during the lab. I proceeded with the direct live-boot option on this disposable machine. That was a lab exception, not a resolved diagnosis or a recommended shortcut. If your media check fails, stop and recreate and verify the installation medium before following this guide. A matching downloaded-image checksum alone does not establish that the written USB medium passed verification.
Boot the verified live installer in UEFI mode. Choose the intended disposable installation disk, review the proposed storage changes, and enable “Encrypt my data.” Set and securely record a strong disk passphrase. Confirm the keyboard layout used at boot. Review the installation summary carefully before approving the destructive installation.
Figure 1
The installer encryption choice
Note. The empty passphrase fields show the setup stage, not a suggested password length.
Finish installation, restart into the installed system, and confirm that the disk passphrase unlocks it. Complete initial setup, create the local account and account password, and verify that you can log in. The lab account was joemurphy; use your own account. Third-party repositories were not needed for the FIDO2 procedure.
Step 2 Update and identify the encrypted volume
sudo dnf upgrade --refresh
sudo reboot
After the update completed and the installed system restarted, I checked the release, running kernel, and storage layout:
crypto_LUKS backing the Btrfs root and home mounts
Device gate. Every /dev/sda3 command below refers to this lab’s encrypted partition. Your device may be /dev/nvme0n1p3 or something else. Establish the partition backing your installed root and home filesystems, then substitute that verified device everywhere. Do not use a whole disk, an already unlocked /dev/mapper path, or a partition chosen only because its number matches mine.
Figure 2
Fedora Linux 45 installation summary showing the EFI partition, /boot partition, and encrypted Btrfs root and home volumes.
sudo cryptsetup luksDump /dev/sda3 | head -n 12
Success check: the header reports LUKS version 2 for the intended encrypted partition. The inspection command above displays only the beginning of the header.
Before changing authentication
Confirm the disk passphrase and account password work and are available independently of the computer. Keep a second key available as you add it later. The lab recorded a local header backup in the next step, but no completed off-device backup was documented. A backup kept only on the encrypted root filesystem cannot be reached if that filesystem cannot be unlocked. Arrange protected off-device recovery copies before relying on this design.
Step 3 Prepare the first key and preserve the header
Connect only the key being enrolled. This avoids ambiguity when a command automatically selects a FIDO2 device. The first key already had a PIN; the second Yubico key’s PIN was set and tested in Windows before its Linux enrollment. A key with no PIN must have one configured using its supported management tool before the PIN-required steps below.
sudo systemd-cryptenroll --fido2-device=list
sudo dnf install yubikey-manager
ykman info
ykman fido info
ykman fido access verify-pin
Success check: device information identifies the intended Yubico key and the existing PIN verifies. These ykman commands are for the Yubico devices. They are not a management procedure for the uTrust keys. Do not reset an authenticator to troubleshoot an ordinary prompt; a reset would require a separate credential-recovery plan.
The tools’ existing support was sufficient; this lab did not need to compile pam-u2f or add custom udev rules. Do not import those changes from a different version of Fedora Linux.
sudo cryptsetup luksHeaderBackup /dev/sda3 --header-backup-file /root/luks-backup.img
sudo ls -lh /root/luks-backup.img
sudo cp -a /etc/crypttab /root/crypttab.before-fido2
Figure3
FIDO2 security-key detection, YubiKey identification, and successful PIN verification on Fedora Linux 45.
Note. The screen shots above show the commands and observed results from the Fedora Linux 45 lab. Device information, firmware version, and available FIDO2 capabilities may differ between security keys. The final panel confirms successful PIN verification. Use the complete commands provided in the guide rather than copying them from the photographs.
Success check: the header-backup command completes, and the recorded file was 16 MB and accessible only to root. Preserve it securely. This was the pre-enrollment backup, not evidence of a later backup containing every enrollment. The crypttab copy preserves the original boot-unlock configuration.
Do not overwrite an existing backup from an earlier attempt without first deciding which state you need to retain. Header restoration and slot deletion were not exercised in this session, so neither is presented as a tested recovery procedure here.
Step 4 Enroll the first key for disk unlocking
With the intended key still the only FIDO2 authenticator connected, run the enrollment command against your verified LUKS2 partition:
The prompt for the current disk passphrase authorizes adding the enrollment. The later security-token PIN prompt asks for the key’s PIN. They are different secrets. Follow the touch prompts when the key requests confirmation.
Success check: the command reports a new FIDO2 token and a key-slot number. The first Yubico key received slot 1 in this lab. Your number can differ; record what the tool actually reports. LUKS2 enrollment requires a FIDO2 device supporting the hmac-secret extension (systemd project, n.d.).
Figure 4
LUKS2 header backup and successful FIDO2 security-key enrollment using systemd-cryptenroll, showing the authentication prompts and confirmation of enrollment in key slot 1.
Note. This is a historical result, not a slot number to enter manually.
Add FIDO2 discovery to the existing crypttab entry
First inspect your existing entry. In this lab, its option field was exactly discard,x-initrd.attach. The successful edit appended fido2-device=auto to that field:
Configuring FIDO2 discovery in /etc/crypttab and preparing Dracut to include FIDO2 support in the initramfs.
Run that substitution only after confirming the matching option field belongs to your intended encrypted volume and does not already contain the new option. It is the lab’s exact edit, not a general editor for arbitrary crypttab layouts. If your configuration differs, stop and adapt it deliberately; do not replace unrelated entries.
The verified entry retained four fields: its existing mapping name, its UUID source, none, and the comma-separated options. The resulting options were discard,x-initrd.attach,fido2-device=auto. Keep your existing mapping name and UUID.
Step 5 Include FIDO2 in the boot image
I verified that the dracut FIDO2 module was available, added it to the configuration, rebuilt the running kernel’s initramfs, and checked the resulting image. Preserve the spaces inside the quoted module list (Dracut project, n.d.).
Success check: the module listing includes fido2, the rebuild completes, and inspection of the built image includes fido2 and the encryption-related modules. Do not reboot past an unexplained rebuild failure. This command rebuilt the currently running kernel’s image; testing every installed or future kernel was outside this session.
Figure 6
Dracut configuration, initramfs rebuild, and verification that the FIDO2 module is included in the boot image.
Note. Read the commands in the text rather than copying from a perspective photograph.
Save your work and reboot with the key inserted before power-on. At the disk-unlock screen, enter the key’s PIN and touch it when requested. Success means the system progresses to the graphical account-login screen. At this point the account still uses its existing password; PAM enrollment comes next.
Step 6 Register the key for the local account
Disk enrollment has not registered the key for login or sudo. While logged into your own account, inspect the active authentication profile and install the packaged PAM tools:
sudo authselect current
sudo dnf install pam-u2f pamu2fcfg
sudo authselect check
authselect list-features local
The lab profile was local, with with-silent-lastlog, with-mdns4, and with-fingerprint already enabled. The configuration check reported valid, and the available feature list included with-pam-u2f. If your profile or validity result differs, resolve that difference before continuing. Do not force-select a new profile over an unfamiliar configuration.
Register as your normal account, without sudo. The first registration writes the initial mapping file; do this only when you are creating that file for the first key. If you already have registrations, use Step 8 to preserve them.
Enter the token PIN and complete the requested touch. The first Yubico registration produced 207 bytes. That count is a lab observation, not a universal validity requirement; the uTrust records were longer. Registration must complete successfully with the intended key.
The registration option requests PIN verification during authentication; user presence was not disabled (Yubico, n.d.-b). This is policy for these registrations. It does not change every website or application to require the PIN, and insertion alone does not trigger authentication.
Success check: the named authselect backup is reported and the configuration remains valid. Authselect manages the shared PAM files; enabling a supported feature avoids hand-editing those generated files (Authselect project, n.d.). The password fallback remained enabled. This was not the with-pam-u2f-2fa feature that would require the account password as well.
Figure 7
Fedora Linux 45 PAM U2F configuration: verifying the authselect profile, registering the security key, enabling PAM U2F authentication, and validating the final configuration.
Step 7 Verify each authentication path
sudo -k
sudo whoami
Success check: a fresh sudo authentication asks for the PIN and then a touch, and whoami returns root. sudo -k invalidates the current cached sudo authentication. Without it, a successful command may simply reuse a timestamp. Keep your existing logged-in session open while testing.
Run this as your normal user in a terminal within the local GNOME desktop session, without sudo:
pkexec /usr/bin/whoami
Success check: the graphical authorization dialog accepts the key’s PIN and touch, and the command returns root. This confirms the polkit path used by that test. It is not a claim that every desktop application uses the same authorization policy.
Press Super+L to lock the desktop. Wake it, authenticate with PIN and touch, and confirm your existing session unlocks. Next save your work and use the top-right system menu’s Log Out action. At the full GDM sign-in screen, select your account and repeat the key authentication. A lock-screen test does not replace a full logout-and-login test.
No separate polkit key enrollment was necessary. During investigation, the vendor GDM files under /usr/lib/pam.d led to password-auth, while sudo and polkit used system-auth. The same account mapping was used through those paths. No manual GDM or polkit PAM edits were part of the successful procedure.
Figure 8
Verification of FIDO2 authentication on Fedora Linux 45, demonstrating successful sudo authentication, graphical session unlocking, security-key touch confirmation, and polkit authorization.
Step 8 Add a second key without replacing the first
Repeat this stage with only the new key connected. The following is the exact successful second-Yubico workflow. That key already had a verified PIN set in Windows. Generate its account registration into a temporary file:
Success check: registration completes; the recorded Yubico output was 207 bytes. The backup command must complete before the next step. Be careful with the dot in ~/.config. An early failed copy in the lab used ~/config and was corrected before proceeding.
Append the new credential to the existing account’s line, preserving its earlier credentials. This script checks that the usernames match, then joins the new credential to the existing mapping:
Run the merge once for this newly generated registration. It is not a duplicate-removal utility or a validator for arbitrary malformed or multi-user files. It was used on the lab’s single-account, single-line mapping. Do not repeatedly append the same file.
sudo -k
sudo whoami
Success check: with only the new key connected, sudo requires its PIN and touch and returns root. Then test pkexec, lock-screen unlock, and full logout/login as in Step 7. The default mapping format permits several colon-separated credentials for one username (Yubico, n.d.-a). No second authselect feature change is needed.
Step 9 Enroll the additional key for the disk
The second key’s successful sudo test does not authorize it for LUKS. Keep only that key connected and repeat the same disk-enrollment command, using the verified encrypted partition:
Enter the existing disk passphrase, then this key’s PIN, and confirm presence when requested. Success check: a new FIDO2 enrollment is reported. The second Yubico key received slot 4 because two uTrust keys had already been added between the Yubico enrollments. A new two-key installation can allocate different slot numbers.
Lab slot
Enrollment retained
Result in this session
0
Original disk-passphrase fallback
Successfully unlocked without a key
1
First Yubico Security Key NFC
Repeated disk-unlock tests passed
2
First Identiv uTrust
Enrolled; later intermittent unlock failures
3
Second Identiv uTrust demo key
Enrolled; later intermittent unlock failures
4
Second Yubico Security Key NFC
Repeated disk-unlock tests passed
The slot labels above record enrollment order and observed results. They are not commands, universally assigned numbers, or a suggestion to delete a slot. Every enrollment was left in place, including the two uTrust enrollments.
The lab did not repeat the crypttab or dracut changes for each added key. It repeated enrollment and validation. The account mapping and LUKS header are separate records, so keep track of both when managing several physical keys.
What the demo PIN means
No PIN value is needed for this guide. Choose your own, and keep the primary and backup keys under your control. The demonstration key’s PIN was not published here. Changing a PIN and resetting an authenticator are different operations; this session did not test a reset or a post-demo removal-and-reenrollment sequence.
Step 10 Test the complete sequence
For each test, connect only the key you intend to evaluate. Insert it into the selected USB port before turning the machine on. Cold-boot disk unlocking, full account login, and screen unlocking exercise different stages. Save work before any restart or logout.
Test
Observed Yubico result
First key through four physical USB ports
Disk unlocking succeeded in all four reported port tests
Second key through four physical USB ports
Disk unlocking and login succeeded in all four reported port tests
One key for the disk and the other for the desktop
Succeeded; additional swaps and port changes also reported successful
Screen lock followed by key rotation
Each enrolled key unlocked the screen in reported tests
Fresh sudo authentication
PIN plus touch; root returned
Graphical polkit test
PIN plus touch; root returned
After transition to Yubico-only testing
No further failures reported by the author
The four port names used in my notes were top right, top left, middle right, and bottom right as viewed while using the laptop. These describe this test unit, not USB controller types. I did not record a formal attempt total or a measured failure rate, so no percentage or reliability score is claimed.
A reproducible test record should identify the physical key, port, whether it was present before power-on, which stage was tested, and the exact result. If an attempt fails, avoid changing several variables at once. In this session, early successes did not predict the later uTrust failures.
Late insertion was less dependable
Inserting a key after the boot-unlock screen had appeared worked sometimes but not consistently. Having the selected key connected before power-on was the more dependable workflow observed. This does not establish the reason for the difference or guarantee hot-plug behavior across keys and systems.
Success with PIN and touch at login does not remove the account password or change privilege membership. Existing sudo and polkit authorization decisions still determine which actions the account may perform.
Recovery and the problems encountered
The tested recovery path
I rebooted with the key unplugged. The boot screen initially continued asking for a LUKS2 token PIN. Pressing Enter with an empty field did not immediately switch to a disk passphrase. Escape changed between graphical and text views; it did not cancel token authentication.
In the successful recovery attempt, I entered the usual token PIN with the token absent and waited. The prompt eventually changed to the disk-passphrase prompt. I entered the strong disk passphrase, the disk unlocked, and I logged in using the account-password fallback. The delay was not measured. This sequence documents what happened; it does not establish a universal timeout or a recovery procedure for a forgotten token PIN.
Figure 9
The initial boot prompt still asked for a token PIN
Note. The later disk-passphrase prompt was a different stage.
Recovery secrets must remain available outside the encrypted computer. Do not discard them because the keys are working. The fallback intentionally provides another way in; its strength and storage matter to the overall design.
The uTrust result changed with further testing
Both uTrust keys completed PAM registration and LUKS enrollment. Initial sudo, polkit, login, and screen-unlock tests succeeded. The first uTrust GDM failure led us to inspect shared PAM configuration and logs. A later correctly controlled attempt worked without a demonstrated configuration repair.
Repeated boot testing then exposed intermittent disk-unlock failures with both uTrust devices, including attempts with a key connected before startup. The Yubico key unlocked the same machine during this troubleshooting. Some earlier attempts might have involved the wrong PIN, so those attempts alone are inconclusive; the later repeated failures are why I would not rely on these uTrust devices for boot unlocking on this test unit.
Periodic green flashing and a brief red indication were observed on uTrust devices. Their meaning and any causal connection were not established. The log search reported no matching SELinux AVCs in the inspected results. Neither observation identifies a firmware, USB, PAM, or Fedora Linux defect.
Security boundaries and operating practice
This design reduces routine use of a reusable account password and gives a practical hardware-backed route into an encrypted personal computer. It still has a PIN and retained fallback passwords. Calling it a passwordless daily workflow describes the tested user experience; it does not mean passwords or password hashes have been eliminated.
The hardware path requires the registered key and its PIN, but password fallback remains an alternative. A stolen fallback account password can therefore still permit account access; a stolen disk passphrase can still unlock the volume. Touch confirms presence for the requested operation; it is not proof that the request is trustworthy. Malware, a compromised privileged account, or a tampered boot environment can defeat assumptions outside this lab. No adversarial testing was performed.
Local disk unlocking and PAM are not a test of browser WebAuthn phishing resistance. This guide makes no promise that these local paths prevent all phishing, session theft, keylogging, or malicious authorization prompts. Encryption protects stored data when locked; it does not shield an already unlocked system from every threat.
The PAM registration file was stored in the user’s home directory, so it was available after the system volume unlocked. That arrangement is not a hardened defense against an attacker already able to modify that account’s files. Individually encrypted or network-mounted homes were not tested. The registration also used the default hostname-based relying-party identity; renaming or moving the configuration was not tested.
Keep system updates, independent backups, physical protection, and least privilege in the design. A successful root test demonstrates authorized escalation; it is not an instruction to operate as root routinely. Key removal did not configure automatic screen locking or revoke a cached sudo timestamp.
The approach fits a defense-in-depth strategy. It can support a broader zero trust design, but adding a token does not itself create one. Zero trust separates authentication and authorization and avoids treating location or ownership as sufficient trust (Rose et al., 2020). Apply those principles to the rest of the environment as well.
What I would require before depending on it
My next operational requirements are protected off-device recovery material, continued testing after updates, and a deliberate plan for lost-key revocation. Those are recommendations, not completed tests in this report. Slot removal, header restoration, key resets, and forgotten-PIN recovery were not exercised. All existing enrollments remain intact.
On November 17, 2026, following editorial suggestions from Gregory, I updated my Fedora workstation and extended the original Fedora Linux 45 lab to test remote SSH authentication from a Windows computer at home. OpenSSH accepted the Yubico FIDO2 key with PIN and touch, and a fresh reconnection also succeeded.
After updating, the Fedora workstation ran kernel 7.3.4-300.fc45.x86_64, openssh-clients and openssh-server 10.5p1-1.fc45, and libfido2 1.17.0-6.fc45. The Windows computer used OpenSSH_for_Windows_9.5p2 with LibreSSL 3.8.2.
Examples use 192.168.x.x for the Fedora address and <FEDORA_USER> for its account. Replace these placeholders before running commands. Run Windows commands one at a time in a regular PowerShell window. Run Fedora commands as the normal user, using sudo only where shown.
After reboot, I recorded the versions above. SSH was initially inactive and disabled. I generated missing host keys, checked the configuration, and started the service for the session:
ip -br -4 address show scope global
sudo firewall-cmd --get-active-zones
sudo firewall-cmd --list-all
sudo ssh-keygen -lf /etc/ssh/ssh_host_ed25519_key.pub
The active FedoraWorkstation firewall zone already allowed SSH; I added no firewall rule or router port forwarding. Starting sshd did not enable it at boot. I recorded the ED25519 host fingerprint for comparison from Windows.
2 Create the SSH credential on Windows
I connected one Yubico key to Windows and confirmed that ssh -V reported 9.5p2 and ssh -Q key listed the sk- key types. Then I ran:
I entered the existing security-key PIN, touched the key, and left the separate local file passphrase empty. This created a non-resident SSH credential with a local handle file and a .pub public-key file. The local handle file is needed with this key; the key was not reset.
3 Copy and authorize the public key
From Windows, I copied only the public key using the Fedora account password for this initial transfer. I accepted the host only after its ED25519 fingerprint matched the value recorded locally on Fedora Linux:
On Fedora Linux, as the normal user, I checked the transferred public key’s fingerprint against the Windows result:
ssh-keygen -lf "$HOME/fedora45-ssh-lab-key1.pub"
I verified that the transferred public key’s fingerprint matched the Windows result. The following registration commands back up any existing authorized_keys file and add the key with verify-required:
(
set -e
lab_pub="$HOME/fedora45-ssh-lab-key1.pub"
umask 077
mkdir -p "$HOME/.ssh"
chmod 700 "$HOME/.ssh"
if [ -f "$HOME/.ssh/authorized_keys" ]; then
    cp -p "$HOME/.ssh/authorized_keys" \
        "$HOME/.ssh/authorized_keys.before-fido2-$(date +%Y%m%d-%H%M%S)"
fi
touch "$HOME/.ssh/authorized_keys"
lab_entry="verify-required $(tr -d '\r\n' < "$lab_pub")"
if ! grep -qxF "$lab_entry" "$HOME/.ssh/authorized_keys"; then
    printf '\n%s\n' "$lab_entry" >> "$HOME/.ssh/authorized_keys"
fi
chmod 600 "$HOME/.ssh/authorized_keys"
restorecon -Rv "$HOME/.ssh"
ssh-keygen -lf "$HOME/.ssh/authorized_keys"
)
The fingerprint matched. The verify-required entry requires user verification for this SSH key; default touch requirements remain in place. No SSH restart or PAM configuration change was needed.
4 Test from Windows
With the key connected to Windows, I ran this single command. It selects the lab credential, disables agent use and connection sharing, and permits only public-key authentication for this connection:
Windows requested the security-key PIN and touch. SSH reported “User presence confirmed” and opened the Fedora Linux shell.
Observed results
whoami
hostname
printenv SSH_CONNECTION
whoami returned my Fedora account, hostname returned fedora, and SSH_CONNECTION showed the Windows client connecting to the Fedora workstation on port 22. I exited and connected again successfully with PIN and touch. No Fedora account password was used for these public-key login tests.
Figure 10. Windows requested the external security key PIN during SSH login. The PIN field is redacted.
Figure 11. Successful SSH authentication and remote identity checks. Network addresses, account identifiers, the key fingerprint, and the connection’s temporary port are redacted. Remaining command text is unchanged.
Scope: these results cover one enrolled SSH key and successful local-network logins. Server password authentication remained available; password fallback was disabled only in the test command. The workstation was already running with its encrypted disk unlocked.
Community acknowledgment
I am grateful to the Fedora community and the contributors to systemd, cryptsetup, dracut, authselect, PAM, libfido2, and the hardware tooling. Being able to combine their work into a useful home lab is the reason this project was possible. I hope the results help others test carefully and share what they learn.
Rose, S., Borchert, O., Mitchell, S., & Connelly, S. (2020). Zero trust architecture (NIST Special Publication 800-207). National Institute of Standards and Technology. https://doi.org/10.6028/NIST.SP.800-207
Steps 1–10 describe my November 3, 2026, lab session. The optional SSH section documents the November 17, 2026, extension. External references explain the tools and security concepts; they do not independently reproduce or certify these results.
AI disclosure
I personally performed the original lab work and testing on November 3, 2026, and the optional SSH extension on November 17, 2026, using my Fedora Linux 45 lab workstation and, for SSH, one of my Windows computers at home. I used AI tools to assist with research, editing, formatting, and preparing composite illustrations from my original lab photographs. After completing the SSH tests, I also used AI to compile and format that portion of the report to save time. The commands and documented results come from work I performed, not AI-generated testing. Readers should use the written commands rather than transcribing commands from the illustrations. The results, conclusions, and any errors remain my responsibility.
A follow-up on PIN and touch for encrypted storage and everyday authentication
On my first day working with Fedora Linux 45, I wanted to see how far I could get without typing my account password during normal use. The goal was straightforward: use a physical FIDO2 security key, its PIN, and a touch to unlock the encrypted system, sign in, unlock the screen, and approve administrative actions. Keep strong recovery passwords available when the keys are not.
By the end of the session, two Yubico Security Key NFC devices were working across all four USB ports of my Dell Latitude E6430 ATG. I could unlock the disk with one key and authenticate at the desktop with the other. Repeated swaps continued to work. Two Identiv uTrust devices also enrolled and initially passed several tests, but later boot-unlock failures made their results much less dependable.
This is a non-production lab report. Do not apply it to a production machine. I spent several hours testing on November 3, 2026, and found the Yubico workflow consistent in those tests. That is a useful result, not a guarantee of long-term stability or compatibility with a different computer. Keep backups, independent recovery secrets, and a way to recover the installation.
Why this is worth exploring
The policy is a choice of a registered key with PIN and touch or the retained password fallback. It does not enforce possession of a key for every login. Anyone who knows a valid fallback password can still use it. That distinction matters when deciding which threats this setup addresses.
My goal is to build a computer where I almost never need to enter a reusable password during normal operations. Ideally, I want to rely on either my primary or backup FIDO2 security key for 99% or more of everyday authentication. I'm not eliminating passwords. Instead, I retain very strong, unique, high-entropy disk and account passwords as protected recovery credentials for lost keys, hardware failures, or other emergencies. The 99% figure is my objective, not a measured result from this lab.
The security benefit is reducing unnecessary password exposure. A password I don't routinely type presents fewer opportunities for someone watching or for keylogging malware to capture it. Although a keylogger could still capture a security key's PIN, that PIN alone generally cannot complete a new authentication requiring possession of the registered key and a physical touch, even if the key remains inserted in the computer. This adds another barrier against unauthorized access, although it doesn't prevent attacks against an already compromised system or eliminate the risks associated with retained password fallbacks.
I see this as part of defense in depth alongside updates, careful backups, physical security, and least privilege. It is compatible with thinking in zero trust terms, where authentication and authorization are distinct and access does not follow merely from being on a trusted network (Rose et al., 2020). A token by itself is not a zero trust architecture.
There are limits. I did not test resistance to malware, a modified boot environment, phishing, or a stolen live session. Local PAM authentication and disk unlocking do not establish browser WebAuthn phishing resistance. Encryption protects stored data when locked; it is not a complete defense for an already compromised, unlocked computer.
A fresh installation and a different desktop
My Fedora 42 article described a Cinnamon and LightDM setup (Murphy, 2025). This was a clean Fedora Workstation 45 installation using GNOME and GDM. I used the distribution’s packages and the existing authselect profile rather than importing the older article’s manual PAM and build steps.
During the original November 3 session, the system ran kernel 7.2.15-300.fc45.x86_64, with systemd 262.1-1.fc45. The PAM packages were pam-u2f and pamu2fcfg 1.4.0-8.fc45. The two Yubico devices identified themselves as Security Key NFC models with firmware 5.7.4 and 5.8.0. I did not establish a uTrust firmware revision.
The installer encrypted the main system volume, containing Btrfs root and home filesystems. The EFI and /boot partitions were outside that encrypted volume. My target was /dev/sda3; that name is specific to this installation. A reader must identify the correct encrypted partition on their own machine before copying any disk command.
One installation exception deserves disclosure: the boot-media check failed even though I had checked the downloaded image’s checksum. I proceeded on this disposable lab system. I did not establish why it failed, and I do not recommend ignoring a failed media check. Recreate and verify the medium before treating the installation as a trustworthy starting point.
Disk enrollment and account registration are separate
I first preserved a LUKS header backup and a copy of /etc/crypttab. The backup recorded in this session stayed on the local encrypted root filesystem; a completed off-device recovery backup was not documented. That is a gap to address before depending on this arrangement.
With only the intended key connected, I enrolled it against the verified LUKS2 partition with client-PIN and user-presence requirements. The systemd documentation describes the FIDO2 hmac-secret requirement for this path (systemd project, n.d.). I added fido2-device=auto to the existing crypttab option field, included the dracut fido2 module, rebuilt the running kernel’s initramfs, and checked that the module was present (Dracut project, n.d.).
The first boot test took a PIN and touch and reached the graphical login screen. That completed the disk part. It did not enroll the key for my account.
For the account, I used pamu2fcfg --pin-verification as the normal user and stored the mapping in ~/.config/Yubico/u2f_keys. The registration option requests PIN verification for authentication (Yubico, n.d.-b). I then enabled with-pam-u2f in the existing local authselect profile, preserving an authselect backup and checking that the configuration remained valid (Authselect project, n.d.).
The feature used the existing shared PAM paths. I did not need a separate key enrollment for polkit, a new polkit authorization rule, or manual edits to the GDM files. A fresh sudo test returned root after PIN and touch. The graphical pkexec test did the same. Screen locking and a full logout-and-login test also passed.
The companion lab guide 1 contains the successful commands and success checks in sequence. They are not a universal copy-and-paste recipe for a different partition layout or an existing custom authentication stack.
Adding the backup key without losing the first
The second Yubico key already had a PIN set and tested before Linux enrollment. I registered it to a separate file, backed up the current account mapping, and appended its credential to the same account line. The mapping format accommodates multiple credentials for one username (Yubico, n.d.-a). I tested the new key alone before proceeding.
I then enrolled that physical key separately for LUKS. It received slot 4 because two uTrust enrollments had already occupied slots 2 and 3. The first Yubico enrollment was in slot 1, and the original disk-passphrase route remained in slot 0. Slot numbers record this session’s order; they are not values readers should reproduce manually.
All enrollments remain in place. I have not removed the uTrust entries or reset any key. The procedure did not require a fresh crypttab edit for every additional authenticator.
What repeated testing changed
At first I was excited that the uTrust keys were working. Both produced account registrations, both enrolled for the disk, and several sudo, polkit, login, and screen-unlock tests succeeded. An initial GDM problem later disappeared in a correctly controlled test without a demonstrated configuration repair.
The important finding came from continuing to test. Moving through ports and restarting exposed intermittent disk-unlock failures with both uTrust devices, even when connected before startup. The Yubico key unlocked the same machine during troubleshooting. Some earlier attempts might have involved an incorrect PIN, so I do not use those attempts alone to establish a defect. Later repeated failures were enough for me to stop treating these two uTrust devices as dependable boot keys on this computer.
I observed periodic green flashing and a brief red indication on uTrust devices. I do not know what caused those indications or whether they explain the failures. The inspected SELinux search found no matching AVCs, which is not a diagnosis either. I cannot say which component changed since the earlier Fedora installations, or that Fedora, a USB controller, or the token firmware was responsible.
After switching to the Yubico keys, I reported no further issues. Each key succeeded in tests across all four physical USB ports. I also alternated which key unlocked the disk and which authenticated at the desktop. I did not record a formal trial count, so these results should not be converted into a percentage or a blanket endorsement of every device from one vendor.
Tested path
Yubico keys
uTrust keys
Disk enrollment
Both completed
Both completed
Repeated disk unlocking
No failures reported
Intermittent failures reported
Account and privilege authentication
Reported tests passed
Successful tests, with an earlier transient login problem
Scope
One laptop and one day of lab testing
Same machine and session
Recovery deserves its own test
I also booted without a connected key. The initial prompt still asked for a token PIN. Empty Enter did not immediately reveal the passphrase option, and Escape only switched the display between graphical and text views. In the successful attempt I entered the usual token PIN with the key absent, waited, and eventually received the disk-passphrase prompt. The strong disk passphrase unlocked the volume, and the account-password fallback let me log in.
The delay was not measured, and I did not test forgotten-PIN recovery. I would not describe this as an instant or universal fallback shortcut. The useful result is narrower: recovery without the physical key worked in this session using the retained disk and account secrets.
Late insertion after reaching the boot prompt was less dependable than having the chosen key plugged in before power-on. That became my preferred test workflow. It is an observation to investigate further, not a claim that every key will hot-plug reliably or that a particular controller caused the difference.
Extending the lab to SSH
On November 17, 2026, following Gregory’s editorial suggestions, I updated the Fedora workstation and extended the lab to test SSH from a Windows computer at home. Using OpenSSH’s native FIDO2 support, I authenticated with a Yubico security key connected to the Windows computer, entering its PIN and confirming with a touch. A fresh reconnection also succeeded without entering the Fedora account password. This extension tested one SSH credential over the local network; server password authentication remained available. The companion lab guide 1 includes the commands, screenshots, and results in an optional SSH section.
A useful result with work still to do
For ordinary use on this lab machine, the two Yubico keys gave me the PIN-and-touch experience I wanted. Password fallback remained available, and sudo still applied its normal authorization and caching behavior. Pulling out a key did not configure automatic locking. No settings were changed to make the computer trust every administrative request.
Before extending this to another environment, I would require protected off-device recovery material, a lost-key revocation plan, and testing after updates. Header restoration, key resets, slot deletion, and every future kernel were outside this session. The home-directory PAM mapping also needs to be considered in any more demanding threat model, because control of that account’s files is already significant access.
The result is encouraging precisely because it was worth testing past the first success. I am grateful to the Fedora community and all of the contributors behind systemd, cryptsetup, dracut, authselect, PAM, libfido2, and the hardware tools. Their shared work made this experiment possible. I hope this follow-up helps other users build a careful lab, test recovery, and report both the good results and the problems.
Rose, S., Borchert, O., Mitchell, S., & Connelly, S. (2020). Zero trust architecture (NIST Special Publication 800-207). National Institute of Standards and Technology. https://doi.org/10.6028/NIST.SP.800-207
The original installation and local-authentication tests took place on November 3, 2026. The SSH extension was completed on November 17, 2026. External references explain the tools and security concepts; they do not independently reproduce or certify these results.
I performed the installation, configuration, and hands-on hardware testing and documented the results myself. AI tools assisted with technical reference research, organizing photographs, drafting, and editing. The findings, conclusions, and any errors remain my responsibility.
Modern Linux systems still have cron available, but I think people should stop using it.
Don’t get me wrong, it works perfectly for what it was designed for, but I think it is suboptimal for the majority of tasks, and keeping scheduled tasks in multiple places is a very confusing way of handling them.
I think that in modern Linux systems, using Systemd to substitute cron is the best approach.
In fact, Systemd can perform the same scheduled activities as cron.
Still, it is integrated with all Systemd facilities, so the experience is better and execution is more robust.
In fact, Systemd can order jobs after network initialization and require filesystems to be mounted.
It also handles logging automatically, ensuring logs are consistent with other system logs and easier to find and consult when needed.
Let’s keep it security focused this week. Have a look at Sebastian Bergmann’s “The Wrong Crash” post and the research into AI supply chain leaks.
Quote of the Week
Queue theory in math tells us that as utilization approaches 100%, lead times approach infinity—in other words, once you get to very high levels of utilization, it takes teams exponentially longer to get anything done.
Fedora Infrastructure team will be applying updates to servers and rebooting them.
Many services will be affected, most should only be down for a short time as their particular resources are rebooted HOWEVER some will be upgraded to F45 from earlier releases and may take a bit longer.
The family took time off from local commitments and took a whirlwind road trip down to Starbase, TX. We have been there once before, but this time was special, because we timed it just right to see Starship Flight 15. We took only a few sightseeing detours this time, so the 3000km each way were on an optimal route.
I cannot compete with the army of pro photographers who set up near the launch site, or the public viewing beaches, but here are a couple of our pictures. Our little family could not compete with the many hundreds of people who made pilgrimage right to the launch pad hours before. Our little Tesla could not compete with the apocalypse of Cybertrucks on site and all around. But no matter, it was not about competition but about witnessing the starship launch & catch. And those were superlative, right on time and right on target. (Booster catch was called off for a tech glitch, certainly fixed next time.) Spaceflight has just become cheap.
This trip was heavily AI-assisted. Our Hermes AI cluster planned the trip, with some weird timing constraints like matching drive arrival times against venue hours. It kept a detailed diary while en route, based on our positions and our frequent photo snaps & caption blurbs, and synthesized summary maps like the above. It helped with all sorts of minor searches and chores while we were away. And then there was the car: full-self-driving almost the entire way, day & night, good weather & bad, city & highway. It got us out of a few near-accidents (others' fault). The car is still fun to drive by hand, but so cozy when monotonous or confusing road hours are delegated to the machine. Even during the longest driving sprints, charging was fine: 15 minutes' rest/charge after 2 hours' drive worked well for both human and machine.
A technically minded person within travel distance should make such a trip. Seeing skyscrapers rocket then fall then hover will inspire you.
Release Candidate versions are available in the testing repository for Fedora and Enterprise Linux (RHEL / CentOS / Alma / Rocky and other clones) to allow more people to test them. They are available as Software Collections, for parallel installation, the perfect solution for such tests, and as base packages.
RPMs of PHP version 8.5.13RC1 are available
as base packages in the remi-modular-test for Fedora 43-45 and Enterprise Linux≥ 8
as SCL in remi-test repository
RPMs of PHP version 8.4.23RC1 are available
as base packages in the remi-modular-test for Fedora 43-45 and Enterprise Linux≥ 8
as SCL in remi-test repository
ℹ️ The packages are available for x86_64 and aarch64.
ℹ️ PHP version 8.3 is now in security mode only, so no more RC will be released.
As I’ve endured LLMs taking over all facets of the internet and peoples’
minds, I’m struck by how important it is that human endeavors retain
friction. Friction is what spurs us into problem solving. Friction
frustrates us, but its presence leads to reward and accomplishment once
overcome. Yet from the viewpoint of marketing departments, friction should
be removed regardless of cost (financial or otherwise). Society has been
fooled into thinking that convenience and a frictionless experience
is objective improvement over prior practices. Don’t bother calling a
travel agent, have ChatGPT put the itinerary together for you. It’s a
waste of time to build a data-backed chart for tracking progress at work,
just use Claude to create one everyday. Don’t waste your time writing
documentation, Copilot can answer all your questions.
You get the idea.
Societal pressure to rely on an LLM for everyday tasks (rather than
my brain) has spurred me on to reconsider the tools I depend on for
my day to day work and computing needs, many of which reduce friction
themselves. I don’t use LLMs, so I’m already good there. Today let’s
focus on language servers, their relationship to text editors, and other
text editor related tools.
Language Servers
Language servers are programs that read source code. They provide language
features (such as auto-complete, “go to definition”, find all references,
etc.) for one’s text editor or IDE to use. Microsoft started the Language
Server Protocol
so that language servers and code editors had a standardized format for
communication. No longer were you limited to using Eclipse or JetBrains if
you wanted intelligent language features for reasoning about your project.
These features can be extremely useful especially for those new to a
project, or new to a programming language! Receiving instant information
about a function/method signature as you’re typing sounds useful. Having
the ability to quickly open a new window in your editor for a class
definition is helpful. One can reason about a codebase quickly.
I started exploring and using language servers in early
2023 when I switched from Vim to
Neovim. Exploring LSP was the main driver for my
using Neovim. I was a happy Neovim and language server user once I got
it all setup. I felt so swanky with all this magical new power at my
finger tips. Wow, code that can understand my code?! I’ll be unstoppable.
Fast-forward to early 2026; LLMs are everywhere. Every third programming
YouTuber is claiming that we never need to write code by hand again. Let
your agents do it all. Watching the “AI psychosis” phenomenon spread
across the software industry, my peers included, was alarming. Such a
deep dependency on these magic word machines had quickly developed. You
could tell that less thinking was occurring, replaced by “the chatbot
said to do it.” I’m trying to prevent this post from becoming an AI
rant, but I do want to provide context for why I developed a curiosity
to step away from development tools of convenience. What effect would
that have? Any? I paid attention to my own tool usage.
To my surprise, the language server – especially auto-complete – was
affecting how I programmed. In the moment I would be thinking less about
the code I was writing, instead typing a few letters then waiting with
my empty brain to be presented with options of how to continue. I’d be
less familiar with the layout of my own projects, because the language
server made it a breeze to jump around files with no consequence. I had
become dependent on the language server for my projects. That’s not
to say that I could no longer write code, but I was more detached from
the overall workings of the project as a result of the language server
features. The LS took care of the details for me. Why did I need to care.
But I wanted to know and care. I turned off language server
auto-complete. That helped but I was still more distanced from my code
that I wanted. The visual pop-in of other language server features
continued to maintain control of my focus and vision, rather than the
logic of the code in front of me.
Treesitter
Disabling text editor features like LSP and auto-complete
will poorly segue us into my next consideration:
Treesitter. Treesitter
is a library/ecosystem(?) of source code parsers for reading code
to provide editors with better highlighting and text selection
semantics based on a language’s given features and syntax. This is
cool, and it made my source code have more colors, but what did
it really provide me? I spent hours writing some code to install
and maintain treesitter parsers for my minimal Neovim setup because
nvim-treesitter was
no longer maintained 1. There is also the fact that many Treesitter
parses are just random git repos of code spread across the internet that
Treesitter installs and compiles on your machine. The potential for a
supply-chain attack is high.
The nail in my Treesitter coffin was trying to build the latest version
of their command-line tool for Void Linux
across all the different architectures Void supports. Rust
cross-compilation is a nightmare, I now know. As of writing, that pull
request is still
open because I haven’t found a solution. At this point, I was ready to
move away from Neovim to use an editor that doesn’t rely on Treesitter
2. Unfortunately Treesitter has become somewhat of a standard (in my
opinion due to bandwagoning) so that doesn’t leave much left to chose from.
Kakoune
Enter Kakoune. Kakoune is a Vim-ish editor adhering to the Unix
Philosophy. As a result, one gets a editor that is lightning quick and
doesn’t reimplement any features that already exist elsewhere. Plus
it doesn’t rely on Treesitter. Bonus! Additional to the non-features
espoused by Kakoune, I have taken a strong stance to use the editor’s
default settings as much as reasonably possible. This may change over time
but as if writing this post, my Kakoune configuration is considerably
small. For comparison my Neovim configuration and custom code was over
1000 lines of Lua.
Conclusion
It’s important that we repeatedly evaluate the usefulness of the tools
we use, to ensure they’re solving the stated goal and to regularly
guarantee that its positive effects outweigh its negative effects,
but also to check how they affect us as the humans using them. Having
taken my own journey over the past months from fancy LSP-laden Neovim
to a stripped down Kakoune, I can say I’m happier and more engaged than
I was before. I don’t move quite as fast as I did, but that was never
the point 3.
I encourage you to occasionally pause to ask yourself, “why am I using
this? Is is truly helpful to me? Has this affected my thought processes
in any way?” Taking your own journey of evaluation and self-reflection
may reveal that nothing needs to change. Or you just might discover a
more rewarding world when there’s a taste of added friction.
Nvim-treesitter has since been unarchived and continues to
receive maintenance and code changes. ↩
For new Linux users the terminal can be like the Sphinx, quiet, mysterious, and offering no help to those who do not already speak its language. Here we'll show you how to get comfortable with the terminal by using some common commands to analyze a text file of words used by the popular online game, Wordle.
This analysis has real tasks to work on, giving you hands-on experience with the Linux command line. You'll be able to apply this experience to also work with logs, configuration files, and search for text inside files. These are fundamental skills an experienced user needs. Plus, you'll have some fun with Wordle.
I've Been Living Under A Rock. What's Wordle?
Wordle is an oddly addictive word game hosted by the New York Times. The goal of Wordle is to guess a five-letter word in no more than six guesses. The rules are simple. Guess a five-letter word. Wordle will mark letters that are not used, letters used but in the incorrect location, and letters in the correct location with different colors. Guess another word using the previous word's clues. Keep guessing until you've guessed the word or run out of guesses.
Wordle uses a curated list of words, so not every possible five-letter word can be a Wordle word. Offensive words, words with special characters or spaces, words using non-American spellings, and names (words that should be capitalized) are not used. Only certain plural and past tense words are accepted. Take a look at the full Wordle rules. These word rules narrow down possible Wordle words from some 20,000 dictionary five-letter words to about 2,500 words in the curated list.
Can the tools shown here be used to cheat at Wordle? If you play against others, the answer is yes. Being smart and clever about games is fun. Cheating is not fun....for anyone. Use this power for good only.
The Sphinx Speaks - First Look at the Terminal
If you're new to the terminal, let's take a quick tour. The application that let's you access the terminal from your desktop is a terminal emulator. On Fedora Workstation it is called Terminal. Fedora KDE uses a terminal emulator called Konsole. Open your terminal emulator application, and let's take a look around.
At the top left of the terminal window you see the prompt. The blinking cursor shows you where to type commands. The terminal uses software called a shell to communicate with the operating system. The terminal can use different shells, but we're going to use the default shell used by almost all Linux distributions, bash. You are probably already using bash, but let's confirm. To check your shell, type this command and hit Enter:
user@host:~$ echo $SHELL
/bin/bash
If the response is /bin/bash, you're set. If you get other responses (e.g., /bin/csh, /bin/ksh/, /bin/zsh), you're using a different shell. You may have problems with some of the tools we'll use. You can still follow along and run most of the commands, but you may encounter some issues.
The echo command just tells the terminal to "echo back" the item ($SHELL) to you. The item in question is a variable the system uses to hold the location to the preferred shell of the logged-in user.
Assuming you are using bash on Fedora, your prompt should look something like this:
user@host:~$
On some other Linux distributions, you may see a prompt that looks like this:
[user@host ~]$
Either way, the prompt gives us four pieces of important information:
The username of the current user in to the terminal. In the example this is "user".
The hostname of the system. In the example the hostname is "host".
The current working directory is user's home directory (~). You will see the tilde (~) used frequently in the terminal. It represents the /home/user/ directory. Remember, there's no place like ~.
The $ at the end tells us we currently have non-root permissions. We're not going to make any system-wide changes, so this is perfect for us. It also indicates the shell is ready for more input.
Put the Terminal to Work - Create a Workspace
Let's make a directory we can store our data in. We'll assume you have a standard desktop install with pre-made folders like Documents, Music, Pictures, Downloads, etc. We're going to put our work in the Documents folder. Inside the Documents folder, we're going to make a new folder called 'wordle'. We use the terms 'folder' and 'directory' to mean the same thing. Old school Linux users prefer 'directory' as that is how they are referred to on the command line. Keep an eye on your prompt to see how it changes when you change directories.
First, change directories (cd) to the Documents directory:
user@host:~$ cd Documents
Now, make a new directory (mkdir) called 'wordle':
user@host:~/Documents$ mkdir wordle
Change directories (cd) to 'wordle':
user@host:~/Documents$ cd wordle
Your new working directory should be /Documents/wordle. Let's confirm that. Tell the terminal to print the name of the current working directory (pwd):
Knowing which directory the terminal is in is important. The commands you issue will happen inside the current working directory unless you explicitly tell the command to use a different directory. Everything we're going to do should happen inside this directory.
Anytime you need help with a command, type the command followed by a space and --help to get a brief note on the basics of the command. Most linux commands have these flags you can use to modify the basic command. Some flags, like --help, are whole words and prefixed by two dashes. Other flags are just one letter preceded by a single dash. These flags are known as options. Try it with:
user@host:~/Documents/wordle$ pwd --help
You can also try using the --help option with other commands:
mkdir --help
Now that you have your workspace set, we won't show the whole prompt. We'll show only the commands issued, like the one above.
Practice with the --help option as much as you want with the commands we've already used - cd, mkdir, pwd. Warning: If you try
echo --help
Well, see what happens. To get the help text for echo, use:
help echo
If you move out of the directory or close the terminal, you can easily get back to our 'wordle' directory by issuing the command:
cd ~/Documents/wordle
Let's Go Surfing - Finding a Wordle Word List to Analyze
Your Linux system comes with its own dictionary. It is a list of words applications can use to do things like check spelling. Wordle uses a curated word list, so the system dictionary won't be much help. There are many such curated Wordle word lists on the Internet, but you don't need to go searching for one. We've found a good list for you. Just open this link in a new browser tab: https://raw.githubusercontent.com/Kinkelin/WordleCompetition/refs/heads/main/data/official/shuffled_real_wordles.txt
Take a few moments to study the file in the browser. Note the following things:
The first line in the file starts with a #, but the rest of the file is five-letter words (all in lowercase) with each word on its own line. That may seem like a waste of visual space, but this is exactly the type of file Linux loves. Word processor documents, spreadsheets, tables, and columns all make the job of reading the file harder for Linux. This simple text file is perfect for us.
The first line says the file has 2,315 words. Pretty close to the number of curated words used by Wordle.
The words are not in alphabetical order. That might nag at our human sense of order, but it won't affect the analysis Linux will do.
What about letter pairs (th, ou)? How often do they come up? In English, letter pairs are called digraphs. If both lettters are vowels, the pair is called a dipthong (shoutout to English teachers everywhere).
Ok, this is a good list. Let's download it into our workspace.
Back to the Terminal!
Click back into the terminal. Make sure you are in the correct workspace, the directory called wordle. Tell the terminal to download the file.
The command wget is a tool for downloading files from web servers. When the command tells you its done, confirm you have the file in the directory with a ls command. The ls command tells the terminal to list files and directories in a directory:
ls
shuffled_real_wordles.txt
We can also look at the contents of the file in the terminal. The cat (from the word catenate) command will do that, but it has a small hitch. See if you can spot it when we run the command:
cat shuffled_real_wordles.txt
As you can see, the cat command just spits out the entire file contents. And since the file has 2,000+ lines, you can't see the whole thing. We should use the less command.
less shuffled_real_wordles.txt
Aha! Now you see the top of the file, but not the end of the file. The less command shows you just one page of the file at a time. If you want to see the next page, just hit the spacebar or the PgDn/PgUp keys. The down/up arrow keys work, too, but only move one line at a time. You can do this as much as you like until you quit less. Move up and down a few pages and lines using the different navigation key options. To quit less, just tap the Q key. By the way, less is known as a pager command, because it shows output in pages.
One more command we want to use to inspect this file is wc or word counter. wc does exactly what its name says -- it counts words in a file. Try it:
wc displays line, word, and then byte counts. The three numbers match up with our expectations -- 2,315 lines plus a one-line description at the top, for a total of 2,316 lines and 2,335 words. If we want wc to show only lines, use wc -l or for words, wc -w. Try it:
Use wc --help to see how to count characters. We won't use it here, but it may be good to know.
See how that first sentence is keeping us from exactly matching the number of Wordle words? It's going to confuse Linux, too. We don't want that sentence in our analysis, so let's edit our file and get rid of it.
Terminal, Edit Me a Story
A good practice to follow before we edit a file is to make a copy of it first. That will let us have an original copy. In the terminal, we'll do this with the cp (copy command). In this case, we're going to give the command two filenames -- the original name and the new name. Also, let's give our working copy a shorter name:
cp shuffled_real_wordles.txt words.txt
When we get no messages back, we can assume the command worked.
Now we edit our working file with with nano. Nano is the current default editor in Fedora. There are other editors that can be run in the terminal -- vim, emacs, micro, just to name a few. If you want to use a different editor, that's OK. We'll stick with nano here.
nano words.txt
Once you are in nano, there are two important commands to remember. CTRL+O will write/save the file. Nano will ask you to confirm the name. Hit enter. The second command quits nano -- CTRL+X. If you make changes and try to quit without saving, nano will ask you if you want to save changes to the file (Save modified buffers?). You can press Y, N, or CTRL+C (cancel and return to nano), depending on what you want to do.
Delete that first line. Don't leave any blank spaces between the first word and the top of the file. Save the file and exit nano.
Let's check the wc output now:
 wc -lw words.txt
2315 2315 words.txt
Perfect. 2,315 lines and 2,315 words. See how we combined the -l and -w options? Many commands will let us do this. Keep this in mind as you gain experience with the terminal.
Let the Analyzing Begin!
Analysis is an intimidating word that just means asking questions and finding answers about a thing by breaking that thing down into its component parts. Take another look at our word list and its component parts, letters. What questions could we ask about them? Here are the questions we're going to work on in our analysis.
What is the total letter frequency in the possible word list?
What are the most frequent letters at the start of a word?
What are the most frequent letters at the end of a word?
What about letter pairs (th, ou)? How often do they come up? In English, letter pairs are called digraphs. If the letters are both vowels, the pair is called a dipthong (shoutout to English teachers everywhere).
You could easily come up with more questions. Make a note of them. After you get some experience, start hunting for answers on your own. For now, we'll focus on some simple text analysis questions.
I'll Grep You, My Pretty
The grep command's function is simple and powerful. It finds text based on a pattern you give it, and outputs what it finds. It can find exactly what we're looking for, or it can find things that come close to what we're looking for. In fact, grep is going to be the cornerstone of our analysis work, so we should spend some time learning the basics.
You tell grep what you want to find in the file by giving it a pattern or regular expression (also called a regex) and a place to search. Let's say you want to see if the word 'eater' is in our words.txt file. A recommended practice is to put the pattern in quotes, so we'll do that here:
 grep "eater" words.txt
eater
The response shows us grep found 'eater' in the file. Try this one:
grep "eaton" words.txt
grep found nothing so nothing is returned. Remember, Wordle does not use proper nouns, so that makes sense (sorry, Eaton, Ohio).
What if we want to find all of the words with 'eat' in them? Simple enough:
grep "eat" words.txt
treat
wheat
cleat
heath
great
bleat
eater
eaten
cheat
death
sweat
pleat
meaty
Wow! Now we can begin to see the true power of grep.
When we are building our search pattern for grep, we can use special characters called wildcards and anchors. A wildcard is a placeholder for unspecified letters. We can use a dot (.) to represent any single character. The star/asterisk (*) character represents the previous character any number of times, including no character at all. Combine the dot and star (.*) to match any number of any character. Let's try wildcards out to see how they work with grep.
Words with a single character between 'e' and 'at':
grep "e.at" words.txt
begat
elate
Words with any number of (including zero) characters between 'e' and 'at'
grep "e.*at" words.txt
treat
wheat
cleat
heath
great
bleat
eater
eaten
cheat
death
sweat
begat
elate
pleat
meaty
eclat
The "e.*at" pattern matches all of the words the "eat" pattern PLUS begat, elate, and eclat.
Anchors tell grep where we want the search to be focused in a line. We can tell grep to search at the start (^) of the line or at the end of the line ($). This is exactly what we'll need when we check for the most frequent starting and ending letters in our words. Let's search for words with 'eat' at the start of the line in our words.txt file:
grep "^eat" words.txt
eater
eaten
How about words with 'eat' and the end of the line?
The grep command has several available options, but we need to be aware of two of them. If you read grep --help, you'll see that grep has a count (-c) option that reports the number of lines matched by the pattern. If a word has two of the same letter, it will match that, but only count the line once.
 grep -c "a" words.txt
909
The grep command found 909 words that contain the letter 'a.'
The second grep option we need is -o, which prints out every match of the pattern it finds. Given a single line with two matches, the grep -o command prints out both matches. Let's see how it works:
grep -o "a" words.txt
a
a
a
.....
That time we asked grep to print out every occurence of a. It did that dutifully, printing out 'a' more times than we want to count. Let's give grep a little help with a pipe. We'll review pipes in greater detail next, but let's just add one to our last command.
grep -o "a" words.txt | wc -l
979
Here, we took our never ending lines of 'a' and sent them to wc to count. We came up with 979 occurrences. So, we can say that the letter 'a' is found in 909 words, but appears 979 times, thanks to repeated letters in words (e.g., alarm).
Say Hello to My Little Friend(s) -- Pipes and Filter Commands
The pipe symbol (|) tells the terminal to start the pipe process. The pipe tells the first command to send its output to the next command. The second command then receives the input, processes it, and spits it out in its own format. The commands and pipes together are called a pipeline. The commands receiving the output are filter commands. Almost any command can be a filter command, but there are a few commonly used filter commands we want to focus on -- sort, uniq, head, column, and tee. Briefly, here's what each does:
sort orders input. When used with -n, it can sort numbers, and with -r it can do a reverse sort.
uniq identifies and acts on repeated matches. When used with the -c option, it returns the occurence and the number of times the occurence was found.
head just displays the first 10 lines of ouput. The command can be adjusted to show a specific number of lines. head has a brother called tail that works on the last lines.
column formats input into multiple columns. This command is a gem when dealing with a long list of simple outputs.
tee copies output sent to our display and sends it to another location, like a file. It does not supress the output to the terminal. This helps us capture the output in a more permanent way, while still displaying output in the terminal.
Let's build a pipeline as an example
Say we want the output of one of our grep command to appear in alphabetical order, and we just want to see the first 5 lines.
grep "eat" words.txt | sort | head -5
bleat
cheat
cleat
death
eaten
Remember how the command grep -o "a" words.txt just printed out 'a' repeatedly? We piped the number of lines to wc -l to count the lines. The uniq -c does something similar, with a slightly different output:
grep -o "a" words.txt | uniq -c
979 a
The uniq command has the advantage over wc -l of being able to group together and count matching output. That will let us get the output of a grep command using wildcards while keeping an accurate count of each letter.
Let's count all the letters. We can use the (.) wildcard instead of typing every single letter. We'll add head to the end of our pipeline to keep our terminal tidy:
grep -o "." words.txt | uniq -c | head
1 s
1 c
1 o
1 w
1 l
1 w
1 a
1 g
1 e
1 r
What happened? grep sent the uniq command the data for each line. So, uniq told us the word 'scowl' has one 's', one 'c', etc. We want to know the total occurences for letters in all lines, not just the individual letters. We have to insert a sort to arrange the output of grep by letter before it gets sent to uniq. We'll use head to keep from filling the terminal with so much output:
grep -o "." words.txt | sort | uniq -c | head
979 a
281 b
477 c
393 d
1233 e
230 f
311 g
389 h
671 i
27 j
We're getting warm. We see that the letters are listed alphabetically, rather than by order of frequency. Let's throw in another sort. This one will sort the output by frequency or count. Remember to use a reverse number sort, so the letters are listed by order of their frequency, highest to lowest. This time, we want to see data on all of the letters, so let's replace head with column:
grep -o "." words.txt | sort | uniq -c | sort -nr | column
1233 e   729 t   575 n  393 d   311 g   195 w   29 q
979  a   719 l   477 c  389 h   281 b   153 v   27 j
899  r   671 i   467 u  367 p   230 f   40 z
754  o   669 s   425 y  316 m   210 k   37 x
That's it! We have listed letters in our Wordle words.txt file by order of frequency. Let's store this output in a file with the tee command.
We see in the display the same output as earlier. Check the letter-freq.txt file:
cat letter-freq.txt
Bingo! Question #1 of our analysis is complete!
Now we need to answer questions #2 and #3.
Recall they are:
What are the most frequent letters at the start of a word?
What are the most frequent letters at the end of a word?
Since we've already figured out how to get total letter frequency in the file, all we have to do is adjust our grep command to check the first and last letters of each word. As we mentioned before, we can tell grep to do this by using the caret (^) or dollar sign ($) characters in our search pattern. Let's try it first before committing the results to a file.
grep -o "^." words.txt | sort | uniq -c | sort -nr | column
366 s   142 p   111 d   83 w   41 o   23 q   3 z
198 c   141 a   107 m   72 e   37 n   20 k
173 b   136 f   105 r   69 h   34 i   20 j
149 t   115 g    88 l   43 v   33 u   6 y
We now have three files -- letter-freq.txt, starting-letter-freq.txt, and ending-letter-freq.txt -- that answer our first three questions.
Looking For Letter Pairs
In the final part of our analysis, question #4, we want to see which letter pairs are used most frequently. This time, instead of counting each instance of a letter pair, including repeated appearances in a single word, we only want to count the number of words that contain a specific letter pair. Using grep -c, we can create letter pairs once, and then count the number of words that contain that pair. Given that all of our words have only five letters, it's reasonable to conclude that our word count will not be too different from a total letter pair count. The only downside with the word count is that we'll find several letter pairs are not used at all. We can live with that. Let's get to work.
We can make letter pairs right in the terminal, automatically. We'll use a bash function called "brace expansion" to do just that. If you're using a shell other than bash, you'll have to check the documentation to see how your shell does brace expansion.
Brace expansion in bash is designed to generate unique strings given a base string and two or more items in a list. Typically, you'd want to use this to name related files. Here's an example:
A nice feature of brace expansion is that bash understands sequential letter and number braces with a little shorthand trick:
 echo {a..z}
 a b c d e f g h i j k l m n o p q r s t u v w x y z
and
 echo {1..7}
 1 2 3 4 5 6 7
So, bash treats {a..z} as all of the letters of the English alpahabet in order, lowercase, and {1..7} as all numbers 1-7 in order.
How can we apply this to our letter pair problem? Let's try something simple first, like creating all the possible letter pairs that begin with 'a'. How about:
 echo a{a..z}
aa ab ac ad ae af ag ah ai aj ak al am an ao ap aq ar as at au av aw ax ay az
We're on the right track, but we want all letter pairs.
 echo {a..z}{a..z}
aa ab ac ad ae af ag ah ai aj ak al am an ao ap aq ar as at au av aw ax ay az ba bb bc bd be bf bg bh bi bj bk bl bm bn bo bp bq br bs bt bu bv bw bx by bz ca cb cc cd ce cf cg ch ci cj ck cl cm cn co cp cq cr cs ct cu cv cw cx cy cz da db dc dd de df dg dh di dj dk dl dm dn do dp dq dr ds dt du dv dw dx dy dz ea eb ec ed ee ef eg eh ei ej ek el em en eo ep eq er es et eu ev ew ex ey ez fa fb fc fd fe ff fg fh fi fj fk fl fm fn fo fp fq fr fs ft fu fv fw fx fy fz ga gb gc gd ge gf gg gh gi gj gk gl gm gn go gp gq gr gs gt gu gv gw gx gy gz ha hb hc hd he hf hg hh hi hj hk hl hm hn ho hp hq hr hs ht hu hv hw hx hy hz ia ib ic id ie if ig ih ii ij ik il im in io ip iq ir is it iu iv iw ix iy iz ja jb jc jd je jf jg jh ji jj jk jl jm jn jo jp jq jr js jt ju jv jw jx jy jz ka kb kc kd ke kf kg kh ki kj kk kl km kn ko kp kq kr ks kt ku kv kw kx ky kz la lb lc ld le lf lg lh li lj lk ll lm ln lo lp lq lr ls lt lu lv lw lx ly lz ma mb mc md me mf mg mh mi mj mk ml mm mn mo mp mq mr ms mt mu mv mw mx my mz na nb nc nd ne nf ng nh ni nj nk nl nm nn no np nq nr ns nt nu nv nw nx ny nz oa ob oc od oe of og oh oi oj ok ol om on oo op oq or os ot ou ov ow ox oy oz pa pb pc pd pe pf pg ph pi pj pk pl pm pn po pp pq pr ps pt pu pv pw px py pz qa qb qc qd qe qf qg qh qi qj qk ql qm qn qo qp qq qr qs qt qu qv qw qx qy qz ra rb rc rd re rf rg rh ri rj rk rl rm rn ro rp rq rr rs rt ru rv rw rx ry rz sa sb sc sd se sf sg sh si sj sk sl sm sn so sp sq sr ss st su sv sw sx sy sz ta tb tc td te tf tg th ti tj tk tl tm tn to tp tq tr ts tt tu tv tw tx ty tz ua ub uc ud ue uf ug uh ui uj uk ul um un uo up uq ur us ut uu uv uw ux uy uz va vb vc vd ve vf vg vh vi vj vk vl vm vn vo vp vq vr vs vt vu vv vw vx vy vz wa wb wc wd we wf wg wh wi wj wk wl wm wn wo wp wq wr ws wt wu wv ww wx wy wz xa xb xc xd xe xf xg xh xi xj xk xl xm xn xo xp xq xr xs xt xu xv xw xx xy xz ya yb yc yd ye yf yg yh yi yj yk yl ym yn yo yp yq yr ys yt yu yv yw yx yy yz za zb zc zd ze zf zg zh zi zj zk zl zm zn zo zp zq zr zs zt zu zv zw zx zy zz
And there is our letter pair list, all 676 of them.
So how are we going to run all of these through grep? The pipeline commands we used would work, but we would have to manually enter each letter pair as the pattern. We need something to send the output of the brace expansion to grep. And we have just such a solution called a "for loop". Let's take a look at a simple for loop in the terminal:
 for n in {1..5}; do echo $n; done
1
2
3
4
5
What's happening here? We tell bash for each number (n) in the list created by the brace expansion of {1..5}, do the echo command on that number, then finish.
You see that each step in the loop construct is separated by a semicolon. We gave the individual items in the brace expansion a name (n). The n is called a variable, and when we use it again, we refer to it as $n so bash knows it is a variable name.
This is a lot of work going on in one line, so bash allows us to use new lines instead of the semicolons, as shown below. When you hit enter after the first line, bash knows you haven't given it a full command yet, so it goes to the next line, and adds a '>' to the front of the display. When you've given bash a complete command, after you type 'done,' bash goes to work.
 for n in {1..5}
 >do echo $n
>done
1
2
3
4
5
Multiple commands can occur in the loop. We just add them to the list of commands after the 'do', like this:
 for n in {1..5}
 do echo "The number is..."
 echo $n
 done
 The number is...
1
 The number is...
2
 The number is...
3
 The number is...
4
 The number is...
5
As easy as this is to do, it's still a bunch of typing. Any mistakes we make will mean we have to go back and re-type the whole command. We should put it into a file that we can execute without typing the whole thing out.
Welcome to shell scripting!
We could write the script just like we've done in the terminal, but that won't be very readable for humans. Let's use a couple readability tricks for our script. When scripting a for loop, many experienced scripters use this format: for n in {1..5}; do
echo "The number is..."
echo $n
done
We put the "for" and "do" statements on the same line, separated by a semicolon. This lets the reader see a loop is coming, and keeps the list of commands in the format we would use directly on the command line, one command per line. We also indented each command, so they are nestled between the 'for/do' and 'done' statements.
Now we're ready to create a shell script to count letter pair frequency. Let's create a filename called 'lpcount.sh' The '.sh' at the end is called a filename extension. It will tell the terminal this is a script file.
nano lpcount.sh
Add this text to the file:
 #!/bin/bash
for n in {a..z}{a..z}; do
  pcount=$(grep -c $n words.txt)
  echo $pcount $n
done
Save and close the file with CTRL+O, ENTER, CTRL+X. Next, we have to make the file executable. We do this with the chmod (change file mode bits):
chmod +x ctofive.sh
We have our first script! Don't dismiss the script because of its small size. you'll find other situations where short scripts like these can save you tons of time. Experienced users usually have a collection of these home-made scriptlets or snippets to make their work easier. Let's finish up our analysis by using our new script in a pipeline.
First, we just want to test the script to make sure it works. We'll use the head command in a pipeline so we only get the first 10 lines, rather than all 676.
 ./lpcount.sh | head
 0 aa
 29 ab
 52 ac
 49 ad
 1 ae
 18 af
 26 ag
 2 ah
 47 ai
 2 aj
Perfect! Let's run the command again. This time, we'll do a reverse number sort, format the output into columns and send the output of all 676 letter pair word counts to a file.
Question 4 has been answered! Later, you may want to look for starting or ending letter pairs. We've already done starting and ending single letters, so finding starting and ending letter pairs won't be too difficult.
Summary and Next Steps
We took our first steps into the linux terminal and bash by doing some analysis on a Wordle word list. You can easily apply these skills to other tasks, like log and config file reviews. The techniques used here are useful, but in some cases, not optimal. As you learn bash, you'll find better ways to do the simple things we've done here. You also wrote a small program that does something useful. If I've whetted your appetite to do more text analysis, I recommend you learn a dedicated language like Python or Perl. As powerful as bash scripting is, those two programming languages will outstrip bash in capability and speed very quickly when it comes to text analysis.
Retour sur la migration technique du forum de Fedora-fr vers Flarum 2 : découverte du nouveau module Deck, délégation des files d'attente à fof/horizon et Redis, intégration du package manager, logs d'audit et conformité GDPR.
Across the various Fedora working groups, a major focus this week was the transition between release cycles, heavily featuring post-release cleanup and monitoring for Fedora 45 alongside active planning for Fedora 46, including proposals like the removal of the legacy DNF4 stack. Infrastructure and tooling migrations were another prominent shared theme; multiple teams—including Docs and Gaming—are migrating references from Pagure and GitLab to Fedora Forge, while the Council and FESCo are actively investigating Forgejo-based replacements for the retiring Bugzilla issue tracker. Security and system maintenance also drove significant cross-team collaboration, highlighted by a coordinated infrastructure outage for server updates, the removal of inactive packagers, and widespread vulnerability patching in the Rust and CoreOS groups. Finally, community engagement teams like Mindshare and Ambassadors are aligning their efforts to finalize proposals, funding, and volunteer coordination for major upcoming open-source conferences, particularly FOSDEM 2027 and FOSSASIA 2027.
Contributors should be aware of a planned infrastructure outage scheduled for November 19, 2026, at 22:00 UTC, which will last approximately four hours to accommodate server updates and reboots. Additionally, as part of routine maintenance for the Fedora 45 development cycle, 161 users are being removed from the packagers group due to inactivity. For those looking to get more involved, the latest Fedora Podcast (Episode 064) not only discusses the recent Fedora 45 release but also highlights several upcoming engagement opportunities for Fedora 46, including writing release notes, participating in test weeks, and submitting wallpaper ideas.
In broader community news, two new guides have been published to help users enhance their desktop experience. The first outlines a method to install the official Claude Desktop Linux beta on Fedora, utilizing a script to safely extract and run Anthropic's .deb package without root privileges. The second introduces TuxTalk, a free, locally-hosted voice dictation tool for Linux that allows users to dictate text directly into any application, terminal, or document without requiring an account or sending voice data off-device.
Council
This week, the Council addressed trademark usage for a new Fedora-derived distribution called Bibim, clarifying that the Fedora Remix logo is the intended branding for such projects, which led the creators to adopt the Remix guidelines instead of seeking a trademark variance (Trademark question: using the Fedora logo for a Fedora-derived distribution (Bibim)). Additionally, a significant community discussion began regarding the future of Fedora's issue tracking system in light of the upcoming retirement of Red Hat's hosted Bugzilla, with members debating the transition to a Forgejo-based system versus maintaining a community Bugzilla instance (What issue tracker do we want to use for Fedora 90?).
Contribution opportunities
Contribute to creating a script or packaging solution that simplifies converting a standard Fedora release into a Fedora Remix.
Help design a specific landing page for Fedora Remix users to encourage upstream contributions.
Submit concrete proposals, gather requirements, or write user stories for Fedora's future issue tracking system transition.
This week, FESCo held one meeting and processed numerous tickets, primarily focusing on approving System-Wide and Self-Contained Changes for upcoming Fedora releases. Key discussions centered around the ongoing investigation into replacing Bugzilla, managing the removal of unmaintained NetworkManager VPN plugins, and extending the F45 FESCo election voting period to accommodate the holidays. FESCo also formally set the EOL date for Fedora 43.
The Packaging Committee focused this week on updating the Emacs packaging guidelines to support the built-in package management system in recent versions of GNU Emacs. This includes discussing and merging changes that provide new RPM macros and dependency generators for Emacs packages. Additionally, new tickets were opened to discuss allowing Emacs add-ons in RPM subpackages (Issue 1581) and marking up spec templates as source code (Issue 1582).
Decisions
The committee approved and merged PR#1577 (associated with Issue 1577), which introduces new RPM macros and dependency generators for Emacs packages, with plans to resolve minor formatting and Unicode issues post-merge.
The Mindshare group focused on upcoming conference preparations and deadlines. Reminders were issued for FOSSASIA 2027, noting the November 19 deadline to update the event wiki and November 29 for talk proposals. Additionally, a final call for financial assistance applications for FOSDEM 2027 was made ahead of the November 15 deadline. Community members also briefly connected regarding attendance at SFSCON 2026.
Decisions
Future FOSDEM financial assistance requests will transition from using the Wiki to a dedicated application form to better capture budget details and applicant motivations (URL).
This week, the Fedora Join group received introductions from two new prospective contributors. Fardeen Khan introduced themselves as a developer and Fedora advocate looking for guidance on which teams to join. Lutz Weber also introduced themselves, expressing interest in starting with Quality Assurance (QA) and eventually contributing to the Python SIG and software packaging.
Contribution opportunities
Guide Fardeen Khan in finding a suitable team to contribute to, utilizing their development and ethical hacking background.
Welcome Lutz Weber and help them get started with the QA team and the Python SIG.
This week, the Ambassadors group focused on coordinating Fedora's presence at upcoming major open-source conferences. Reminders were issued for approaching deadlines regarding event proposals, talk submissions, and financial assistance requests for both FOSDEM 2027 and FOSSASIA 2027. Furthermore, community members discussed potential informal meetups at the South Tyrol Free Software Conference (SFSCON).
This week, the Workstation / GNOME group addressed several critical system behavior and packaging issues. Key discussions included a bug in GNOME 51's GDM that disables initial fingerprint login—breaking Fedora's authselect and oo7-daemon workflows—and a Btrfs metadata exhaustion issue prompting calls to reconsider auto-balancing defaults. Additionally, users reported a crash in pdftotext when handling certain PDFs, which has been forwarded upstream.
The migration to replace gnome-keyring-daemon with oo7-daemon as the default secret service provider was completed and the ticket was closed. (Issue #506)
This week, the KDE group focused on resolving user-reported issues with recent Plasma updates and discussing future package replacements. Community members actively addressed a shutdown hang bug in Plasma 6.8 by providing unofficial fixes via COPR and pull requests for Qt, while also testing an unofficial build of Plasma 6.8.3. Additionally, discussions clarified the removal of X11 sessions in Fedora 44 and the expected weekly cadence for automated Discover updates on Kinoite. On the development front, new requests for enhancements (RFEs) were filed to replace kwalletmanager with KeepSecret and to remove live-system-only packages during Plasma Setup to save disk space. The ongoing effort to replace kwallet with oo7-daemon was deferred for KDE due to integration challenges.
Decisions
The replacement of kwallet with oo7-daemon has been deferred for KDE variants due to integration issues and a lack of time (URL).
Contribution opportunities
Test the unofficial COPR for KDE Plasma 6.8.3 on Fedora 44 and 45 and report any issues in the forum thread.
Test the Qt 6.11.2 COPR containing the cherry-picked fix for the Plasma 6.8 shutdown hang issue on Fedora 44 and 45 (URL).
The Server working group met this week to discuss ongoing projects and potential changes for the upcoming Fedora 46 release. Key discussions centered around the 'Strengthening Server Updates' project, which was postponed to allow for further testing, and the future of Single Board Computer (SBC) images. Additionally, a community member published a comprehensive and highly successful test report detailing the upgrade path from Fedora 44 Server to the Fedora 45 release on a 2010-era machine, confirming excellent stability with no regressions.
Decisions
The working group agreed to evaluate switching the Single Board Computer (SBC) image to GPT/EFI and dropping Raspberry Pi 3 support for Fedora 46. (URL)
The group decided to keep NetworkManager for the time being rather than switching to systemd-networkd, citing issues with split DNS on virtual machine hosts and its utility in home lab setups. (URL)
Working group members agreed to catch up on outstanding tasks for the Strengthening Server Updates project and revisit the topic on November 25, 2026. (URL)
Contribution opportunities
Help is needed to test the procedures for the Strengthening Server Updates project and start a post-installation how-to style article.
Contributors with image building experience are invited to assist in evaluating and implementing the switch of the SBC image to GPT/EFI, which involves updating kiwi definitions.
This week, the Infrastructure team focused heavily on resolving service disruptions and preparing for an upcoming mass upgrade. Bodhi experienced significant load and timeouts due to aggressive scrapers, prompting the team to implement mitigations like blocking specific RSS endpoints and deploying a Valkey backend for caching. The team also addressed sporadic 404 errors for jQuery on the Fedora Forge caused by Varnish mis-caching, and resolved IPA replication issues after an OS upgrade on ipa01.
Additionally, a planned outage for mass updates and reboots was scheduled for November 19th, which will involve upgrading several servers to Fedora 45. The team also investigated a sophisticated phishing campaign targeting mailing list administrators and welcomed several new contributors to the group.
The Release Engineering team focused on post-release cleanup for Fedora 45, including resolving an issue with missing torrents for several Labs ISOs that were absent at release time. The team also addressed an out-of-date Fedora 45 COSMIC Atomic reference and handled routine package unretirements and SCM requests, while monitoring and unsticking the package signing service. Additionally, preparations for the Fedora 43 End of Life have begun.
Decisions
Fedora 43 End of Life is officially set for December 2, 2026, aligning with FESCo and existing policies (Meeting, Ticket #13588).
Feedback is requested on a proposed enhancement to track build-time dependencies in orphan reports to help downstream tools differentiate between runtime and build-time broken dependencies.
The Quality team monitored the recent release of Fedora 45, noting a smooth rollout with no major regressions, which was corroborated by a detailed community server test on older hardware. The team is now transitioning focus to Fedora 46, reviewing upcoming system-wide changes, and continuing to document common issues for Fedora 45. Additionally, the KDE Plasma 6.8 test days were launched and actively promoted across the community.
Decisions
Christopher Boni volunteered to send out the call for upcoming Test Days (Meeting log).
Bug 2538553 was published to the Fedora 45 Common Issues, while bugs 2560255 and 2537131 are being held for further investigation before publication (Ticket #952).
Contribution opportunities
Participate in the KDE Plasma 6.8 Test Days running from 2026-11-09 to 2026-11-15 by testing and submitting results.
Help is requested to investigate a navigation test failure in openQA where os-autoinst fails to recognize screen changes during Tux Racer gameplay (Ticket #954).
This week, the Websites and Apps team discussed the future of Fedora Magazine's hosting, prompted by a potential end of WP Engine support by the end of 2027. Conversations explored migrating from WordPress to a static site generator (like Nuxt or Hugo) paired with Decap CMS, or potentially using Discourse as a backend, though challenges remain regarding content conversion and comment integration. In the forums, a user reported that Fedora's wifi login detection domain is on the HSTS preload list, breaking captive portal detection, and suggested using a dedicated, independent domain. Additionally, the team handled a new collaborator request and tracked a deprecation warning for the @comark/nuxt module in the fedora-websites-3.0 repository.
Contribution opportunities
Help is needed to explore and draft a strawman proposal for migrating Fedora Magazine off WP Engine to a static site or alternative CMS before the end of 2027.
This week, the Design team received a new request to create a "Fedora loves GNOME" sticker for distribution at upcoming conferences such as FOSDEM. Additionally, ongoing work continued on the community involvement poster, with the contributor using AI-generated feedback to identify and resolve typography, spacing, and alignment issues. In the background, several automated repository actions failed in the design/backgrounds repository, and the weekly team meeting appears to have been cancelled.
Contribution opportunities
A graphic designer is needed to create a print-ready PDF for a "Fedora loves GNOME" sticker to be distributed at events like FOSDEM.
Contributors can help troubleshoot and fix the failing Update README.md automated actions across multiple branches in the design/backgrounds repository.
This week, the Docs team focused heavily on migrating infrastructure references from the sunset Pagure and GitLab to Fedora Forge. This massive cleanup spanned multiple repositories, resulting in updated team documentation, build scripts, templates, and Quick Docs. The migration also resolved a bug in the translated builds by pointing the asciidoc-keywords repository to Forge. Additionally, discussions are underway to establish a Quay organization for hosting the team's CI container images.
The 'How to edit files on the Pagure Web UI' guide has been officially retired and replaced with the Fedora Forge guide.
The oo7 feature for KDE has been delayed and will not be included in the Fedora 45 Release Notes.
The default branch for site-builder and related translation scripts has been officially switched to main, and the legacy prod branch will be deleted (Ticket 77, Ticket 58).
The kernel testing guide has been updated to recommend using grubby and custom buildids instead of overwriting existing packages, preventing conflicts with standard Fedora updates (Ticket 1087).
Contribution opportunities
Team Decision Needed: Determine the future of the Publish RPMs on Copr Quick Doc, as its example repository was lost in the Pagure sunset.
Team Decision Needed: Clarify what permissions the docs-admin and docs FAS groups grant on Forge to update the team charter.
Contributor Opportunity: Help perform a full script sync for docsbuilder.sh to update it to the new Forge docs-template script format (Ticket 72).
This week, the COPR team successfully executed a planned infrastructure outage to update machines to the latest packages. The outage was brief, and services were quickly restored. In discussions, the team addressed intermittent Bodhi outages affecting builds and identified an ongoing issue where internal messaging changes at Red Hat have broken the Fedora review bot. Additionally, the team clarified that some group-owned projects that missed the initial Pulp migration will be queried and migrated once the current batch of owners is finished. Maintainers also provided guidance on packaging non-crates.io Rust applications, clarifying the scope of rust2rpm.
Decisions
Executed a planned infrastructure update for COPR on November 12, 2026, temporarily halting build queue processing and Frontend/Web-UI task acceptance (Mailing List).
Group-owned projects that missed the initial Pulp migration will be migrated in a final sweep after the last batch of individual owners is completed (Matrix Chat).
Deferred modifying the PR input schema to a follow-up PR, opting to merge the current PR as-is to maintain stability for both string and list variants (Matrix Chat).
Contribution opportunities
Help improve the Fedora documentation for packaging non-crates.io Rust applications, specifically by making the manual .spec file template more prominent for inexperienced packagers.
Investigate and help resolve the bazelisk build failure on Rawhide, which currently fails despite building locally.
The EPEL team successfully completed the retirement of EPEL 10.2 and switched EPEL 10.3 to build against the newly released RHEL 10.3. Additionally, an EPEL 9.8 archive snapshot was created in response to the RHEL 9.9 release.
Other activities included delivering an RPM packaging workshop at the Texas Linux Fest, ongoing efforts to package Mailman 3 and Incus for EPEL 10, and closing the investigation into ffmpeg CVE-2025-59734 as it could not be reproduced.
During this week, the Atomic group focused heavily on system update mechanisms, configuration management, and security. A recurring theme was the handling of file merges and updates across different system directories (/etc vs /var), specifically addressing how to safely regenerate certificates, crypto-policies, and appstream caches during system finalization or boot. Other significant activities included resolving a stalled update pipeline for the Fedora Cosmic-Atomic image and addressing compatibility issues with the new RPM v6 package format in rpm-ostree. The group also initiated discussions on improving the security of sealed images against CVE-2026-121876 by restricting auto-mounted partitions, and continued tracking the long-term goal of migrating away from nss-altfiles.
Decisions
Fixed the stalled Fedora Cosmic-Atomic updates by correcting the release engineering scripts, allowing users to receive the latest nightly builds and updates.
Determined that the rpm-ostree installation failure for RPM v6 packages (like Google Chrome 157) is an upstream issue; users are advised to use Flathub or hold back the update as a workaround (Ticket 138).
Decided to run /etc-only updates (such as ca-certificates, crypto-policies, dconf, and SELinux) in advance at finalization time to avoid boot delays, while acknowledging that /var-dependent updates like mandb and appstream cannot be pre-run (Ticket 145).
Contribution opportunities
Investigate and define default restrictive systemd image policies for sealed images to mitigate CVE-2026-121876.
Help design a migration path and build images to transition away from nss-altfiles to standard systemd-sysusers or JSON records (Ticket 87).
This week, the CoreOS group held a meeting to review the Fedora 46 Release Schedule, noting that Rawhide development has begun and that change proposals requiring mass builds or system-wide changes are due in December. In community discussions, a proof-of-concept for live kernel takeover on Fedora bootc using kmorph was shared, demonstrating a potential path forward for rebootless kernel updates.
Ticket activity was high, with 17 tickets addressed. Notable resolutions include a fix for a systemd-journald failure on ppc64le, the rollout of a patch for the CVE-2026-98432 TCP use-after-free vulnerability across multiple streams, and the resolution of an rpm-ostree package download issue in Konflux hermetic builds. Ongoing discussions include a proposed adjustment to the end-of-year release schedule to accommodate holidays and resolving SELinux denials for podman-remote socket connections.
Decisions
The community agreed to migrate the automated engineering newsletter repository to the official CoreOS organization (Issue #2240).
This week, the IoT group addressed a system upgrade issue where a user was unable to perform further updates after upgrading to Fedora 45 due to a missing GPG public key. The problem was traced to an outdated GPG key path in the ostree remote configuration that had not been automatically replaced during the upgrade. The user successfully resolved the issue by manually updating the path to the correct directory.
Decisions
The maintainers decided to close the GPG public key upgrade issue as an isolated incident, leaving the ticket available as a reference for any other community members who might experience the same configuration problem (Issue #143).
The Alternative Images group met on November 12 to discuss the status of this quarter's image releases, which are currently delayed due to the setup of a new omni repository for RISC-V. The team expects to release the standard images shortly and is actively developing bootable aarch64 raw images for CentOS Stream 10. Additionally, the group noted that kiwi has been updated to version 11.x in EPEL 10, which integrates the stackbuild and boxbuild plugins directly into the core. In broader news for the Linux community, the CentOS ISA SIG is building a Fedora Omni kernel monthly to ensure compatibility across almost any RISC-V machine. The group also plans to triage their migrated GitLab issues to clear out older, closed items.
Decisions
The CentOS ISA SIG decided to create an omni repository for RISC-V, which will include a Fedora Omni kernel built monthly to support a wide range of RISC-V hardware (Meeting Log).
The group decided to roadmap the production of both live media and raw disk images for RISC-V for a future quarter, pending the availability of necessary EPEL packages (Meeting Log).
It was decided to formally retire the kiwi-boxed-plugin and kiwi-stackbuild-plugin packages in EPEL 10, following the EPEL Retirement Policy, as their functionality is now integrated into the core of kiwi 11.x.
This week, the AI group saw activity across package reviews and AI tooling. A contributor proposed a review swap for a stack of packages including parrotia (a local transcription tool using Whisper) and its dependencies, python-darkdetect and python-customtkinter. In the Matrix channel, discussions covered the Fedora AI contribution policy regarding LLM usage in source code, an AI skill for converting Markdown to Gutenberg-ready print, and a fix for a ROCm upgrade issue between Fedora 44 and 45. Additionally, a new package review request was opened for agent-skills.
Contribution opportunities
A contributor is seeking a package review swap and a sponsor for three packages: python-darkdetect, python-customtkinter, and parrotia (link).
Testing and karma are requested for a fix addressing the Fedora 44 to 45 upgrade issue with ROCm (link).
A package review is requested for agent-skills (link).
The Fedora RISC-V group spent significant effort debugging a severe CPU lockup issue specific to the SpacemiT K3 SoC when building Rust with the RVA23 target for ELN (Ticket 40). After extensive testing, contributors identified that the lockup occurs when the CPU speculatively fetches instructions from unmapped code pages. A reliable workaround was found by increasing the page fault size (echo 2097152 > /sys/kernel/debug/fault_around_bytes), allowing multi-core Rust builds to complete successfully.
In other developments, a bug in the GCC build system's multilib configuration causing incorrect rva23u64 target paths was identified. The team also investigated KVM guest initialization failures on the K3 SoC when using QEMU with -cpu max (Ticket 39), noting that -cpu host with EDK2/OVMF bypasses the crash. Additionally, the Titan devicetree was merged into a maintainer tree, paving the way for full usability with the generic v7.5 kernel, and a workaround for a Titan EDK2 boot bug was confirmed.
Decisions
Implemented a temporary workaround to increase fault_around_bytes to 2 MiB on K3 builders to prevent CPU lockups during Rust compilation (Ticket 40).
Identified that the target-lexicon crate in several Rust packages (e.g., keylime, tss-esapi) needs to be bumped to at least version 0.13.5 to properly support the RVA23 target.
Determined that QEMU KVM guests on the K3 SoC currently require -cpu host and EDK2/OVMF to boot successfully, as -cpu max causes instant initialization failures (Ticket 39).
Contribution opportunities
Help is needed to update the target-lexicon crate dependencies in various Fedora Rust packages (such as keylime and tss-esapi-sys) to support RVA23.
Contributors with access to JTAG hardware for the SpacemiT K3 (e.g., CoM260) are encouraged to help capture low-level CPU traces to find the root cause of the speculative fetch lockups.
Assistance is welcome in testing and refining the QEMU/KVM ACPI boot combinations across different RISC-V hardware platforms to document what virtualization configurations work reliably.
The Gaming group focused on infrastructure and documentation updates this week. Specifically, they completed a migration effort to update repository links and workflows, transitioning references from Pagure to the new Fedora Forge. This included updating the issue tracker links and refining the README with instructions for the Forge PR workflow and site-builder previews. Migrate links from Pagure to Fedora Forge
This week, the Perl group primarily focused on package updates and architecture support. Steve Traylen submitted and merged multiple pull requests to update perl-SQL-Abstract to version v2.000003 and bump the EPEL 8 build post-unretire. Additionally, Emmanuel Seyman reported that perl-Algorithm-BloomFilter is failing to build on i686 systems, prompting discussions about dropping support for that architecture.
Decisions
Exclude the i686 architecture for the perl-Algorithm-BloomFilter package due to unresolved build failures, unless a fix is provided. Discussed in this thread.
Update the perl-SQL-Abstract package to v2.000003 and bump the EPEL 8 build post-unretire, as seen in PR #11 and PR #10.
Contribution opportunities
Help resolve the build failure for perl-Algorithm-BloomFilter on i686 hosts to prevent the architecture from being excluded, as noted in this thread.
Development for Ruby 4.1 is ongoing, with recent efforts focused on rebuilding the gem ecosystem and addressing Fail To Build From Source (FTBFS) issues against the latest snapshot. A significant change in Ruby 4.1 is the removal of net/pop and net/ftp from the default bundled gems. This removal breaks rubygem-mail and, recursively, Ruby on Rails (RoR) related packages. To mitigate this, a review request for rubygem-net-pop has been submitted. Additionally, maintainers have identified priority FTBFS issues that need resolution, specifically for rubygem-mysql2 and rubygem-ruby-libvirt, which block other major packages like RoR and Vagrant. Upstream Ruby has already fixed the rubygem-ffi FTBFS issue.
Decisions
Maintainers decided not to fix the FTBFS issue for rubygem-narray during the Ruby 4.1 migration, as it is an old package and lacks dependent packages.
This week, the Rust SIG focused heavily on security updates and package cleanups. Major efforts included rebuilding numerous packages to address security advisories in the zstd, zstd-safe, and quick-xml crates, as well as filing bugs for packages statically linking a vulnerable bundled sqlite. Additionally, the group discussed the challenges of packaging crubit for Chromium builds, ultimately advising against shipping the unstable rustc-dev in Fedora, and successfully concluded the retirement of outdated gtk-rs-core and gtk4-rs compatibility packages.
Decisions
The group decided against shipping rustc-dev in Fedora or RHEL due to its reliance on unstable APIs, which impacts the Chromium build process. Alternatives like bundling Rust sources or pre-generating bindings were recommended (URL).
Outdated compatibility packages for gtk-rs-core v0.20 and gtk4-rs v0.9 were officially retired from Rawhide after confirming they were no longer in use (URL).
Stable branches of msedit will diverge from Rawhide and remain at version 1.x to bypass a test failure on s390x, leaving the Rawhide package temporarily affected by the zstd vulnerability (URL).
Contribution opportunities
Maintainers of packages statically linking sqlite (such as flare-im, nodejs-pnpm12, task, and vaultwarden) need to update their packages to address CVE-2026-119375 (URL).
Help is needed to port older packages relying on quick-xml v0.38 and v0.37 to the secure v0.41 release, which may require working directly with upstream developers due to default behavior changes (URL).
The msedit maintainer has an opportunity to fix an s390x test failure on Rawhide to allow the package to receive the latest zstd security updates (URL).
Fedora Package Review Process reimagined - Jakub Kadlčík proposed and prototyped a reimagined package review process using an intermediate forge repository and pull requests, gathering feedback on the approach.
Proposal: Arborists SIG - Gordon Messmer proposed the Arborists SIG to develop branch management software that mirrors upstream releases in dist-git, aiming to streamline container builds.
How can I contact the crypto team? - Steven Emelander from the AWS-LC and s2n-tls teams responded to feedback regarding their configuration scheme, expressing willingness to collaborate with the community.
Packaging proposal: whatsapp-desktop - Abdallah Shehawey provided a refreshed source-only application snapshot for whatsapp-desktop and discussed dependency handling, while seeking an application reviewer and packager sponsor.
Arch specific deps of subpackage in noarch package - Miroslav Suchý encountered a build failure when a noarch package had an architecture-specific dependency, which was resolved by using BuildArch: noarch alongside ExclusiveArch: noarch x86_64 aarch64.
Packages with uninitialized git repositories (no commits) - Samyak Jain noted several package repositories with no initial commits that fail branching operations, prompting discussions on specific cleanups or deletions for the empty repos.
Logwatch and systemd timers - Frank Crawford discussed moving the Logwatch package from using cron to systemd timers, noting that rsyslog might be a better fit for large systems while OpenTelemetry is increasingly preferred.
Dominik 'Rathann' Mierzejewski orphaned the xorg-x11-drv-amdgpu package as they switched to Wayland; it was briefly claimed by Leigh Scott before being orphaned again.
Michael J Gruber announced the intent to orphan portmidi, noting a switch to portmidi2 is overdue.
Package Updates
On the devel-announce list, Aoife Moloney posted about the Libical4 update, and Michel Lind coordinated the final rebuilds to land it in Rawhide.
Adrian Reber announced the libcdio 2.4.0 update in Rawhide, which includes SONAME bumps for libcdio, libiso9660, and libcdio++.
Mattia Verga announced that python-dateutil 4.0.0 is coming to Rawhide, un-deprecating the package as upstream has become active again.
Dominik 'Rathann' Mierzejewski announced a mac SONAME bump for Monkey's Audio Codec to version 13.46.
Alexey Savchkov introduced themselves as a DevOps engineer interested in adopting orphaned C/C++ packages like ptl and usbsniff, and asked about using short vs. full git commit hashes in spec files.
Kanishk Bansal introduced themselves with a focus on security, submitting a rebase of expat to fix several CVEs, and expressed interest in automating CVE triage.
Igor Bispo introduced themselves as the upstream author of ParrotIA, seeking a sponsor to package it and its Python dependencies for Fedora.
All contribution opportunities
Developers and scripters can tackle a variety of language-specific and system-level challenges across the project. Rust developers are needed to port packages to quick-xml v0.41 and address CVE-2026-119375 in statically linked SQLite packages. Ruby developers can help fix FTBFS issues for rubygem-mysql2 and migrate rubygem-ruby-libvirt to the TypedData API, while Perl experts can resolve an i686 build failure for perl-Algorithm-BloomFilter. Web and scripting contributors can resolve a @comark/nuxt module deprecation, fix failing automated actions in the design repository, or update the docsbuilder.sh script to the new Forge format. Additionally, system-level programmers can assist with a dnf5daemon-server bug or provide patches for a GDM fingerprint login issue.
For those with RPM packaging experience, there are numerous opportunities to review new submissions or adopt orphaned software. Contributors can provide package reviews for agent-skills, rubygem-net-pop, or ParrotIA and its dependencies. Experienced packagers can also adopt orphaned packages like xorg-x11-drv-amdgpu and portmidi, take over a stalled EPEL 10 request for gparted, or help bring mailman3 to EPEL 10 to assist Release Engineering.
Quality assurance and infrastructure enthusiasts are highly encouraged to participate in testing and system maintenance. Testers can join the KDE Plasma 6.8 Test Days, evaluate an unofficial Plasma 6.8.3 COPR, or provide karma for a ROCm upgrade fix. OpenQA experts are needed to investigate a Tux Racer navigation test failure. On the infrastructure side, beginners can learn Ansible by configuring ELN Monitoring for Matrix, while those interested in Zabbix can help refactor external HTTP checks. Contributors with image-building experience can also assist the Server team in updating kiwi definitions to switch the SBC image to GPT/EFI.
Finally, non-code contributions are vital for documentation, design, and community growth. Graphic designers can create a print-ready PDF for a "Fedora loves GNOME" sticker or design a landing page for Fedora Remix. Writers can draft a migration proposal for Fedora Magazine, write a post-installation guide for Strengthening Server Updates, or update legacy syntax in Quick Docs. Community veterans can also provide mentorship by guiding newcomers like Fardeen Khan and Lutz Weber, or by helping Julita Inca get started with Ansible testing.
TuxTalk is a free voice dictation tool for Linux. You hold a key, talk, and let go. What you say appears wherever your cursor is located: a document, an email, a chat box or a terminal. The speech model runs on your own computer, so your voice never leaves it and there is no account to create. This is provided under the MIT license and the code is on GitHub.
This article walks through installing it on Fedora Workstation or Fedora KDE Plasma Desktop, what the first run changes on your system and why, using it day to day, and removing it if you wish.
Before you start
You need a working microphone and a 64-bit Fedora install on x86_64. No graphics card is required. The default speech model is fast on an ordinary processor, and if you have an NVIDIA, AMD or Intel graphics chip, TuxTalk can use it through Vulkan.
TuxTalk isn't in the Fedora repositories and there's no Copr build. You install the RPM from the project's GitHub releases page and check it against the checksum file published with it.
Install the RPM
Download both tuxtalk-0.23.1-1.x86_64.rpm and SHA256SUMS.txt from the latest release at https://github.com/ronb1964/TuxTalk/releases into the same folder. Then check the RPM against the checksum file:
$ cd ~/Downloads
$ sha256sum -c --ignore-missing SHA256SUMS.txt
tuxtalk-0.23.1-1.x86_64.rpm: OK
If it says anything other than OK, delete the file and download it again. Then install it with dnf, which also pulls in the few system libraries it needs:
$ sudo dnf install ./tuxtalk-0.23.1-1.x86_64.rpm
dnf warns that it skipped the OpenPGP check for the package. This is because the RPM isn't signed with a key and why the checksum step, indicated above, matters.
The package installs into /opt/talktype (the folder kept the app's old name so upgrades replace files in place), adds a tuxtalk command, and puts TuxTalk in your applications menu.
Installing on Atomic Desktops
For Silverblue and the other Fedora Atomic desktops, download the AppImage from the same release page indicated above (see the Assets section). Make it executable and run it:
Start TuxTalk from your applications menu. The first-run screen looks at your graphics card and your language and recommends a setup. The default is NVIDIA's Parakeet model, which covers English and 24 other European languages. If you need another language, OpenAI's Whisper covers 99 of them. Either one downloads once and then works offline.
The first-run screen
The first run also asks for your admin password once, to set up two things:
The hotkey helper. On Wayland an ordinary program cannot detect keys pressed in other windows, so TuxTalk needs help to notice F8. A small helper program runs as a systemd service, tuxtalk-hotkeys, and it's the only part of TuxTalk that reads the keyboard. It doesn't run as root. It runs as a throwaway user (systemd's DynamicUser) whose only extra right is the input group, with no network, no access to home folders, a read-only system and no way to gain more privileges. It only reports hotkeys, never what you type: F-keys and the few other keys that never type anything, Right Ctrl or Right Alt on their own, or a key held together with two of Ctrl, Alt and Super. Letters, numbers and Enter are never reported. And it only reports them to the user who's at the screen. The file it runs sits in a root-owned folder, /usr/local/libexec/tuxtalk, so nothing you run as yourself can change it.
A udev rule that gives /dev/uinput to the user at the screen, the same way Steam's rule does for game controllers. TuxTalk uses it to type, through its own virtual keyboard. A program can press keys with /dev/uinput, but it can't read them.
A restart is not needed. You can look at the helper yourself:
$ systemctl status tuxtalk-hotkeys
$ systemd-analyze security tuxtalk-hotkeys
The second command rates it 0.6, "SAFE".
On Fedora Workstation, TuxTalk also offers to install its GNOME Shell extension, which puts its menu in the top bar. GNOME only loads a new extension after you log out and back in once. On KDE Plasma it shows a tray icon instead.
Dictate
Click where you want the text to go, hold F8, say what you want, and let go. A moment later the text appears. If you'd rather not hold a key for a long dictation, tap F9 to start and tap it again to stop.
Two sentences dictated into KWrite
A few things that make it more useful:
Say punctuation and it appears: "comma", "period", "question mark", "new paragraph".
Say an email address the way you'd say it out loud. "john at gmail dot com" comes out as john@gmail.com.
In a terminal it leaves off the capital letter and the period, so a dictated command is ready to run.
Names and terms it keeps getting wrong go in Your Words in Preferences, spelled your way. Or say "fix that word" right after a dictation.
For hands-free use, turn on the double-tap option under Preferences → General. Then double-tap F9, talk as long as you like, and it stops by itself when you stop talking.
If your F-keys need the Fn key, Preferences → General also offers Right Ctrl, Right Alt, Scroll Lock or Left Ctrl+Space.
There's more in TuxTalk Labs under Preferences → Advanced. Each feature in this menu is off until you turn it on. The newest feature is running the desktop by voice: opening apps, snapping windows, and a numbered mouse grid you can click with by voice.
Remove TuxTalk
Open Preferences, go to Updates & Backup and click Uninstall TuxTalk…. It asks for your password once and removes everything it set up: the program, the hotkey helper, the udev rule, the downloaded models and the GNOME extension. Your settings are retained unless you tick the box to delete them as well. If TuxTalk won't open, the same thing can run from a terminal:
$ tuxtalk --uninstall
Removing only the package with sudo dnf remove tuxtalk takes the hotkey helper with it, but leaves your settings and the downloaded models in your home folder.
Feedback
TuxTalk is a hobby project, and it gets better when people tell me what doesn't work for them. Questions, problems and ideas are welcome in the Discussion section in the GitHub project at: https://github.com/ronb1964/TuxTalk/discussions
A note on how this was made:
I can't write code. TuxTalk is written by Claude, Anthropic's AI, and I test it and use it every day. I do my best to make sure the code is held to a standard a human developer can respect. Claude also helped me draft this article. I went through it and changed it to sound more like me, and I've checked every step in it. (Assisted-by: Claude)
Another busy week gone by, here's a bit belated long form recap
of doings in the last week.
anubis adjustments
We use anubis in front of a number of our sites to somewhat
keep the scraper menace at bay. For a while I have been puzzled
as to why there were so many challenges. After digging into it
recently I think I figured out why.
We have a network of proxies all over the world.
They each run an anubis instance. Proxies are reached via
round robin dns (ie, if you are in say south america you will
get a selection of proxies in that region when resolving things).
When you make a request, and anubis decides to challenge you,
your browser will do a challenge, anbuis will sign a cookie for
you that shows you solved the challenge and are good for a week.
All the proxies use the same key to sign the cookie, so they should
all be good on any proxy. Right? Well, no. Because it turns out
there's a bit more to make it so you can't just replay a connection
and bypass things.
So, you might hit proxy a, get a challenge, be fine for a while,
then you hit proxy b. The cookie is valid, but it looks like a
replay since it doesn't have any knowlege of it, so you get
another challenge.
So, sadly the answer is a shared store for this information for
all the proxies. Not great to add another point of failure in
but if the proxy cannot reach the backend anyhow, it probibly
doesn't matter that it can't reach a valkey store.
So, I setup a common valkey in our openshift cluster with
multiple pods, sentinal setup for failover and replication.
It was a bit tricky to get it working with our vpn setup, but
I managed to do so and rolled it out this last week. First
to staging, then a few production hosts, then all of them.
The valkey backend also stores some other info to speed things up.
So, the TLDR version: I hope legit folks will see a good deal
less challenges now and thus everything should be a bit faster.
bodhi and the scrapers
Of course that leads into scrapers. poor bodhi.fedoraproject.org
( Our updates system ) has been getting hit pretty hard by scrapers
lately. Many of them are "security scanners" trying to get information
about security updates. Thats fine, but when you ask for security
updates for EOL releases, or security updates for some package
where you want page 10000 (ie, updates that came out years and years
ago) it puts quite a strain on things.
Bodhi would get a bunch of these database heavy queries, then
the backend database would get slow because it's doing so many of them
and then the pods would fail liveness check and get restarted.
I did a few things to try and help this:
A 30s timeout on web queries. If it takes longer than 30s to answer
some query, just teminiate it and take the next request. This should
hopefully help prevent long queries from taking all threads up.
Scrapers were using the bodhi rss feed feature to bypass anubis
We had allowed rss feeds because they often cannot do challenges
but the scrapers found you could do '?search=' on rss feeds to
search for things. This should now get you a challenge.
Increased threads in general to handle more requests.
It seems to have helped, but time will tell.
Also, I think we should look at providing static dumps of common
information around updates that people could just download and
parse directly. This will take some doing to identify what data
people want and get bodhi able to generate it.
mass update/reboot cycle next week
Last week RHEL 10.3 and 9.8 came out, the week before fedora 45 came out.
So, next week we are going to update/reboot things, move a bunch of
our fedora instances to fedora 45 and resize some things to handle current
usage patterns.
As usual, monday should be staging, tuesday/wed should be various hosts
we can do without causing any service impact and thursday will be the
actual outage when we do the rest.
Hopefully that will leave us into a good state for...
US Thanksgiving holiday
The week after next is the US Thanksgiving holiday. I'm going to be
"off" that week, so don't expect me in meetings or the like.
I will of course still be around in case problems arise.
Hopefully I can actually get to some of my packaging backlog.
Giant owl butterfly (Caligo telamonius memnon) in the Haga Butterfly House in Solna. I thought I was lucky finding them sitting opposite each other like this, but then learned they do that habitually.
Anthropic released a Linux beta of Claude Desktop, but only as a .deb package for Debian and Ubuntu. claude-desktop-rpm is a small Bash script that installs that same package on Fedora. This article covers what the script checks, what it changes on your system, and how to remove it again.
Before you start: what this is and what it costs
Claude Desktop is proprietary software from Anthropic, released under Anthropic's own terms. The install script described here is MIT licensed. It is not made by Anthropic and it does not redistribute any of Anthropic's files: it downloads the package from Anthropic's own repository each time.
You need a Claude account to use the app. Chat works on every plan, including the free one. Claude Code and Cowork, the two features most people install the desktop app for, need a paid plan (Pro, Max, Ultra, Team or Enterprise). Anthropic's download page lists the current plans and prices.
If you would rather use free and open source tools for this kind of work, there are good options that run on Fedora too, such as OpenCode and Hermes Agent. This article is for people who already use Claude and want the official app on Fedora.
What the script checks before installing
Anthropic publishes the Linux beta as a signed APT repository. The script described here reads that repository the same way APT would, and stops if any check fails:
Anthropic's public key must match a fingerprint pinned in the script.
The repository index (InRelease) must be signed by that key, and its Valid-Until date must not have passed.
The package list's checksum must match the signed index.
The .deb's checksum must match the package list.
Only if all these checks are passed does it unpack the .deb. A reader on Fedora Discussion found a gap in the first version (the index could be signed by any key in the key file, not only the pinned one). That is fixed, and the test suite now runs each of these checks against a tampered copy of the repository.
Installing it
The script needs four packages that most Fedora Workstation systems already have. You might verify that these are available:
sudo dnf install curl gnupg2 binutils tar
Next, download the Claude script from the latest release into a folder and run it as your normal user:
Each release also publishes a checksum file, SHA256SUMS. To check the downloaded script before running it, fetch that file into the same folder used to contain the script and compare:
The script is a single Bash file so you can also read it before running it.
The installation does NOT use sudo. Everything goes into ~/.local (the app, a launcher, the menu entry and icons) and ~/.config (a systemd user timer for updates). The script also copies itself to ~/.local/bin/claude-desktop-rpm, so from then on you can run it by name.
Open Claude from the application menu and sign in. If something looks wrong, run:
claude-desktop-rpm doctor
This checks the installation, the launcher, automatic updates, the tray icon, the keyring that stores your sign-in, and the Cowork prerequisites. Each warning comes with the command that fixes it.
Why the app stays light in dark mode
On GNOME, the app stays light even when the desktop is set to dark. Electron apps on Linux read the GTK theme name, and GNOME's dark style does not change that name. It sets a separate color-scheme preference that Electron ignores.
The script does not touch Anthropic's files. Instead, the launcher created checks GNOME's color-scheme setting when you start the app, and sets GTK_THEME=Adwaita:dark for Claude only when it is dark. If you set GTK_THEME yourself, the launcher leaves it alone.
GNOME also hides tray icons by default, and Claude's tray menu is where Quit lives. The doctor command tells you how to turn on the AppIndicator extension if you want the icon.
Setting up Cowork
Cowork runs tasks inside a small virtual machine, so it needs KVM, QEMU, UEFI firmware and virtiofsd. On Fedora all of these come from Fedora's own repositories. Run this once:
claude-desktop-rpm cowork
This is the only command that uses sudo. It performs the following steps:
installs qemu-system-x86-core, edk2-ovmf and virtiofsd with dnf
writes /etc/modules-load.d/vhost_vsock.conf and loads the vhost_vsock module
adds you to the kvm group
Log out and back in for the group change to take effect. The command does not change any file that a package owns, so rpm -V stays clean. An earlier version did replace two firmware links that edk2-ovmf ships. That was a mistake, and the current version restores the packaged links if it finds the old ones.
Plan for disk space
The app's Cowork virtual machine files take about 12 GB in ~/.config/Claude.
Updates
The script installs a systemd user timer that checks Anthropic's repository once a day. Each update goes through the same checks as the first install. If Claude is open when an update arrives, the script downloads and verifies it but waits, and the launcher puts it in place the next time you start the app.
To turn the daily check off or on again use these commands:
claude-desktop-rpm auto-update off

claude-desktop-rpm auto-update on
Note: If the app shows its own "Update available" button, ignore it. Its link points to APT. The timer handles updates, or you can quit Claude and run claude-desktop-rpm update.
A second account
Some people keep separate Claude accounts for work and personal use. Version 1.2.0 added profiles for that:
claude-desktop-rpm profile add work
This adds "Claude (work)" to the app menu. It opens with its own sign-in and chats in ~/.config/Claude-work, and it can run next to your normal Claude window. The launcher passes Chromium's --user-data-dir flag to do this. Anthropic does not document that flag for Claude Desktop, so a future version could ignore it. If that happens, both menu entries open your normal account and nothing is lost. Both tray icons also look the same; the tray menu, which shows each account's plan, tells them apart.
What does not work yet
Computer Use is not in Anthropic's Linux build on any distribution yet.
The script is tested on Fedora 44 Workstation (GNOME, x86_64), and its automated install test also passes on Fedora 45. A user reported it working on KDE Plasma on Aurora, an atomic Fedora variant. Other desktops and RHEL-based systems have not been tested much.
Anthropic officially supports only Debian and Ubuntu for now. If something breaks after an update, the problem may be in the script, so please report it on the project's issue tracker rather than to Anthropic. (See the project link in the Links section below)
Removing it
claude-desktop-rpm uninstall
This removes everything the install added to ~/.local and ~/.config, including the timer and any profile menu entries, and rebuilds the menu, file-type and icon caches.
Your chats and sign-in in ~/.config/Claude stay, in case you reinstall. Delete that folder (and any Claude-NAME folders) to erase them too.
The uninstall never uses sudo, so the Cowork setup stays: remove the packages with dnf and delete /etc/modules-load.d/vhost_vsock.conf if you no longer need them.
This is the 143rd issue of syslog-ng Insider, a monthly newsletter that brings you syslog-ng-related news.
NEWS
Syslog-ng hardening using Tor
For many years, I didn’t think that Tor could be useful for me. However, I’ve recently found a Gist on GitHub that describes how you can use it to harden your central syslog-ng server. And while I have yet to try it, at least now I have a reason to actually test Tor.
Syslog-ng end of August news, and about scaling back Java support
Most of August, I was on vacation, but now I’m back and I try catching up on the events of the past weeks, just like my colleagues do. Currently, we are fixing issues and reviewing contributions, but we also discussed scaling back our efforts on Java support.
Recently, I heard complaints within the syslog-ng community that using Elasticsearch is not that easy anymore. I installed Elasticsearch 9.5 with Kibana to verify these claims.
There will be a Fedora Copr outage while we upgrade infrastructure
machines to the latest Copr packages.
The build queue processing will be stopped during the outage, and the
Frontend/Web-UI will be down most of the time (no new tasks accepted).
The DNF packages and repositories (hosted on copr-backend …
This Week in Fedora (TWIF) is the Fedora community’s weekly report on project news, decisions, and contribution opportunities. Across the Fedora ecosystem this week, the primary focus was the highly anticipated release of Fedora Linux 45, with teams including Release Engineering, Quality, Infrastructure, Server, and Docs finalizing release candidates, deploying updates, and immediately transitioning into Fedora 46 planning. Beyond the release cycle, a major shared initiative is the Bootable Image Unification (“Atomic Fusion”) project, which dominated the agendas for the Council, Atomic, IoT, and Hummingbird groups as they prepared proof-of-concept demos. Infrastructure and tooling migrations also commanded significant cross-team collaboration; the Council, FESCo, and Quality teams are actively evaluating a potential transition from Bugzilla to a Forgejo-integrated issue tracker, while FESCo, Release Engineering, and ELN are coordinating the complete removal of the legacy DNF4 stack. Finally, adapting to upstream shifts and reinforcing system security were key technical themes, highlighted by FESCo and the KDE SIG managing the deprecation of X11 in KDE Plasma 6.8, alongside widespread security patching and cryptographic upgrades—such as the adoption of %openpgpverify—across the Perl, Rust, Cloud, and Infrastructure teams.
NOTE: This is an experiment of translating the This Week in Fedora report into a Fedora Community Blog series. Do you have feedback? Reply to the Fedora Discussion topic attached to this post and let us know your thoughts.
This Week in Fedora is generated with AI assistance, and this Community Blog edition was prepared with AI assistance too. AI-assisted summaries can be wrong, so please check anything important against the linked sources. If you spot a problem, open an issue in the TWIF repository or reply to this post’s Fedora Discussion topic.
The highly anticipated release of Fedora Linux 45 is now officially available, as announced across the project forums, community posts, and the announce and devel-announce mailing lists. This milestone brings exciting updates across the ecosystem, including Fedora Workstation 45 featuring GNOME 51’s reworked frame scheduling, and the KDE Plasma Desktop Edition highlighting KDE Plasma 6.8, the 30th-anniversary release of KDE. Hardware support continues to expand with the Fedora Asahi Remix 45 introducing out-of-the-box support for Apple M3 chips, alongside community-maintained RISC-V GA images available for testing, providing a great opportunity for contributors to report hardware enablement issues. For immutable OS users, detailed instructions are available for rebasing to Silverblue 45, while Fedora Atomic Desktops now utilize the new Anaconda Web UI and have migrated their repositories to the atomic-desktops organization, offering streamlined engagement for future contributors.
To avoid disruptive surprises, users and system administrators should note several key technical shifts in this release. The Anaconda installer now includes native support for Stratis storage configuration, simplifying advanced local storage management through an easy-to-use interface. Additionally, the unmaintained NetworkManager-vpnc and NetworkManager-fortisslvpn plugins are officially retired in Fedora 45, requiring users to migrate to actively supported VPN alternatives to maintain enterprise connectivity. Finally, on the infrastructure side, a brief planned server outage occurred on November 6th to reboot main VPN, email, and bastion servers into a new kernel for CVE mitigation, ensuring the ongoing security of the project’s backend services.
AI
AI
The AI/ML SIG discussed new package reviews, notably OpenShell, an NVIDIA-driven tool for agent sandboxing. Packaging updates were announced, with the latest AI and ROCm packages now available in COPRs for released distributions, and new LLM servers like Gufo and Colibri landing in Rawhide. The group is also collaborating on a Fedora Magazine article highlighting the use of the pi-coding-agent to help Fedora contributors, which may evolve into a broader series exploring how AI is utilized within the Fedora ecosystem. Other chat discussions touched on integrating hardware volunteering for AI tasks and addressing Wayland compatibility issues for freelance time-tracking tools.
Decisions
The latest AI and ROCm packages are now available for general use in COPRs for released Fedora distributions.
New LLM servers, Gufo and Colibri, have been packaged and are available in Rawhide.
The SIG will pitch and publish a Fedora Magazine article focusing on the pi-coding-agent, potentially kicking off a series on how AI is used in Fedora.
The Ambassadors group saw two forum discussions this week. A new contributor asked for help setting up their Fedora Campus Ambassador profile, including access to the wiki, Fedora People, and Libravatar, and received troubleshooting steps from the community. Additionally, a member started an organizational thread to coordinate a meetup for Fedora, CentOS, AlmaLinux, and RockyLinux contributors attending SFSCON 2026 in Bolzano, Italy.
Contribution opportunities
Contributors attending SFSCON 2026 in Bolzano, Italy (Nov 13-14) are invited to connect and team up with other community members.
This week, the Atomic group focused on bootable image unification (“Atomic Fusion”) with an upcoming presentation to the Workstation WG and a seed proof-of-concept demo (Meeting Agenda). In addition, there are ongoing discussions about rebasing Fedora Atomic Desktops on Fedora Bootc base images, which will modernize the build flow (Issue #88).
Several technical issues were also addressed, including a bug where systemd-oomd fails to intervene during memory exhaustion on Kinoite 44 (Issue #130), a syncing issue with the Fedora Cosmic-Atomic image (Issue #137), and an anomaly where rpm-ostree stable commits occasionally bundle packages from the updates-testing repository (Discussion).
Decisions
Systemd services in Atomic images will use ConditionPathIsMountPoint=/sysroot instead of checking for /run/ostree-booted to ensure compatibility with the composefs backend (Issue #133).
The Fedora Cosmic-Atomic update failure was identified as a release tooling script issue and moved to a releng ticket (Issue #137).
Contribution opportunities
Help is needed to file a releng ticket to investigate why rpm-ostree stable commits occasionally pull packages from the updates-testing repository (Discussion).
Contributors are invited to help create and review test cases for the upcoming Fedora Atomic Desktops Test Week, covering installations and upgrades via rpm-ostree, gnome-software, and plasma-discover (Issue #87).
Assistance is requested to test and provide a controlled reproducer for a memory exhaustion bug where systemd-oomd fails to intervene on Kinoite 44 (Issue #130).
This week, the Cloud group focused on image configuration and distribution infrastructure. A key update involves adding the SUSPEND_SAFE_FPR guest OS feature to Fedora Cloud GCP images to address a page reporting suspend UAF vulnerability (CVE-2026-74481), which is now being applied to new nightly builds (Issue 449). Additionally, following the announcement that the HCP Vagrant Registry is shutting down on December 31, the group is discussing setting up a self-hosted Vagrant registry to ensure continued availability of Vagrant boxes, drawing inspiration from AlmaLinux’s recent implementation (Issue 450).
Contribution opportunities
Help is needed to set up a self-hosted Vagrant registry for Fedora to replace the retiring HCP Vagrant Registry before December 31 (Issue 450).
This week, the COPR team successfully completed a scheduled server upgrade on November 3rd, bringing new features and bug fixes to the platform. Following the upgrade, an ongoing data migration to Pulp temporarily affected several projects (alphabetically from “sar” to “siddharthvipul1”), causing some 404 errors and pending builds which are expected to resolve as the migration progresses. Additionally, the team discussed the timeline for IPv6 support on the Pulp instance, estimating a fix for early next year, and provided support for building bleeding-edge Rust packages with vendored crates in Copr.
Proceeded with the ongoing data migration to Pulp, which temporarily causes 404 errors and pending builds for affected project owners while their specific data is being migrated.
Contribution opportunities
Help is welcome to set up automation that recognizes new copr-cli tags being pushed, creates the sdist tarball, and automatically uploads it to PyPI.
This week, the CoreOS team celebrated the general availability release of Fedora Linux 45. The testing stream has been successfully rebased to version 45.20261030.2.1, bringing notable changes such as native Butane support in Ignition, the use of chunkah for better layer reuse in container images, the relocation of RPM repository configs out of /etc, and the update to Podman 6.0. The team is currently in the post-release cleanup phase and has already opened the tracker for the upcoming Fedora 46 rebase. In addition to the release activities, the team addressed several critical bugs and infrastructure tasks. A fix for the IPv4 TCP use-after-free vulnerability (CVE-2026-98432) was shipped in the stable stream, and workarounds are being tested for an ext4 /boot corruption issue affecting upgrades. The team also approved a proposal to switch Konflux-driven streams to a Jenkins poll-based import model to simplify downstream pipeline management.
Decisions
Released Fedora Linux 45 and rebased the testing stream to version 45.20261030.2.1.
This week, the Council focused on the long-term future of Fedora’s issue tracking and ongoing image unification efforts. A major discussion was initiated regarding the potential transition from Bugzilla to a Forgejo-integrated system (related to FESCO#3664), weighing the necessity of adopting modern, open-source infrastructure against concerns over Forgejo’s current maturity and feature parity. Additionally, the agenda for the November 5th Bootable Image Unification (“Atomic Fusion”) meeting was published, featuring a review of the project board, a seed proof-of-concept demo, and a planned presentation to the Workstation Working Group.
The Design team focused on the initial sketches for the F46 wallpaper, discussing the use of alternative geometric shapes for bubbles while prioritizing iridescence. They also reviewed poster designs, noting layout inconsistencies and the need for better text hierarchy and spacing, and successfully closed the F45 Virtual Release Party graphics ticket. Additionally, the team discussed accessibility improvements for international audiences, agreeing to spell out acronyms like DEI. In the Matrix chat, automated alerts indicated that the “Fix time of day path” action failed in both the main and f45-backgrounds branches of the backgrounds repository.
Decisions
Iridescence will remain the primary visual focus for the F46 wallpaper bubbles, regardless of the final geometric shape chosen.
The Fedora logo and mascots will not be included in the wallpaper to comply with guidelines and avoid clutter; instead, mascot concepts will be repurposed for promotional art.
Acronyms such as DEI (Diversity, Equity, and Inclusion) will be spelled out in designs to improve accessibility and clarity for international audiences.
The Fedora Docs team successfully navigated the Fedora 45 release, merging numerous release notes covering updates like GNOME 51, KDE Plasma 6.8, and various system changes. Following the release, the team is restructuring the release notes repository to stop versioning; future notes will be built directly from the main branch, displaying the three most recent supported releases on a single page while older notes remain available via the Internet Archive.
Additionally, the team is revamping its infrastructure by transitioning the site-builder repository to build from main rather than prod. They are also evaluating “Bruce,” a new broken-link detection script, for CI integration to automatically generate static reports and eventually file issues for broken links. Furthermore, discussions are ongoing regarding Antora component consolidation to allow cross-repository module inclusion and integrating the Fedora Design Suite documentation.
Decisions
Stop versioning the release notes repository and build them exclusively from the main branch, preserving only the three most recent supported releases (Meeting, Issue #449).
Transition the site-builder repository (formerly docs-fp-o) to drop the prod branch and build the production site directly from main (Meeting, Issue #61).
Integrate the “Bruce” link-checking script into the CI pipeline in phases, starting with generating a static HTML report before moving to automated issue creation (Issue #69).
Retain docsbuilder.sh as a wrapper for local documentation previews while updating the underlying container to support Aarch64 and dropping npm dependencies (Issue #65).
Contribution opportunities
Review and merge open pull requests for the Fedora 45 Release Notes, as requested by community members (Forum Topic).
Help replace legacy {partialsdir} includes with the partial$ syntax across documentation repositories to align with current Antora standards (Issue #38).
Assist in documenting the Fedora Docs site build and monitoring process for the prod and stg branches (Issue #59).
Provide feedback on the proposed integration of the Fedora Design Suite documentation into the official Fedora Docs website (Issue #68).
Test and provide feedback on the proposed Antora module inclusion methods (component merge vs. Antora extension) to improve cross-SIG documentation discoverability (Issue #66).
The ELN SIG held a meeting on November 3, 2026 (meeting log). Key updates include the complete removal of dnf-4 from ELN, the completion of rebuilds for libxml2 2.15, and the replacement of perl-Params-Util with perl-Params-SomeUtil. Additionally, the Content Resolver now displays daily diffs. On the RISC-V front, approximately 140 packages have been built, though progress is currently paused pending fixes for toolchains like gcc, golang, and rust. The group also discussed ongoing issues with KDE Discover (Issue #633) and the unmaintained libappstream-glib (Issue #486), as well as upcoming libical4 rebuilds.
Decisions
dnf-4 has been completely removed from ELN and will not be included in RHEL 11.
perl-Params-Util has been replaced with perl-Params-SomeUtil.
This week in EPEL, discussions highlighted a known daily cache delay in the CentOS Stream repo for Fedora’s Koji, which temporarily caused scratch build failures in epel9-next (URL). Security updates were a major focus, with uv (v0.13.5) and ruff (v0.17.2) being pushed to stable for the EPEL10 leading branch to address multiple RUSTSEC vulnerabilities and the eMudhra CA compromise (URL). Additionally, pipx is being retired from EPEL9 due to 23 security vulnerabilities that cannot be practically patched on the older Python 3.9 stack (URL). Other activities included the EPEL 10.2 retirement announcement, progress on bringing mailman to EPEL10, and participation in the release party CLE presentation.
Decisions
The pipx package is being retired from EPEL9 due to severe security vulnerabilities and incompatible Python version requirements (URL).
Versions 0.13.5 of uv and 0.17.2 of ruff were pushed to stable for the EPEL10 leading branch to address critical security flaws (URL).
Andrew Heath introduced himself to the Fedora community, sharing his extensive background in enterprise Linux, infrastructure automation, and image building. He expressed interest in contributing to packaging, image building, QA, and infrastructure automation. In response, he was welcomed by the community and advised to engage with the packaging team in their Matrix room to find a sponsor and initial tasks.
Contribution opportunities
Andrew Heath is seeking a packaging sponsor and looking for good first tasks, particularly in co-maintaining existing packages or picking up orphaned ones in the automation and sysadmin tooling space.
Opportunities exist to mentor or collaborate with Andrew in areas like image building (osbuild), QA testing, and infrastructure automation.
During this week, FESCo celebrated the release of Fedora 45 and announced upcoming elections. The committee held a meeting and processed numerous tickets, focusing heavily on the future of Fedora’s issue tracking system, with extensive debate on whether to migrate to Forgejo or maintain a community-run Bugzilla instance. Other major topics included the coordinated removal of the legacy DNF4 stack and Modularity, as well as handling the deprecation of X11 support in KDE Plasma 6.8 for stable releases.
Decisions
Rejected the request to revert the removal of plasma-workspace-x11 from Fedora 44 and 45 in Ticket #3707.
Approved the pull request clarifying the responsibilities of the Engineering representative for the Council in Ticket #3613.
Rejected the Thin LTO Build Flag (F47) change proposal due to a lack of votes over five weeks in Ticket #3692.
Transferred maintainership of python-authlib to a new co-maintainer following the non-responsive maintainer policy in Ticket #3697.
Contribution opportunities
Community members are asked to help identify tools and scripts that depend on the legacy DNF4 stack or libmodulemd to assist with their planned removal in Ticket #3702.
Volunteers interested in maintaining a community-run Bugzilla instance are invited to put forward a proposal to the Fedora Infrastructure group, as discussed in Ticket #3664.
The Hummingbird group prepared for their upcoming “Atomic Fusion” (bootable image unification) meeting on November 5, 2026. The agenda included a project board review, a potential demo of a seed proof-of-concept, and preparations for presenting to the Workstation Working Group.
The Infrastructure team successfully navigated the Fedora 45 release, officially lifting the infrastructure freeze on November 4th. The week involved significant maintenance and troubleshooting, including resolving a storage-related outage on Fedora Forge by resizing its Persistent Volume Claim and NetApp volume, and investigating persistent login issues with Fedora Accounts (FAS) linked to FreeIPA OTP interactions.
In addition to routine maintenance, the team began planning the deployment of Siguldry to the production environment for RPM and OSTree signing. They also scheduled a mass upgrade and reboot of infrastructure servers for November 19th, and discussed ongoing efforts to optimize AWS resource usage and clean up untagged cloud instances.
Decisions
The infrastructure freeze for the Fedora 45 release was officially lifted on November 4th. (URL)
A mass upgrade and reboot of most infrastructure servers is scheduled for November 19th at 22:00 UTC, which will cause short outages for many contributor services. (URL)
Mirrors that transparently redirect HTTP traffic to HTTPS will be updated in MirrorManager to explicitly use HTTPS URLs only, improving crawler compatibility. (URL)
The Limestone Networks mirror (mirror.lstn.net) was disabled in MirrorManager due to an expired TLS certificate. (URL)
New FAS groups were created for chromium-sig, sysadmin-oraculum, napkinstack-labs, tablepro, and nanlang.
Contribution opportunities
Help is needed to investigate and resolve the persistent Unauthorized: bad credentials login errors on accounts.fedoraproject.org, which appear to be related to FreeIPA OTP module interactions. (URL)
Contributors can help clean up NetApp and host storage, including moving older releases to archive volumes, increasing partition sizes on alerting hosts, and compressing logs. (URL)
Assistance is requested to set up a Zabbix HTTP check for Oraculum and retire its old watchdog email alerts. (URL)
There is an opportunity to help set up Zabbix monitoring for the staging autosign service by implementing checks for AMQP, RPMs, OSTree, and CoreOS metrics. (URL)
Help is needed to create an announcebot Discourse service user and API key for sending compose announcements. (URL)
A new contributor expressed interest in helping with virtualization and infrastructure tasks, presenting an opportunity for onboarding and mentorship. (URL)
This week, the IoT group focused on bootable image unification and resolving a system upgrade issue. Laura Santamaria shared the agenda for the “Atomic Fusion” meeting, which included a seed proof-of-concept demo and a presentation to the Workstation Working Group (URL). Additionally, a user reported a bug where upgrading to Fedora 45 fails due to a missing GPG public key in rpm-ostree. The issue was resolved locally by updating the gpgkeypath in the fedora-iot.conf file to point to /usr/share/pki/rpm-gpg/ (URL).
This week, the Fedora KDE group navigated discussions regarding Plasma 6.8 updates and overall desktop stability. Notably, the update to Plasma 6.8 officially drops X11 session support upstream, resulting in the obsoletion of kwin-x11 and plasma-workspace-x11 packages in Fedora 44. Users relying on X11 were advised that locking packages might prevent future UI updates, though community workarounds like Copr repositories have emerged. Additionally, the community discussed the marketing and perceived stability of Fedora KDE, with maintainers emphasizing that upstream KDE’s rapid release cadence inherently involves trade-offs. Users seeking long-term support might look toward LTS distributions, while those experiencing bugs are encouraged to contribute directly to upstream bug resolution.
The replacement of kwallet with oo7-daemon is currently deferred for KDE Plasma and Plasma Mobile variants due to a lack of time for integration, as noted in Issue #700.
The screen package will not be added to the Kinoite base image; users are advised to use package layering or system extensions instead (Issue #723).
Contribution opportunities
Contribute to upstream KDE bug resolution to improve the stability of the Plasma desktop environment, as suggested in the discussion on Fedora KDE stability.
In a discussion regarding the koneko license and copyright, Cristian Le followed up on concerns regarding copyrighted sprites included in the project, specifically characters from Cardcaptor Sakura and the BSD Daemon. Following previous advice to drop the artwork, Cristian confirmed that the issue has been flagged to the upstream developers and that the problematic sprites will be removed via a downstream patch if necessary.
Decisions
The copyrighted sprites (Cardcaptor Sakura and BSD Daemon) in koneko must be removed, either by upstream or via a downstream patch. (Source)
Community feedback is welcome to improve the FIDO2 integration living document.
Contributors are encouraged to explore, test, and share improvements regarding FIDO2 integration for Polkit GUI prompts, as the original author left this partially incomplete.
This week, Mindshare began early planning for the Virtual F46 Release Party, aiming for May 2027, to ensure a smooth event by crowd-sourcing ideas and recruiting role leads well in advance. Additionally, a community member reached out to organize an informal meetup for Fedora, CentOS, AlmaLinux, and RockyLinux contributors attending SFSCON 2026 in Bolzano, Italy.
Contribution opportunities
Help organize the Virtual F46 Release Party by volunteering for event team roles including Wrangler, Speakers, Design, Promotion & Content, and Production & Video. To get involved, join the #commops:fedoraproject.org Matrix room and reply to the ticket.
Connect with other community members at SFSCON 2026 in Bolzano, Italy, by joining the organizational thread.
This week, the Perl group focused heavily on package maintenance, dependency management, and security enhancements. Maintainers implemented source signature verification using openpgpverify for packages like perl-Net-DNS and mod_perl. Several packages received routine version bumps, including perl-Mozilla-CA, perl-CGI, and perl-Tk-Text-SuperText. Additionally, contributors collaborated on adjusting dependencies for downstream distributions, such as adding build conditionals for Lexical::Var in perl-Exporter-Tiny and disabling optional dependencies in RHEL builds for perl-File-ShareDir.
Decisions
Merged a build conditional in perl-Exporter-Tiny PR #2 to use Lexical::Var via Recommends instead of Requires on older Perl versions.
The Python group discussed reversing the deprecation of python-dateutil following a new upstream 4.0.0 release. Contributors agreed to undeprecate the package and patch out its new tzdata dependency to rely on the system’s time zone data instead. Additionally, a proposal was made to automatically set LD_LIBRARY_PATH in %py3_test_envvars to streamline testing, and feedback is currently being sought on potential breakages.
Decisions
Undeprecate the python-dateutil package following the new upstream 4.0.0 release.
Patch out the tzdata dependency in python-dateutil 4.0.0 to rely on system timezone data instead.
The Quality team successfully verified and tested the release candidates for Fedora 45, officially declaring it “GO” for release, alongside publishing and updating the Common Issues. The team also hosted a Test Week for Linux Kernel 7.3, encouraging users to test the kernel rebase on Fedora 44 and 45.
Fedora 45 has been officially released, with the team handling final release candidate composes, signing the IoT compose, and managing post-release cleanup and synchronization. During the rollout, a minor synchronization issue with the Labs images was manually resolved, and discussions were held to better align fedora_distro_aliases and releases.json updates in future cycles.
In addition to the release, the team resolved several infrastructure and build issues. This included fixing broken RHEL 9 repositories for EPEL 9 builds, addressing a bug where Rawhide .treeinfo files were missing kernel image information, and removing several underpowered x86_64 hosts from the heavybuilder channel to prevent Out-Of-Memory errors during large builds like Chromium.
Several underpowered x86_64 build hosts were removed from the heavybuilder channel to prevent OOM errors during large package builds. (URL)
A fix was implemented and backported in Pungi to ensure .treeinfo files contain kernel image information, restoring virt-install functionality for Rawhide. (URL)
The EPEL 7 meson tagging order issue will not be fixed because EPEL 7 is End of Life. (URL)
Provide feedback and identify any infrastructure applications still relying on DNF4 for the F46 Change Proposal to Remove DNF4, libdnf, and libmodulemd.
The Fedora RISC-V team successfully finalized and announced the Fedora 45 RISC-V GA images, including Server, Container, and Cloud variants. A major focus this cycle was clarifying kernel recommendations: the ‘Omni’ kernel is highly recommended for most physical hardware to avoid issues like PCIe/NVMe data corruption on JH7110-based boards (e.g., VisionFive 2), while the ‘Generic’ kernel is primarily targeted at QEMU and a select few boards. Meanwhile, the bootstrap of Fedora ELN (Enterprise Linux Next) for RISC-V is making significant progress, with Koji fully configured for ELN and RVA23 channels, and over 140 packages already built. The team is also actively debugging hardware-specific issues, including GCC build hangs on the SpacemiT K3 and a QEMU KVM guest initialization bug.
Decisions
The ‘Omni’ kernel is officially recommended for most physical RISC-V hardware (including VisionFive 2) to prevent potential data corruption with certain PCIe/NVMe storage configurations, while the ‘Generic’ kernel is recommended primarily for QEMU.
Koji hub policies and channels have been updated to route RVA23-specific builds appropriately, enabling the ongoing Fedora ELN bootstrap.
Contribution opportunities
Help is needed to debug and resolve a hard lockup issue occurring during GCC ELN and Rust builds on SpacemiT K3 hardware (disabling Transparent Huge Pages is currently being tested as a workaround).
Contributors can assist with upstreaming vendor patches from the Omni kernel to the Mainline kernel to improve out-of-the-box hardware support.
Developers familiar with QEMU and KVM can help investigate a guest initialization failure when using -cpu max on RISC-V KVM hosts.
The Rust group focused heavily on security updates and package rebuilds this week, addressing multiple RUSTSEC advisories across crates like zstd, zip, ruzstd, rustls, and webpki-roots. Additionally, there was a mailing list discussion regarding a request to package crubit for Fedora and EPEL to support Chromium builds, though it faces significant hurdles due to its reliance on nightly Rust and unstable compiler internals.
Decisions
The request to package crubit for Fedora to support Chromium builds is currently blocked, as the required cc_bindings_from_rs tool depends on a nightly compiler and unstable compiler internals, which cannot be shipped in Fedora (Mailing List).
The effort to update packages to ruzstd v0.9 to address RUSTSEC-2026-0344 has been completed and the tracking ticket is closed (Issue 42).
Contribution opportunities
Assist with rebuilding or updating applications not co-maintained by the Rust SIG that vendor affected versions of zstd, zstd-safe, rustls, and webpki-roots (Issue 48, Issue 43, Issue 46).
Help port applications currently depending on older versions of zip (v0.6), rustls (v0.21/v0.22), and webpki-roots (v0.25) to their latest secure releases (Issue 47).
The Server Working Group celebrated the release of Fedora 45 Server and immediately began preparing for Fedora 46 by setting up a new testing project. A significant portion of the week was dedicated to the “Strengthening Server Updates” project, focusing on system resilience using LVM snapshots. Following the F45 release, the group closed numerous tracking tickets for system-wide changes and package updates.
In addition, the group discussed ongoing work on Ansible support, deciding to catch up on outstanding tasks over the next two weeks before reconvening on the topic. New contributors joined the meeting and immediately volunteered to help with testing and documentation efforts.
Decisions
The group agreed to continue using the ticket system for release testing (starting with Fedora 46), with optimizations to be discussed in the process. (Meeting Log, Mailing List)
For the “Strengthening Server Updates” project, the agreed next steps are testing the snapshot procedures, adding them as a step in post-installation, and preparing a Fedora Magazine article. (Meeting Log, Mailing List)
Members will use the coming weeks to catch up on outstanding tasks for the Ansible support project, deferring further discussion for 14 days. (Meeting Log)
Contribution opportunities
Testers are highly needed for the “System Resilience Using LVM Snapshots” procedures. Findings should be reported in Ticket #272.
Contributors are invited to help write a how-to style article for the post-installation section regarding server update resilience (Ticket #271).
There is an open opportunity to help draft a Fedora Magazine article about the “Strengthening Server Updates” project.
Assistance is welcome for the ongoing Ansible support project, specifically regarding the creation of an Ansible management CLI and configuring CI/CD runners (Ticket #268).
This week, the Websites and Apps team resolved an issue where the x86_64 folder was missing from the Fedora 45 Labs download page by syncing the content and rebuilding the site. The team also successfully closed the F45 beta release tracker and opened tickets for UI improvements, including fixing dark-mode logos on the CoreOS page and improving contrast in the Fedora Media Writer section. In addition, a community member reported that the captive portal check URL is on an HSTS-preloaded domain, which breaks Wi-Fi login detection; the infrastructure team plans to move it to another domain in the future. Finally, a bug in Fedocal where events with past repeat-end dates fail to appear was identified and resolved for a user.
Decisions
The infrastructure team plans to move the captive portal check URL to a different domain to resolve HSTS preload list conflicts that break Wi-Fi login detection (Ticket #13629).
Contribution opportunities
Review requested for the Fedora Maubot/Zodbot plugin for cookies: PR #257 and PR #161.
Help needed to fix missing dark-mode variant logos on the CoreOS page (Work item #439).
Help needed to improve the contrast of download items in the Fedora Media Writer section (Work item #438).
A brief 20-minute meeting was held on November 3rd, following up on the agenda from October 27th. The original agenda included topics such as Fedora 45 blockers and exceptions, appstream-data automation, and DNF updating without wheel.
From F45 onwards: Fedora-maintained (self-updating) hardening…: Chris announced a new self-updating kernel hardening feature available from Fedora 45 onwards. Designed for both beginners and advanced users on GNOME and KDE, it applies security-first configurations automatically, overriding certain defaults like yama-ptrace-enable. Users discussed its interaction with Atomic variants, Toolbox containers, and potential impacts on specific applications, with Chris noting that a new #hardening tag will be used to consolidate feedback.
Btrfs-patrol: snapshots before every dnf transaction…: JC shared updates on btrfs-patrol, a snapshot and rollback tool tailored for Fedora’s default Btrfs layout. It automatically takes read-only snapshots before dnf5 transactions and allows for one-command rollbacks while ensuring the restored snapshot has the necessary kernel modules to boot.
GitLab access for inactive accounts: Shaun McCance announced that due to Fedora exceeding its seat limit on GitLab, accounts with no activity in the past 12 months will be downgraded to view-only access. This will free up seats for active teams without deleting any data, and edit access can be restored if needed.
Proposal: Optional CJK input method support for Fedora’s kmscon console: Skyter Lin proposed adding optional CJK (Chinese, Japanese, Korean) input method support for Fedora’s new kmscon virtual console, having successfully tested Traditional Chinese using uim-fep and m17n. Jocelyn Falempe confirmed the technical feasibility of using Super+Space for toggling and suggested starting by adding a kmscon-uim man page.
Some news about the Audinux activity for october: Yann Collette provided an October update for the Audinux repository, highlighting the addition of 29 new audio-related packages and 155 package updates. Notable additions include several AI-generated standalone applications like bytebeat, ibniz-rust, and mx44-rust, which underwent security and performance audits.
New packages in Fedora Linux (October 2026): Miroslav Suchý shared a comprehensive list of newly added packages to Fedora Linux during October 2026, generated using the rawhide-changes.py script.
F46 Change Proposal: Usermode2 (self-contained): On the devel-announce mailing list, Aoife Moloney shared a Fedora 46 Change Proposal to replace the C implementation of the usermode package with a memory-safe Rust rewrite of its userhelper and consolehelper tools. The rewrite serves as a drop-in replacement while dropping several obsolete standalone GUI tools, and developers discussed ensuring the Rust standard library safely handles the SUID execution environment.
Is packaging a fork permissible?: Łukasz Wojniłowicz asked if packaging a fork under the same name as the upstream project is permissible. Developers clarified that while it is allowed and sometimes necessary for dormant projects, the spec file should clearly explain the relationship between the original repository and the fork to avoid confusion.
F46 Change Proposal: Libical4 (system-wide): On the devel-announce mailing list, Aoife Moloney announced a Fedora 46 Change Proposal to update the libical library to its 4.x series, which introduces an API/ABI break from the 3.x series. Milan Crha and Michel Lind coordinated the necessary package rebuilds in a side tag, noting that only a subset of dependent packages required direct updates.
Heads-up: %gpgverify -> %openpgpverify PRs are coming: Jakub Jelen notified maintainers about upcoming pull requests to migrate packages from %gpgverify to the new %openpgpverify macro, which uses Sequoia’s sqv for upstream source signature verification. He advised maintainers to check if their upstream keys need refreshing or updating to comply with current cryptographic standards.
Orphaned packages looking for new maintainers (on devel-announce): Several orphaned packages were adopted, including tunneler and openfortivpn, while Dominik Mierzejewski advised against adopting rubygem-drake due to obsolescence.
Orphaned – singularity-ce: David Trudgian orphaned singularity-ce as the upstream project reached EOL, recommending apptainer as a suitable replacement.
Package updates
libcdio 2.4.0 update comes with new sonames: Adrian Reber announced an upcoming update to libcdio 2.4.0 in Rawhide, which bumps several SONAMEs and requires rebuilding dependent packages in a side tag.
Soname bump: libcamera: Milan Zamazal planned an update to libcamera 0.8.0 in Rawhide, noting ABI changes that require rebuilding pipewire-plugin-libcamera, libcamera-apps, and plasma-camera.
openapv SONAME bump: Dominik Mierzejewski announced an update to openapv that includes a SONAME bump and API changes, requiring a rebuild of FFmpeg to fix a high-severity CVE.
sonivox SONAME bump: Yaakov Selkowitz noted an upcoming update to sonivox 4.0.2, which will involve a side tag rebuild for its dependents.
CRI-O v1.37 and Go: Brad Smith reported that CRI-O v1.37.3 now requires Go 1.27.1 or newer, blocking updates on F43 and F44.
Heads-up: croaring 5.4.0 coming to Rawhide: Ben Beasley announced an ABI-breaking update for croaring to version 5.4.0, which will be coordinated with updates to python-pyroaring and groonga.
New contributor introductions
Aashish Jha: A software engineer at Microsoft working on Azure Confidential VMs, introduced himself and his work packaging azure-protected-vm-secrets as his first contribution to Fedora.
Developers and packagers can contribute by adopting orphaned packages like cmake and c-toxcore, or by helping identify tools that still depend on the legacy DNF4 stack for its planned removal. The Rust SIG needs help rebuilding applications that vendor affected versions of libraries like zstd and rustls, and porting others to secure releases. Web developers can submit fixes for missing dark-mode logos on the CoreOS page and review Maubot plugin pull requests. Finally, systems programmers can tackle complex hardware issues, such as debugging a hard lockup during GCC and Rust builds on RISC-V SpacemiT K3 hardware, or investigating a guest initialization failure on RISC-V KVM hosts.
Wow. Sam Altman did something fantastic. He motivated me. I’m using my AI workstation to work on Linux and experiment with AI!
Last winter I bought a new machine to edit my photos and learn AI on Linux. I’m still doing the photo editing part, but not the AI part. I wanted to keep going, but with my new work responsibilities I was too tired to spend energy on Learning. However, the statement about RAM by Sam Altman turned out to be a good motivation. No promises for regular new articles tough…
First of all, some RAM p*rn :-) 128 GB of RAM, from that 8 GB is set to be video RAM (but it could be set to anything from 512 MB to 96 GB…). The price of the little box doubled within a month of purchase simply due to the amount of RAM included. Sam & Co. have made RAM pretty much unaffordable…
root@fedora:~# free -h
               total        used        free      shared  buff/cache   available
Mem:           117Gi       2.2Gi       115Gi       8.0Mi       1.1Gi       115Gi
Swap:           39Gi          0B        39Gi
And finally, I’m working on Linux and AI again. Fedora is now updated from version 44 to 45 on the machine. And openSUSE Tumbleweed has also seen gigabytes worth of updates. Next up: getting AI workloads running again. I had to remove ROCm during upgrade: dependency problems, as far as I could see. I have just reinstalled the packages, and checking documentation…
I have Open WebUI installed from half a year ago, together with ollama. I tested both from the command line and from the Open WebUI: they work. Next time I will try to do something actually useful. :-)
root@fedora:~# ollama list
NAME               ID              SIZE      MODIFIED
llama3.2:latest    a80c4f17acd5    2.0 GB    24 minutes ago
gemma3:27b         a418f5838eaf    17 GB     7 months ago
granite4:latest    4235724a127c    2.1 GB    7 months ago
root@fedora:~# ollama show granite4
  Model
    architecture        granite
    parameters          3.4B
    context length      131072
    embedding length    2560
    quantization        Q4_K_M

  Capabilities
    completion
    tools

  License
    Apache License
    Version 2.0, January 2004
    ...

root@fedora:~# ollama --verbose
>>> who are you?
I am Hermes, a language model created by IBM to assist with a variety of tasks and answer questions on many topics. I strive to provide helpful, informative, and engaging responses
while being respectful and avoiding any harmful or unethical content.

total duration:       1.111554719s
load duration:        42.916831ms
prompt eval count:    12 token(s)
prompt eval duration: 23.637941ms
prompt eval rate:     507.66 tokens/s
eval count:           47 token(s)
eval duration:        1.020660833s
eval rate:            46.05 tokens/s
>>> print the first 10 prime numbers
The first 10 prime numbers are:

1. 2
2. 3
3. 5
4. 7
5. 11
6. 13
7. 17
8. 19
9. 23
10. 29

total duration:       1.434860225s
load duration:        47.052753ms
prompt eval count:    75 token(s)
prompt eval duration: 106.452539ms
prompt eval rate:     704.54 tokens/s
eval count:           58 token(s)
eval duration:        1.254814127s
eval rate:            46.22 tokens/s
>>> Send a message (/? for help)
AI in a miniature box :-)
You can read my older posts about my AI box under the toy tag.
In 2017, I wanted a small tool to change my laptop’s screen brightness.
I found one that worked, but Fedora did not have an RPM package for it.
So I set out to package it myself.
Fedora Copr made that first attempt far less stressful.
I wrote up that first package at the time: How I created my first RPM package in Fedora.
Copr remains one of the most useful tools in the Fedora contribution ecosystem.
This post is the introduction I wish I had read before I started.
It explains what Copr is, why packagers and users rely on it, and why its sandbox-like design matters now.
Copr, short for Community Projects, is a build service.
You give it a source RPM (SRPM), and it builds the package and hosts the results in a DNF or YUM repository.
Copr runs on Fedora infrastructure.
You can use the public instance at copr.fedorainfracloud.org.
If you use Arch Linux, Copr is the closest parallel to the Arch User Repository (AUR).
Both are community spaces where people share packages for others to use.
The AUR shares build scripts, and you build the package on your own machine.
Copr goes a step further.
It builds the RPM for you and hosts the repository, so you enable it and install with DNF.
You need a Fedora Account System (FAS) login to create a project.
You do not need special approval.
You can build for several Fedora releases, EPEL releases, and other targets in one step.
One SRPM can produce packages for many releases and architectures.
When I started, my biggest question was whether my package would build on the releases I cared about.
Koji is Fedora’s official build system, and I used scratch builds there to test.
Copr solved a different problem.
It let me host the package, install it on my own machine, and share a repository with others before I submitted anything for review.
Koji scratch builds caught a Fedora 27 failure that I fixed before I submitted my package for review.
Copr is not a replacement for that process.
It is a place to test first.
Recently, I used Copr to package something new I was working on.
I packaged a set of Markdown files, each one an Agent Skill, from the Fedora Agent Skills Library into a single RPM.
I published it in the AI/ML SIG Copr project and started sharing it for testing and use.
My plan is to package agent-skills officially in Fedora.
Copr made that first step possible because it gave me the fastest path to get an RPM into users' hands.
Users got a semi-official channel to install the package now, and I got real feedback while the official process moves along.
Copr works well as a sandbox.
Several design choices make that true.
Projects are separate.
Packages in your Copr project do not enter Fedora’s official repositories.
Your experiments stay in your own repository.
Packaging rules are relaxed.
Copr packages do not have to follow the Fedora Packaging Guidelines.
The guidelines are still recommended, but you can test ideas before you meet every rule.
Projects can expire.
You can set a project to delete itself after a number of days.
This suits short tests and one-off experiments.
Old builds are removed.
By default, Copr keeps one build per package and deletes the others after 14 days.
Projects on the newer Pulp backend keep the five most recent successful builds per package instead, so test projects do not grow forever.
A sandbox does not mean anything goes.
Copr is Free Software, and its repositories are signed.
However, the Copr maintainers do not review every package.
Before you install a package from a Copr project, check who maintains it.
If you can, look at the SRPM and spec file.
Projects distributed in Copr must also follow Fedora’s license rules.
Fedora is discussing a Council proposal for an Innovation Lifecycle.
The proposal includes a "sandbox stage" for experimental work that is too large for a single change proposal.
One of its stated goals is to isolate risk.
Experiments should be able to break without affecting the main distribution or the people who depend on it.
The proposal also notes that it does not yet define standard sandbox infrastructure.
Copr is not part of that proposal.
It already shows what a low-risk space for experiments can look like.
Work stays separate from official releases, feedback comes quickly, and strong packages can follow a path into Fedora.
I hope we keep that spirit as the larger discussion moves forward.
Distribution methods will change over time.
Right now, RPM packaging works well.
It is tested, proven, and well understood by Fedora contributors and users.
When we do not know how to share something new, RPM packaging is a path we can always fall back on.
It provides versioning and a distribution mechanism for large varieties of software.
Copr makes that RPM packaging fallback fast.
Copr gave me a low-risk way to learn packaging, and it can do the same for you.
If you have a package that is too early for Fedora, build it in Copr, share it, and learn from the results.
Thank you to everyone who maintains Copr and helps packagers use it.
Featured image generated by LLM-gen-AI using the OpenAI image API.
Joyce Moreno adaptou para português do Brasil a linda canção Talkin’ Bout a Revolution, de Tracy Chapman. Foi lançado em seu álbum Music Inside de 1990. O álbum não está disponível nas plataformas musicais, mas tem no YouTube da Joyce. Eis a letra que ela adaptou e a rara gravação.
Todos ‘tão falando de uma revolução Assim, baixinho
Sopra o vento nos seringais O que está marcado a fogo e aço nas usinas Sobe os morros, os becos das capitais E lá vai o buxixo nas esquinas
Todos ‘tão falando de uma revolução Assim, baixinho
Quem não tem nada vai querer Pegar o que é seu Quem não tem nada vai querer Ganhar o que perdeu
E corre, anda logo logo logo logo Corre corre corre corre corre, vai vai corre
Um dia vira a mesa, não dá prá evitar Uma revolução vem vindo Um dia vira a mesa e todos vão falar E já não vai ser baixinho
Across the Fedora ecosystem this week, the primary focus was the highly anticipated release of Fedora Linux 45, with teams including Release Engineering, Quality, Infrastructure, Server, and Docs finalizing release candidates, deploying updates, and immediately transitioning into Fedora 46 planning. Beyond the release cycle, a major shared initiative is the Bootable Image Unification ("Atomic Fusion") project, which dominated the agendas for the Council, Atomic, IoT, and Hummingbird groups as they prepared proof-of-concept demos. Infrastructure and tooling migrations also commanded significant cross-team collaboration; the Council, FESCo, and Quality teams are actively evaluating a potential transition from Bugzilla to a Forgejo-integrated issue tracker, while FESCo, Release Engineering, and ELN are coordinating the complete removal of the legacy DNF4 stack. Finally, adapting to upstream shifts and reinforcing system security were key technical themes, highlighted by FESCo and the KDE SIG managing the deprecation of X11 in KDE Plasma 6.8, alongside widespread security patching and cryptographic upgrades—such as the adoption of %openpgpverify—across the Perl, Rust, Cloud, and Infrastructure teams.
The highly anticipated release of Fedora Linux 45 is now officially available, as announced across the project forums, community posts, and the announce and devel-announce mailing lists. This milestone brings exciting updates across the ecosystem, including Fedora Workstation 45 featuring GNOME 51's reworked frame scheduling, and the KDE Plasma Desktop Edition highlighting KDE Plasma 6.8, the 30th-anniversary release of KDE. Hardware support continues to expand with the Fedora Asahi Remix 45 introducing out-of-the-box support for Apple M3 chips, alongside community-maintained RISC-V GA images available for testing, providing a great opportunity for contributors to report hardware enablement issues. For immutable OS users, detailed instructions are available for rebasing to Silverblue 45, while Fedora Atomic Desktops now utilize the new Anaconda Web UI and have migrated their repositories to the atomic-desktops organization, offering streamlined engagement for future contributors.
To avoid disruptive surprises, users and system administrators should note several key technical shifts in this release. The Anaconda installer now includes native support for Stratis storage configuration, simplifying advanced local storage management through an easy-to-use interface. Additionally, the unmaintained NetworkManager-vpnc and NetworkManager-fortisslvpn plugins are officially retired in Fedora 45, requiring users to migrate to actively supported VPN alternatives to maintain enterprise connectivity. Finally, on the infrastructure side, a brief planned server outage occurred on November 6th to reboot main VPN, email, and bastion servers into a new kernel for CVE mitigation, ensuring the ongoing security of the project's backend services.
Council
This week, the Council focused on the long-term future of Fedora's issue tracking and ongoing image unification efforts. A major discussion was initiated regarding the potential transition from Bugzilla to a Forgejo-integrated system (related to FESCO#3664), weighing the necessity of adopting modern, open-source infrastructure against concerns over Forgejo's current maturity and feature parity. Additionally, the agenda for the November 5th Bootable Image Unification ("Atomic Fusion") meeting was published, featuring a review of the project board, a seed proof-of-concept demo, and a planned presentation to the Workstation Working Group.
During this week, FESCo celebrated the release of Fedora 45 and announced upcoming elections. The committee held a meeting and processed numerous tickets, focusing heavily on the future of Fedora's issue tracking system, with extensive debate on whether to migrate to Forgejo or maintain a community-run Bugzilla instance. Other major topics included the coordinated removal of the legacy DNF4 stack and Modularity, as well as handling the deprecation of X11 support in KDE Plasma 6.8 for stable releases.
Decisions
Rejected the request to revert the removal of plasma-workspace-x11 from Fedora 44 and 45 in Ticket #3707.
Approved the pull request clarifying the responsibilities of the Engineering representative for the Council in Ticket #3613.
Rejected the Thin LTO Build Flag (F47) change proposal due to a lack of votes over five weeks in Ticket #3692.
Transferred maintainership of python-authlib to a new co-maintainer following the non-responsive maintainer policy in Ticket #3697.
Contribution opportunities
Community members are asked to help identify tools and scripts that depend on the legacy DNF4 stack or libmodulemd to assist with their planned removal in Ticket #3702.
Volunteers interested in maintaining a community-run Bugzilla instance are invited to put forward a proposal to the Fedora Infrastructure group, as discussed in Ticket #3664.
This week, Mindshare began early planning for the Virtual F46 Release Party, aiming for May 2027, to ensure a smooth event by crowd-sourcing ideas and recruiting role leads well in advance. Additionally, a community member reached out to organize an informal meetup for Fedora, CentOS, AlmaLinux, and RockyLinux contributors attending SFSCON 2026 in Bolzano, Italy.
Contribution opportunities
Help organize the Virtual F46 Release Party by volunteering for event team roles including Wrangler, Speakers, Design, Promotion & Content, and Production & Video. To get involved, join the #commops:fedoraproject.org Matrix room and reply to the ticket.
Connect with other community members at SFSCON 2026 in Bolzano, Italy, by joining the organizational thread.
Community feedback is welcome to improve the FIDO2 integration living document.
Contributors are encouraged to explore, test, and share improvements regarding FIDO2 integration for Polkit GUI prompts, as the original author left this partially incomplete.
Andrew Heath introduced himself to the Fedora community, sharing his extensive background in enterprise Linux, infrastructure automation, and image building. He expressed interest in contributing to packaging, image building, QA, and infrastructure automation. In response, he was welcomed by the community and advised to engage with the packaging team in their Matrix room to find a sponsor and initial tasks.
Contribution opportunities
Andrew Heath is seeking a packaging sponsor and looking for good first tasks, particularly in co-maintaining existing packages or picking up orphaned ones in the automation and sysadmin tooling space.
Opportunities exist to mentor or collaborate with Andrew in areas like image building (osbuild), QA testing, and infrastructure automation.
The Ambassadors group saw two forum discussions this week. A new contributor asked for help setting up their Fedora Campus Ambassador profile, including access to the wiki, Fedora People, and Libravatar, and received troubleshooting steps from the community. Additionally, a member started an organizational thread to coordinate a meetup for Fedora, CentOS, AlmaLinux, and RockyLinux contributors attending SFSCON 2026 in Bolzano, Italy.
Contribution opportunities
Contributors attending SFSCON 2026 in Bolzano, Italy (Nov 13-14) are invited to connect and team up with other community members.
A brief 20-minute meeting was held on November 3rd, following up on the agenda from October 27th. The original agenda included topics such as Fedora 45 blockers and exceptions, appstream-data automation, and DNF updating without wheel.
This week, the Fedora KDE group navigated discussions regarding Plasma 6.8 updates and overall desktop stability. Notably, the update to Plasma 6.8 officially drops X11 session support upstream, resulting in the obsoletion of kwin-x11 and plasma-workspace-x11 packages in Fedora 44. Users relying on X11 were advised that locking packages might prevent future UI updates, though community workarounds like Copr repositories have emerged. Additionally, the community discussed the marketing and perceived stability of Fedora KDE, with maintainers emphasizing that upstream KDE's rapid release cadence inherently involves trade-offs. Users seeking long-term support might look toward LTS distributions, while those experiencing bugs are encouraged to contribute directly to upstream bug resolution.
The replacement of kwallet with oo7-daemon is currently deferred for KDE Plasma and Plasma Mobile variants due to a lack of time for integration, as noted in Issue #700.
The screen package will not be added to the Kinoite base image; users are advised to use package layering or system extensions instead (Issue #723).
Contribution opportunities
Contribute to upstream KDE bug resolution to improve the stability of the Plasma desktop environment, as suggested in the discussion on Fedora KDE stability.
The Server Working Group celebrated the release of Fedora 45 Server and immediately began preparing for Fedora 46 by setting up a new testing project. A significant portion of the week was dedicated to the "Strengthening Server Updates" project, focusing on system resilience using LVM snapshots. Following the F45 release, the group closed numerous tracking tickets for system-wide changes and package updates.
In addition, the group discussed ongoing work on Ansible support, deciding to catch up on outstanding tasks over the next two weeks before reconvening on the topic. New contributors joined the meeting and immediately volunteered to help with testing and documentation efforts.
Decisions
The group agreed to continue using the ticket system for release testing (starting with Fedora 46), with optimizations to be discussed in the process. (Meeting Log, Mailing List)
For the "Strengthening Server Updates" project, the agreed next steps are testing the snapshot procedures, adding them as a step in post-installation, and preparing a Fedora Magazine article. (Meeting Log, Mailing List)
Members will use the coming weeks to catch up on outstanding tasks for the Ansible support project, deferring further discussion for 14 days. (Meeting Log)
Contribution opportunities
Testers are highly needed for the "System Resilience Using LVM Snapshots" procedures. Findings should be reported in Ticket #272.
Contributors are invited to help write a how-to style article for the post-installation section regarding server update resilience (Ticket #271).
There is an open opportunity to help draft a Fedora Magazine article about the "Strengthening Server Updates" project.
Assistance is welcome for the ongoing Ansible support project, specifically regarding the creation of an Ansible management CLI and configuring CI/CD runners (Ticket #268).
The Infrastructure team successfully navigated the Fedora 45 release, officially lifting the infrastructure freeze on November 4th. The week involved significant maintenance and troubleshooting, including resolving a storage-related outage on Fedora Forge by resizing its Persistent Volume Claim and NetApp volume, and investigating persistent login issues with Fedora Accounts (FAS) linked to FreeIPA OTP interactions.
In addition to routine maintenance, the team began planning the deployment of Siguldry to the production environment for RPM and OSTree signing. They also scheduled a mass upgrade and reboot of infrastructure servers for November 19th, and discussed ongoing efforts to optimize AWS resource usage and clean up untagged cloud instances.
Decisions
The infrastructure freeze for the Fedora 45 release was officially lifted on November 4th. (URL)
A mass upgrade and reboot of most infrastructure servers is scheduled for November 19th at 22:00 UTC, which will cause short outages for many contributor services. (URL)
Mirrors that transparently redirect HTTP traffic to HTTPS will be updated in MirrorManager to explicitly use HTTPS URLs only, improving crawler compatibility. (URL)
The Limestone Networks mirror (mirror.lstn.net) was disabled in MirrorManager due to an expired TLS certificate. (URL)
New FAS groups were created for chromium-sig, sysadmin-oraculum, napkinstack-labs, tablepro, and nanlang.
Contribution opportunities
Help is needed to investigate and resolve the persistent Unauthorized: bad credentials login errors on accounts.fedoraproject.org, which appear to be related to FreeIPA OTP module interactions. (URL)
Contributors can help clean up NetApp and host storage, including moving older releases to archive volumes, increasing partition sizes on alerting hosts, and compressing logs. (URL)
Assistance is requested to set up a Zabbix HTTP check for Oraculum and retire its old watchdog email alerts. (URL)
There is an opportunity to help set up Zabbix monitoring for the staging autosign service by implementing checks for AMQP, RPMs, OSTree, and CoreOS metrics. (URL)
Help is needed to create an announcebot Discourse service user and API key for sending compose announcements. (URL)
A new contributor expressed interest in helping with virtualization and infrastructure tasks, presenting an opportunity for onboarding and mentorship. (URL)
Fedora 45 has been officially released, with the team handling final release candidate composes, signing the IoT compose, and managing post-release cleanup and synchronization. During the rollout, a minor synchronization issue with the Labs images was manually resolved, and discussions were held to better align fedora_distro_aliases and releases.json updates in future cycles.
In addition to the release, the team resolved several infrastructure and build issues. This included fixing broken RHEL 9 repositories for EPEL 9 builds, addressing a bug where Rawhide .treeinfo files were missing kernel image information, and removing several underpowered x86_64 hosts from the heavybuilder channel to prevent Out-Of-Memory errors during large builds like Chromium.
Several underpowered x86_64 build hosts were removed from the heavybuilder channel to prevent OOM errors during large package builds. (URL)
A fix was implemented and backported in Pungi to ensure .treeinfo files contain kernel image information, restoring virt-install functionality for Rawhide. (URL)
The EPEL 7 meson tagging order issue will not be fixed because EPEL 7 is End of Life. (URL)
Provide feedback and identify any infrastructure applications still relying on DNF4 for the F46 Change Proposal to Remove DNF4, libdnf, and libmodulemd.
The Quality team successfully verified and tested the release candidates for Fedora 45, officially declaring it "GO" for release, alongside publishing and updating the Common Issues. The team also hosted a Test Week for Linux Kernel 7.3, encouraging users to test the kernel rebase on Fedora 44 and 45.
This week, the Websites and Apps team resolved an issue where the x86_64 folder was missing from the Fedora 45 Labs download page by syncing the content and rebuilding the site. The team also successfully closed the F45 beta release tracker and opened tickets for UI improvements, including fixing dark-mode logos on the CoreOS page and improving contrast in the Fedora Media Writer section. In addition, a community member reported that the captive portal check URL is on an HSTS-preloaded domain, which breaks Wi-Fi login detection; the infrastructure team plans to move it to another domain in the future. Finally, a bug in Fedocal where events with past repeat-end dates fail to appear was identified and resolved for a user.
Decisions
The infrastructure team plans to move the captive portal check URL to a different domain to resolve HSTS preload list conflicts that break Wi-Fi login detection (Ticket #13629).
Contribution opportunities
Review requested for the Fedora Maubot/Zodbot plugin for cookies: PR #257 and PR #161.
Help needed to fix missing dark-mode variant logos on the CoreOS page (Work item #439).
Help needed to improve the contrast of download items in the Fedora Media Writer section (Work item #438).
The Design team focused on the initial sketches for the F46 wallpaper, discussing the use of alternative geometric shapes for bubbles while prioritizing iridescence. They also reviewed poster designs, noting layout inconsistencies and the need for better text hierarchy and spacing, and successfully closed the F45 Virtual Release Party graphics ticket. Additionally, the team discussed accessibility improvements for international audiences, agreeing to spell out acronyms like DEI. In the Matrix chat, automated alerts indicated that the "Fix time of day path" action failed in both the main and f45-backgrounds branches of the backgrounds repository.
Decisions
Iridescence will remain the primary visual focus for the F46 wallpaper bubbles, regardless of the final geometric shape chosen.
The Fedora logo and mascots will not be included in the wallpaper to comply with guidelines and avoid clutter; instead, mascot concepts will be repurposed for promotional art.
Acronyms such as DEI (Diversity, Equity, and Inclusion) will be spelled out in designs to improve accessibility and clarity for international audiences.
The Fedora Docs team successfully navigated the Fedora 45 release, merging numerous release notes covering updates like GNOME 51, KDE Plasma 6.8, and various system changes. Following the release, the team is restructuring the release notes repository to stop versioning; future notes will be built directly from the main branch, displaying the three most recent supported releases on a single page while older notes remain available via the Internet Archive.
Additionally, the team is revamping its infrastructure by transitioning the site-builder repository to build from main rather than prod. They are also evaluating "Bruce," a new broken-link detection script, for CI integration to automatically generate static reports and eventually file issues for broken links. Furthermore, discussions are ongoing regarding Antora component consolidation to allow cross-repository module inclusion and integrating the Fedora Design Suite documentation.
Decisions
Stop versioning the release notes repository and build them exclusively from the main branch, preserving only the three most recent supported releases (Meeting, Issue #449).
Transition the site-builder repository (formerly docs-fp-o) to drop the prod branch and build the production site directly from main (Meeting, Issue #61).
Integrate the "Bruce" link-checking script into the CI pipeline in phases, starting with generating a static HTML report before moving to automated issue creation (Issue #69).
Retain docsbuilder.sh as a wrapper for local documentation previews while updating the underlying container to support Aarch64 and dropping npm dependencies (Issue #65).
Contribution opportunities
Review and merge open pull requests for the Fedora 45 Release Notes, as requested by community members (Forum Topic).
Help replace legacy {partialsdir} includes with the partial$ syntax across documentation repositories to align with current Antora standards (Issue #38).
Assist in documenting the Fedora Docs site build and monitoring process for the prod and stg branches (Issue #59).
Provide feedback on the proposed integration of the Fedora Design Suite documentation into the official Fedora Docs website (Issue #68).
Test and provide feedback on the proposed Antora module inclusion methods (component merge vs. Antora extension) to improve cross-SIG documentation discoverability (Issue #66).
In a discussion regarding the koneko license and copyright, Cristian Le followed up on concerns regarding copyrighted sprites included in the project, specifically characters from Cardcaptor Sakura and the BSD Daemon. Following previous advice to drop the artwork, Cristian confirmed that the issue has been flagged to the upstream developers and that the problematic sprites will be removed via a downstream patch if necessary.
Decisions
The copyrighted sprites (Cardcaptor Sakura and BSD Daemon) in koneko must be removed, either by upstream or via a downstream patch. (Source)
This week, the COPR team successfully completed a scheduled server upgrade on November 3rd, bringing new features and bug fixes to the platform. Following the upgrade, an ongoing data migration to Pulp temporarily affected several projects (alphabetically from "sar" to "siddharthvipul1"), causing some 404 errors and pending builds which are expected to resolve as the migration progresses. Additionally, the team discussed the timeline for IPv6 support on the Pulp instance, estimating a fix for early next year, and provided support for building bleeding-edge Rust packages with vendored crates in Copr.
Proceeded with the ongoing data migration to Pulp, which temporarily causes 404 errors and pending builds for affected project owners while their specific data is being migrated.
Contribution opportunities
Help is welcome to set up automation that recognizes new copr-cli tags being pushed, creates the sdist tarball, and automatically uploads it to PyPI.
This week in EPEL, discussions highlighted a known daily cache delay in the CentOS Stream repo for Fedora's Koji, which temporarily caused scratch build failures in epel9-next (URL). Security updates were a major focus, with uv (v0.13.5) and ruff (v0.17.2) being pushed to stable for the EPEL10 leading branch to address multiple RUSTSEC vulnerabilities and the eMudhra CA compromise (URL). Additionally, pipx is being retired from EPEL9 due to 23 security vulnerabilities that cannot be practically patched on the older Python 3.9 stack (URL). Other activities included the EPEL 10.2 retirement announcement, progress on bringing mailman to EPEL10, and participation in the release party CLE presentation.
Decisions
The pipx package is being retired from EPEL9 due to severe security vulnerabilities and incompatible Python version requirements (URL).
Versions 0.13.5 of uv and 0.17.2 of ruff were pushed to stable for the EPEL10 leading branch to address critical security flaws (URL).
The ELN SIG held a meeting on November 3, 2026 (meeting log). Key updates include the complete removal of dnf-4 from ELN, the completion of rebuilds for libxml2 2.15, and the replacement of perl-Params-Util with perl-Params-SomeUtil. Additionally, the Content Resolver now displays daily diffs. On the RISC-V front, approximately 140 packages have been built, though progress is currently paused pending fixes for toolchains like gcc, golang, and rust. The group also discussed ongoing issues with KDE Discover (Issue #633) and the unmaintained libappstream-glib (Issue #486), as well as upcoming libical4 rebuilds.
Decisions
dnf-4 has been completely removed from ELN and will not be included in RHEL 11.
perl-Params-Util has been replaced with perl-Params-SomeUtil.
This week, the Atomic group focused on bootable image unification ("Atomic Fusion") with an upcoming presentation to the Workstation WG and a seed proof-of-concept demo (Meeting Agenda). In addition, there are ongoing discussions about rebasing Fedora Atomic Desktops on Fedora Bootc base images, which will modernize the build flow (Issue #88).
Several technical issues were also addressed, including a bug where systemd-oomd fails to intervene during memory exhaustion on Kinoite 44 (Issue #130), a syncing issue with the Fedora Cosmic-Atomic image (Issue #137), and an anomaly where rpm-ostree stable commits occasionally bundle packages from the updates-testing repository (Discussion).
Decisions
Systemd services in Atomic images will use ConditionPathIsMountPoint=/sysroot instead of checking for /run/ostree-booted to ensure compatibility with the composefs backend (Issue #133).
The Fedora Cosmic-Atomic update failure was identified as a release tooling script issue and moved to a releng ticket (Issue #137).
Contribution opportunities
Help is needed to file a releng ticket to investigate why rpm-ostree stable commits occasionally pull packages from the updates-testing repository (Discussion).
Contributors are invited to help create and review test cases for the upcoming Fedora Atomic Desktops Test Week, covering installations and upgrades via rpm-ostree, gnome-software, and plasma-discover (Issue #87).
Assistance is requested to test and provide a controlled reproducer for a memory exhaustion bug where systemd-oomd fails to intervene on Kinoite 44 (Issue #130).
This week, the CoreOS team celebrated the general availability release of Fedora Linux 45. The testing stream has been successfully rebased to version 45.20261030.2.1, bringing notable changes such as native Butane support in Ignition, the use of chunkah for better layer reuse in container images, the relocation of RPM repository configs out of /etc, and the update to Podman 6.0. The team is currently in the post-release cleanup phase and has already opened the tracker for the upcoming Fedora 46 rebase. In addition to the release activities, the team addressed several critical bugs and infrastructure tasks. A fix for the IPv4 TCP use-after-free vulnerability (CVE-2026-98432) was shipped in the stable stream, and workarounds are being tested for an ext4 /boot corruption issue affecting upgrades. The team also approved a proposal to switch Konflux-driven streams to a Jenkins poll-based import model to simplify downstream pipeline management.
Decisions
Released Fedora Linux 45 and rebased the testing stream to version 45.20261030.2.1.
This week, the IoT group focused on bootable image unification and resolving a system upgrade issue. Laura Santamaria shared the agenda for the "Atomic Fusion" meeting, which included a seed proof-of-concept demo and a presentation to the Workstation Working Group (URL). Additionally, a user reported a bug where upgrading to Fedora 45 fails due to a missing GPG public key in rpm-ostree. The issue was resolved locally by updating the gpgkeypath in the fedora-iot.conf file to point to /usr/share/pki/rpm-gpg/ (URL).
This week, the Cloud group focused on image configuration and distribution infrastructure. A key update involves adding the SUSPEND_SAFE_FPR guest OS feature to Fedora Cloud GCP images to address a page reporting suspend UAF vulnerability (CVE-2026-74481), which is now being applied to new nightly builds (Issue 449). Additionally, following the announcement that the HCP Vagrant Registry is shutting down on December 31, the group is discussing setting up a self-hosted Vagrant registry to ensure continued availability of Vagrant boxes, drawing inspiration from AlmaLinux's recent implementation (Issue 450).
Contribution opportunities
Help is needed to set up a self-hosted Vagrant registry for Fedora to replace the retiring HCP Vagrant Registry before December 31 (Issue 450).
The Hummingbird group prepared for their upcoming "Atomic Fusion" (bootable image unification) meeting on November 5, 2026. The agenda included a project board review, a potential demo of a seed proof-of-concept, and preparations for presenting to the Workstation Working Group.
The AI/ML SIG discussed new package reviews, notably OpenShell, an NVIDIA-driven tool for agent sandboxing. Packaging updates were announced, with the latest AI and ROCm packages now available in COPRs for released distributions, and new LLM servers like Gufo and Colibri landing in Rawhide. The group is also collaborating on a Fedora Magazine article highlighting the use of the pi-coding-agent to help Fedora contributors, which may evolve into a broader series exploring how AI is utilized within the Fedora ecosystem. Other chat discussions touched on integrating hardware volunteering for AI tasks and addressing Wayland compatibility issues for freelance time-tracking tools.
Decisions
The latest AI and ROCm packages are now available for general use in COPRs for released Fedora distributions.
New LLM servers, Gufo and Colibri, have been packaged and are available in Rawhide.
The SIG will pitch and publish a Fedora Magazine article focusing on the pi-coding-agent, potentially kicking off a series on how AI is used in Fedora.
The Fedora RISC-V team successfully finalized and announced the Fedora 45 RISC-V GA images, including Server, Container, and Cloud variants. A major focus this cycle was clarifying kernel recommendations: the 'Omni' kernel is highly recommended for most physical hardware to avoid issues like PCIe/NVMe data corruption on JH7110-based boards (e.g., VisionFive 2), while the 'Generic' kernel is primarily targeted at QEMU and a select few boards. Meanwhile, the bootstrap of Fedora ELN (Enterprise Linux Next) for RISC-V is making significant progress, with Koji fully configured for ELN and RVA23 channels, and over 140 packages already built. The team is also actively debugging hardware-specific issues, including GCC build hangs on the SpacemiT K3 and a QEMU KVM guest initialization bug.
Decisions
The 'Omni' kernel is officially recommended for most physical RISC-V hardware (including VisionFive 2) to prevent potential data corruption with certain PCIe/NVMe storage configurations, while the 'Generic' kernel is recommended primarily for QEMU.
Koji hub policies and channels have been updated to route RVA23-specific builds appropriately, enabling the ongoing Fedora ELN bootstrap.
Contribution opportunities
Help is needed to debug and resolve a hard lockup issue occurring during GCC ELN and Rust builds on SpacemiT K3 hardware (disabling Transparent Huge Pages is currently being tested as a workaround).
Contributors can assist with upstreaming vendor patches from the Omni kernel to the Mainline kernel to improve out-of-the-box hardware support.
Developers familiar with QEMU and KVM can help investigate a guest initialization failure when using -cpu max on RISC-V KVM hosts.
This week, the Perl group focused heavily on package maintenance, dependency management, and security enhancements. Maintainers implemented source signature verification using openpgpverify for packages like perl-Net-DNS and mod_perl. Several packages received routine version bumps, including perl-Mozilla-CA, perl-CGI, and perl-Tk-Text-SuperText. Additionally, contributors collaborated on adjusting dependencies for downstream distributions, such as adding build conditionals for Lexical::Var in perl-Exporter-Tiny and disabling optional dependencies in RHEL builds for perl-File-ShareDir.
Decisions
Merged a build conditional in perl-Exporter-Tiny PR #2 to use Lexical::Var via Recommends instead of Requires on older Perl versions.
The Python group discussed reversing the deprecation of python-dateutil following a new upstream 4.0.0 release. Contributors agreed to undeprecate the package and patch out its new tzdata dependency to rely on the system's time zone data instead. Additionally, a proposal was made to automatically set LD_LIBRARY_PATH in %py3_test_envvars to streamline testing, and feedback is currently being sought on potential breakages.
Decisions
Undeprecate the python-dateutil package following the new upstream 4.0.0 release.
Patch out the tzdata dependency in python-dateutil 4.0.0 to rely on system timezone data instead.
The Rust group focused heavily on security updates and package rebuilds this week, addressing multiple RUSTSEC advisories across crates like zstd, zip, ruzstd, rustls, and webpki-roots. Additionally, there was a mailing list discussion regarding a request to package crubit for Fedora and EPEL to support Chromium builds, though it faces significant hurdles due to its reliance on nightly Rust and unstable compiler internals.
Decisions
The request to package crubit for Fedora to support Chromium builds is currently blocked, as the required cc_bindings_from_rs tool depends on a nightly compiler and unstable compiler internals, which cannot be shipped in Fedora (Mailing List).
The effort to update packages to ruzstd v0.9 to address RUSTSEC-2026-0344 has been completed and the tracking ticket is closed (Issue 42).
Contribution opportunities
Assist with rebuilding or updating applications not co-maintained by the Rust SIG that vendor affected versions of zstd, zstd-safe, rustls, and webpki-roots (Issue 48, Issue 43, Issue 46).
Help port applications currently depending on older versions of zip (v0.6), rustls (v0.21/v0.22), and webpki-roots (v0.25) to their latest secure releases (Issue 47).
From F45 onwards: Fedora-maintained (self-updating) hardening...: Chris announced a new self-updating kernel hardening feature available from Fedora 45 onwards. Designed for both beginners and advanced users on GNOME and KDE, it applies security-first configurations automatically, overriding certain defaults like yama-ptrace-enable. Users discussed its interaction with Atomic variants, Toolbox containers, and potential impacts on specific applications, with Chris noting that a new #hardening tag will be used to consolidate feedback.
Btrfs-patrol: snapshots before every dnf transaction...: JC shared updates on btrfs-patrol, a snapshot and rollback tool tailored for Fedora's default Btrfs layout. It automatically takes read-only snapshots before dnf5 transactions and allows for one-command rollbacks while ensuring the restored snapshot has the necessary kernel modules to boot.
GitLab access for inactive accounts: Shaun McCance announced that due to Fedora exceeding its seat limit on GitLab, accounts with no activity in the past 12 months will be downgraded to view-only access. This will free up seats for active teams without deleting any data, and edit access can be restored if needed.
Proposal: Optional CJK input method support for Fedora's kmscon console: Skyter Lin proposed adding optional CJK (Chinese, Japanese, Korean) input method support for Fedora's new kmscon virtual console, having successfully tested Traditional Chinese using uim-fep and m17n. Jocelyn Falempe confirmed the technical feasibility of using Super+Space for toggling and suggested starting by adding a kmscon-uim man page.
Some news about the Audinux activity for october: Yann Collette provided an October update for the Audinux repository, highlighting the addition of 29 new audio-related packages and 155 package updates. Notable additions include several AI-generated standalone applications like bytebeat, ibniz-rust, and mx44-rust, which underwent security and performance audits.
New packages in Fedora Linux (October 2026): Miroslav Suchý shared a comprehensive list of newly added packages to Fedora Linux during October 2026, generated using the rawhide-changes.py script.
F46 Change Proposal: Usermode2 (self-contained): On the devel-announce mailing list, Aoife Moloney shared a Fedora 46 Change Proposal to replace the C implementation of the usermode package with a memory-safe Rust rewrite of its userhelper and consolehelper tools. The rewrite serves as a drop-in replacement while dropping several obsolete standalone GUI tools, and developers discussed ensuring the Rust standard library safely handles the SUID execution environment.
Is packaging a fork permissible?: Łukasz Wojniłowicz asked if packaging a fork under the same name as the upstream project is permissible. Developers clarified that while it is allowed and sometimes necessary for dormant projects, the spec file should clearly explain the relationship between the original repository and the fork to avoid confusion.
F46 Change Proposal: Libical4 (system-wide): On the devel-announce mailing list, Aoife Moloney announced a Fedora 46 Change Proposal to update the libical library to its 4.x series, which introduces an API/ABI break from the 3.x series. Milan Crha and Michel Lind coordinated the necessary package rebuilds in a side tag, noting that only a subset of dependent packages required direct updates.
Heads-up: %gpgverify -> %openpgpverify PRs are coming: Jakub Jelen notified maintainers about upcoming pull requests to migrate packages from %gpgverify to the new %openpgpverify macro, which uses Sequoia's sqv for upstream source signature verification. He advised maintainers to check if their upstream keys need refreshing or updating to comply with current cryptographic standards.
Orphaned packages looking for new maintainers (on devel-announce): Several orphaned packages were adopted, including tunneler and openfortivpn, while Dominik Mierzejewski advised against adopting rubygem-drake due to obsolescence.
Orphaned - singularity-ce: David Trudgian orphaned singularity-ce as the upstream project reached EOL, recommending apptainer as a suitable replacement.
Package updates
libcdio 2.4.0 update comes with new sonames: Adrian Reber announced an upcoming update to libcdio 2.4.0 in Rawhide, which bumps several SONAMEs and requires rebuilding dependent packages in a side tag.
Soname bump: libcamera: Milan Zamazal planned an update to libcamera 0.8.0 in Rawhide, noting ABI changes that require rebuilding pipewire-plugin-libcamera, libcamera-apps, and plasma-camera.
openapv SONAME bump: Dominik Mierzejewski announced an update to openapv that includes a SONAME bump and API changes, requiring a rebuild of FFmpeg to fix a high-severity CVE.
sonivox SONAME bump: Yaakov Selkowitz noted an upcoming update to sonivox 4.0.2, which will involve a side tag rebuild for its dependents.
CRI-O v1.37 and Go: Brad Smith reported that CRI-O v1.37.3 now requires Go 1.27.1 or newer, blocking updates on F43 and F44.
Heads-up: croaring 5.4.0 coming to Rawhide: Ben Beasley announced an ABI-breaking update for croaring to version 5.4.0, which will be coordinated with updates to python-pyroaring and groonga.
New contributor introductions
Aashish Jha: A software engineer at Microsoft working on Azure Confidential VMs, introduced himself and his work packaging azure-protected-vm-secrets as his first contribution to Fedora.
Developers and packagers can contribute by adopting orphaned packages like cmake and c-toxcore, or by helping identify tools that still depend on the legacy DNF4 stack for its planned removal. The Rust SIG needs help rebuilding applications that vendor affected versions of libraries like zstd and rustls, and porting others to secure releases. Web developers can submit fixes for missing dark-mode logos on the CoreOS page and review Maubot plugin pull requests. Finally, systems programmers can tackle complex hardware issues, such as debugging a hard lockup during GCC and Rust builds on RISC-V SpacemiT K3 hardware, or investigating a guest initialization failure on RISC-V KVM hosts.
Although AI has become a very mainstream topic in the last three years, the concept of sovereign AI has not reached the mainstream yet.
The problem isn’t only its low profile, but also that it is often used as a sovereignty theater rather than real sovereignty.
The first thing to realize is that sovereignty is not a boolean characteristic; it is a multidimensional spectrum, and any conversation that treats it as boolean fails to be informative.
Although the exact number of dimensions is arbitrary, and different people might consider different ones, I prefer a three-dimensional model.
Hello everyone. Another week gone by and some longer form recapping.
Fedora 45 released!
Fedora 45 was released on tuesday. Things went mostly smoothly,
with just some few things needing tweaking. There was also some
Labs missing from the master mirror sync (fixed) and torrents
(will be fixed soon).
Our master mirrors were doing 20-25Gbps a second for tuesday and
wed, so definitely lots of bits flowing.
I think this is a pretty solid release, I hope you like it too.
Post release unfreeze
After the release was all out, we ended our Infrastructure freeze.
I merged/deployed 8 pull requests that were blocked by the freeze,
and processed some ticket backlog. More of that next week.
The "AI" security apocolypse
So, there's been a lot of discussion in social media/around about
all the new security vulnerabilities that are being found and the
effect that has been having on open source projects and maintainers.
It's quite relentless over the previous months for many folks,
and has a lot of ill effects, including:
Always having to be ready for security bugs
No more disclosure time/embargoes, so you have to release fast
Inability to have time to actually work on features or
regular maint, have to focus on security all the time.
Thats all well known, but I thought I would add the effect
this has on operations folks. Case in point, late last week
anthropic announced they had found a criticial bug in the linux
kernel (all versions at the time after 4.14 or so). This became
CVE-2026-98432, with a super high CVSS score (9.8 out of 10!).
I looked at it last weekend and anthropic in their announcement said:
"In our proof of concept, it takes 48 minutes to leak a kernel pointer
and another five minutes to reach the shell command execution."
But it doesn't actally provide any details. Whats the connection?
whats the kernel? Whats the hardware?
Everything else I saw said no one had seen a public exploit yet.
Forgive me for not trusting a company that has a large incentive
to talk up their tooling and a track record of breathless announcements
that turn out to not be exactly what they say.
In any case, I upgraded most of out public facing servers as soon as their
was a RHEL update, along with our openshift clusters. However
there were a few that I wanted to actually schedule an outage
for just in case there was issues, so I scheduled that for friday.
I also had to wait until after release, because I didn't want to break
things right before our release went out.
By the time friday rolled around: There were 2 new kernel updates
fixing more CVEs and 2 more openshift updates (fixing the same).
Granted that it's nice to be in a state where you can just reboot
anything as soon as updates come along, but there's cases where
that is just not a very great idea (like if you are about to do
a major release and don't want to possibly break things).
Anyhow, I am sure it's not going to get better for a while, but
I hold out some hope that someday we will have found all the obvious
bugs and it will slow down.
We took some time to interact with the booth visitors at the IndiaFOSS 2026 conference's Red Hat Community Booth. While representing Fedora Project on the event grounds and handing out special swags, we were the conduits for the community's sentiments both as users and contributors to free and open source software projects like that of ours.
11:44am IST
Manifest A
Open Alternatives LibreOffice Calc could be used as a zero-cost in-place software alternative to Office Excel for taxation, compliance and logistics.
Software Interoperability Proprietary formats from Office Excel are a barrier for cross-platform collaboration and open formats should hence be preferred.
12:12pm IST
Manifest B
Beginner Friendly Starting from Microsoft Windows, it is crucial to account for a smoother learning curve while seeking next alternatives for operating systems.
Individual Requirements Alternatives can be tried in virtual machines and live environments to check if they fit their personal needs or if other variants are required.
Innovative Approach The fast release cycle does not necessarily mean that Fedora Linux is unstable as all the updates are duly tested before being published.
Gradual Exploration A good starting point with a general purpose GNU/Linux distribution like ours could be helpful in someone learning about the ecosystem.
12:20pm IST
Manifest C
Personal Exploration After jumping in the deep end with Arch Linux's installation steps, a CA student found Fedora Linux's installation steps to be refreshing.
Troubleshooting Resources The active community helped them resolve software and hardware issues, with Realtek WiFi adapters on their Lenovo LOQ laptop device.
Getting Occupied With the information on Join SIG and FAS accounts, they were asked to participate and find their circle of interest within the community.
Desktop Experience Their personal usage with i3 window manager and various dotfiles let them to truly make the Fedora Linux experience as their own.
12:36pm IST
Manifest D
EndeavourOS Movement Seeking a fresh desktop environment experience from GNOME, they moved from Fedora Linux to EndeavourOS, only come back later.
Positive Experience Acknowledging Fedora Linux's capabilities, they admitted it to be mostly GNOME, and hence, the KDE variant was suggested to them.
Encouraging Contributors They appreciated how they could get started with contributing meaningfully to Fedora Project with zero technical expertise to begin with.
Software Availability Some moved away from Fedora Linux as certain proprietary cyber security tools were not available packaged in the official repositories.
Diverse Opportunities Community driven mentorship guidance helped individuals with designing, testing, documenting, triaging etc. to help Fedora Project.
Existing Contributions They previously helped with software packaging build systems for 3D modelling tools and libraries, with UPI support for various platforms.
Contribution Motivations Their participation was a passion project rooted in community connection and निष्काम सेवा or selfless service, with freedom and sharing.
Maintainer Challenges Human reviews for generated contributions made it harder for maintainers to provide meaningful efforts expended to guide contributors.
Controversial Opinions Excessive generation significantly undermines meaningful contributions, with constant struggles for finding time to review everything.
Genuine Contributions Open source software movement thrives on genuine participation, shared ownership, constructive feedback and welcoming communities.
02:02pm IST
Manifest E
Personal Problems The participant shared contributions to basic call conversation recording for Android phones and generic kernel images for Snapdragon.
Appreciating Community Without any factors that discouraged them from participation, they had blessings for multimedia suite like VLC and MPV in the open.
Exploring Alternatives From Endeavour Linux to Fedora Linux, they experimented with window managers and desktop environments to see what fits the best.
Proprietary Limitations Users cannot investigate issues and resolve problems in proprietary codebases, thus making it crucial to explore what everyone uses.
02:10pm IST
Manifest F
Atomic Future Immutable distributions are sought to eventually replace traditional installations with package managers leading to greater reliability.
Habitual Transitions Widespread adoption would require workflow changes to users habituated to classic commands and hence, this will take some time.
Reproducible Configuration Tooling like Ignition and Butane enable shareable customization with recommendation to directly use YAML configuration for processing.
System Provisioning While NixOS provides greater advanced controls, the Fedora CoreOS suite covers the requirements without a steep learning curve.
Bootable Containers Image mode operating systems are gradually becoming the refreshed normal with the layering packages for purpose specific systems.
Immutable Systems Comparing against previous controversial changes that ended up being standards, the immutable systems would soon end up being one.
02:20pm IST
Manifest G
Recommended Discovery The participant started using Fedora Linux on their friend's recommendation before moving on to join many parts of the community.
Contemporary Relevance For a general purpose operating system, it is important to have access to recent updates in the rapidly evolving software landscape with AI.
Improving Experience They sought Fedora Linux as a user friendly operating system and its versatility and stability are what keeps drawing users towards it.
Welcoming Community The openness and patience of the mentoring members made them want to stay back in the community and keep helping in their ways.
Friends Foundation From Friends, Features, Freedom and First – they preferred the Friends foundation the most as it resonated with why they contribute here.
General Usability Instead of treating zero price as an excuse for poor usability, open source should invest more into design thinking and user experience.
02:34pm IST
Manifest H
Better Performance A third year engineering student from PES University Bengaluru went from Microsoft Windows to Fedora Linux for its lightweightness.
Installation Experience The setup process was relatively straightforward with the Anaconda WebUI but needed more troubleshooting for fingerprint readers etc.
Community Resources Using the official subreddit and Fedora Discussions for initial issues, they gradually began answering questions from fellow members.
Contributing Back After being introduced to FAS accounts and Join SIG, they intend to contribute more into updating documentation and other resources.
Free Alternatives They had found home in the LibreOffice Suite and are appreciative of the open formats to help collaborate with other platforms equally.
Difficult Balance From an over-involved experience of Microsoft Windows, they mentioned how Fedora Linux stayed out of their way while they worked.
Exploring Editions They were introduced to the multiple variants and distinct editions of Fedora Linux for various purposes like servers and embedded etc.
Encouraging Contributors They made it a point to promote Fedora Linux among their circles as a means to give back to the free and open source software resources.
Exploration Decade Another participant explored over fifty alternatives in the previous decade before going with a custom build of Manjaro Linux now.
Experienced Perspectives With an appreciation for Fedora Linux's overall simplicity and software availability, they are looking forward for image mode.
Immutable Appeal Fedora Silverblue and other immutable alternatives helped shape consumer operating systems like SteamOS with a similar architecture.
Problem Solving Multiple individuals can come together to solve problems that can be iterated upon by others, thus finding strength in the community.
User Generated A great example was that of Arch User Repository (AUR) and Collection of Private Repositories (COPR) to allow for that to happen.
Hardware Compatibility When official companies hold back their hardware devices, community members have come together to deliver solutions for the same.
Vendor Partnerships Partnering with Slimbook, Lenovo, Framework and others have allowed Fedora Linux to be available out-of-the-box in the laptops.
Innovative Stability The conversation concluded with recognizing how Fedora Linux balances innovation and stability at the cost of missing release dates.
03:00pm IST
Manifest I
Developer First Since using it for almost over two years now, they appreciated the recent build updates that Fedora Linux provided for development.
Update Frequency Frequent updates every after six months can be offputting for some, but that is exactly what makes them recommend Fedora Linux.
Experimental Discovery From using GNU/Linux distributions on Raspberry Pi to daily driving Fedora Linux on resource limited hardware devices, they grew.
Community Career They plan to make a career in free and open source software communities at some time after learning the ropes from the mentors.
03:08pm IST
Manifest J
Technological Compliance The two participants from the legal sector assisted the startups establishing platforms and navigating regulatory challenges.
Legal Oversight Software companies sometimes avoid compliance requirements if they comply with one jurisdiction since it costs a fortune.
Generated Misuse Generated terms of services without a foundational understanding and substantial review can only end up in a bad manner.
Professional Expertise Lawyers invest considerable efforts in deep research and due diligence to understand the clients produce before providing advice.
Limitation Violations SaaS providers copy products from competing services by barely making superficial changes rather than addressing issues.
Regulatory Responsibility Financial pressure should not be an excuse to minimize necessary legal expenditure, as an oversight could cause great fines later.
Crawling across the sky
All of my crew and I are
Wanted for the highest form of treason
For questioning authority
Demanding we sweat and bleed
And slave our lives away, then call it freedom
So hoist up the Jolly Roger
We’re taking a ride
Take back the life that they denied
For glory or gold
We sail across the galaxy
Our sovereign starship flying free
Forever, our treasure
Taken from plutocracy
We’ve all got mouths to fucking feed
So it’s a pirate’s life for me
So you’ve got to make a choice
If you will raise your voice
For all of those who suffer now in silence
‘Cause the crown would never hesitate
To laugh while we suffocate
Then ask us why we must reply with violence
So hoist up the Jolly Roger
We’re taking a ride
Take back the life that they denied
For glory or gold
We sail across the galaxy
Our sovereign starship flying free
Forever, our treasure
Taken from plutocracy
We’ve all got mouths to fucking feed
So it’s a pirate’s life for me!
Yeah! It’s a pirate’s life for me!
Lyrics from Glory or Gold by Galactikraken & Jonathan Young
The forge.fedoraproject.org is down because of space issue. We are currently working on
fixing it. You can watch the progress in https://matrix.to/#/#forge:fedoraproject.org
For many years, I have managed all my systems with Ansible.
For a similar amount of time, I have used Nebula as my VPN of choice, so I can always connect securely to all my systems, even on the move.
There are no official Ansible modules for Nebula, so over the years many people asked me how I manage it.
I changed my approach over time.
Although my previous iterations worked, I wasn’t satisfied enough to share the details.
I’m now at a point where I think the process is fairly good, so here I am.
Fedora 45 is now available ! 🎉
So let’s see what this new release for the Fedora Atomic Desktops variants includes for Silverblue, Kinoite, Sway Atomic, Budgie Atomic and COSMIC Atomic.
The only remaining repo on GitLab.com/fedora is the one used to build the unofficial bootable container images (gitlab.com/fedora/ostree/ci-test).
The migration of this repo is planned as well.
Anaconda Web UI
The Atomic Desktops installer ISOs now use the new Anaconda WebUI.
This follows the same change that occured for Fedora Workstation 42 and Fedora 43 Spins.
This also enables remote installation of a system using a Web browser on another machine over HTTPS.
Installer images (ISO) and disk images built by Image Builder
The installer images (ISO) are now built by Image Builder.
While there should not be any immediate visible changes, this will help us move to the bootable container images in the future.
This also enables us to offer pre-installed disk images for Silverblue and Kinoite.
Those images are currently in preview and only those variants are covered for now.
They are the only ones with a first boot experience from a disk image.
Fedora Budgie Atomic comes with the brand new version 10.10.3 of Budgie Desktop: New Favorites in Budgie Menu, re-introduced Keyboard applet with Wayland support, massive improvements to our desktop view, primary monitor selection, and more!
As always, I heavily recommend checking them out, especially if you feel like some things are missing from the Fedora Atomic Desktops and you depend on them (NVIDIA drivers, extra media codec, out of tree kernel drivers, etc.).
If you are interested in more security focused variants, I recommend taking a look at the secureblue project.
What’s next
Roadmap to Bootable Containers and bootc / CoreOS / Atomic unification
A lot of work is happening to make the transition to Bootable Containers as smooth as possible for our existing users.
You can look at the roadmap for this transition at atomic-desktops#26.
Most of the progress in this release cycle was (again) focused on getting our bootable container images ready for general consumption in Fedora.
A part of this work is being able to build them reliably in the Fedora Infra.
The people involved in the bootc, CoreOS and other Atomic variants are working on this effort as part of the new Atomic SIG.
See atomic#137 and the project board.
Making it easier to derive images into Fedora Remix images
Work is in progress to make it easier to create derived container images from the Fedora Atomic Desktops images, notably in order to comply with the logo and branding policy.
Once this is ready, we may start publishing “Fedora Remix” branded container images of the Fedora Atomic Desktops.
Those images would not include official Fedora branding and would thus be better suited for projects that want to layer their changes on top.
If you are interested in contributing to Fedora Atomic Desktops, here are some bugs that we will have to fix in the short term.
We would greatly appreciate help with:
Fixing root mount options (atomic-desktops#72):
This is a long standing and mostly invisible bug that impacts performance.
Moving away from nss-altfiles (atomic-desktops#108):
This is another long standing source of issues that new users regularly face.
Where to reach us
We are looking for contributors to help us make the Fedora Atomic Desktops the
best experience for Fedora users.
I am sure I am not the only in this situation. There are more Open Source
maintainers and defenders who are in the same situation. From last July I
started poking into various libraries/projects/deployments of open source
projects to find vulnerabilites, and it became very tiring 16+ hours long days.
As of today morning I found 90+ such issues, many are in projects written or
used by Sunet, many has other bigger userbase too.
The things I am poking at are boring Infrastructure pieces. "National Research
and Education Network/NREN" (s) in every country are not the top receivers of
grant money. Small number of people working years after years to keep the
infrastructure on.
And not many are that lucky to have access to the modern LLMs or knowldge on
how to use them to find and fix issues. I am lucky and thankful to Anthropic
and OpenAI that they provided me with access to latest models with capabilities
to do this work. But, not many has it, this crates too much pressure in my
mind, and for sure friends told me similar stories (in other fields). To defend
Sweden (or your respective country) we will need more capabilites and
compute/hardware and people willing to do this work. Where we are not dependent
on another country's political views to defend our own country.
Many will say open weight models will solve this. If you only think about
capabilities, yes they are catching up. Funniest part for me was that I used an
open weight model and found 4 different zero days in 4 java libraries (they are
all now fixed) and chained them to bypass validation of particular checks for
digital signatures as my first finding (using LLMs) back in July. But, using
open weights are either not allowed at every place or folks don't have
hardware. We need powerful hardware to be able to defend. A lot of decisions
have to made in various levels of our societies to make this happen. And I
don't think we will not see much progress so easily.
On the other hand attackers using $25 and access to same capabilities to
attack. Nation state level actors are now many more times efficient due to both
brain power and money they can spend.
I hope the pace of finding new bugs will come down a bit in 2 years, but not
sure how many of us will not be burnt out by then.
Note: many of you may ask me about technical details of the findings or what I
am using specifically. That would require multiple other posts for me to
explain, but you can just start poking with whatever you have. For example
today morning's finding to another big project was using just
Pi. No special sauce. Just poking and providing input to the
model to guide it. But if I just go by numbers, then OpenAI models helped me
the most in finding vulnerabiities and then to write exploits to demonstate to
the maintainers. I am missing the capabilties to do proper pentesting though.
We took some time to interact with the booth visitors at the IndiaFOSS 2026 conference's Red Hat Community Booth. While representing Fedora Project on the event grounds and handing out special swags, we were the conduits for the community's sentiments both as users and contributors to free and open source software projects like that of ours.
09:36am IST
Manifest A
Zorin OS vs. Fedora Linux Both use GNOME and yet Zorin OS offers a more Windows-like experience out of the box, while Fedora Linux provides a comparatively stock GNOME experience.
Software Freshness Zorin benefits from Ubuntu's stability, but its software packages can be considerably older as compared to Fedora Linux where updates arrive much faster after testing.
Fedora's Positioning The distribution bridges the contentious gap between beginner friendly distributions and faster moving ones, by balancing software freshness and overall stability.
Raspberry Pi Fedora support ARM64, and various other architectures, including Raspberry Pi, but the releases can take longer to arrive sometimes due to the closed kernel sources.
Experimentation Encouraged Fedora Linux is worth trying on any hardware for general purpose users but there is no need to replace whatever works if it already meets your requirements.
Foundational Freedom Users should explore GNU/Linux distributions based on curiosity and learning rather than simply switching for the sake of it to face workflow problems.
Distribution Movements Fedora Linux is a natural intermediate step before experimenting with more advanced GNU/Linux distributions like Arch Linux, Gentoo Linux and others.
Experimental Education College students should consider experimenting with GNU/Linux distributions to learn the internal parts without risking their everyday systems in the process.
Generative Enhancements Generative systems should be treated as a tool that enhances human capabilities rather than a replacement for human involvement in software development.
Usage Responsibility Generated codebase require proper requirements gathering, human oversight and deep auditing to ensure that the result does not lead to poor outcomes.
Learning Fundamentals Beginners should avoid excessive dependence on AI tooling, in order to help long-term capabilities and build strong fundamentals with basic documentation.
Dependent Consumerism Free services can create dependency with providers potentially introducing restrictions with enshittification, so users should remain mindful of privacy concerns.
Privacy Engagements In Fedora Project community, we value meaningful conversations and useful feedback over collecting emails in exchange for our promotional merchandise.
Getting Started Documentation writing and quality assurance are excellent beginner starting points, as they help with bridging the gap between users and contributors.
Advanced Contributions They can gradually move towards issue tracking, design creation, codebase writing and community management, as they grow familiar with the ecosystem.
Container Security Podman comes bundled with Fedora Linux with the support for rootless execution of container payloads along with first class SELinux support.
10:00am IST
Manifest B
Ubuntu Linux vs. Fedora Linux Fedora Linux releases every six months while Ubuntu LTS prioritizes five year support and hence, the former delivers newer software much faster.
Upstream First Fedora Linux aims to ship upstream updates within a shorter timeframe, often around a week after release, whereas Ubuntu paces behind for stability.
Innovation Focus Fedora Linux distinguishes itself with adopting emerging technologies and leading the pack before they become mainstream across other distributions.
Controversial Standards Systemd adoption was controversial at its time, but it soon found its way into major contemporary GNU/Linux distribution shortly after our example.
Enterprise Security Using SELinux, Fedora Linux provides strong system-level protection, with Podman for lightweight rootless container execution against Docker.
Staying Current Newer development tools with Fedora Linux releases help users and builders to cater for the stakeholders of today and tomorrow, and not of yesterday.
10:08am IST
Manifest C
Leading Edge Fedora Linux prioritizes delivering recent software updates while maintaining usability and stability of the general GNU/Linux distribution experience.
Balancing Updates Fedora Linux aims to deliver updates relatively quickly, typically within a week of its upstream release, while holding back broken updates until fixed.
Community Maintenance With a heavy reliance on voluntary developers and community maintainers, Fedora Linux attempts shipping updates as quickly as possible.
Security Updates CVE addressing security patches are prioritized and pushed as soon as they are ready to be shipped to minimize the vulnerability exposure period.
Quality Assurance An integrated update management system allows community members to test proposed updates before wider GNU/Linux distribution adoption ensues.
Getting Involved Contributors can help test updates without from virtual machines and live environment without replacing their existing operating systems here.
10:16am IST
Manifest D
Educational Institutions Fedora Linux is adopted in St. Joseph Engineering College, Mangalore across their computer systems, for student development and general purpose.
Contribution Pathways One need not be a programmer to contribute to Fedora Project, when they can do so through designing, documentation, testing, triaging and other ways.
Packaging Technologies Flatpak's fully open-source nature and support for federated infrastructure is preferred over Snap's centralized software serving approach by the folks.
Upstream Innovation Fedora Linux introduces technologies such as Pipewire and Wayland that eventually greatly influence other GNU/Linux distributions down the road.
Enterprise Contributions Fedora Linux serves as the upstream foundation for CentOS Stream and ultimately, Red Hat Enterprise Linux so the contributors have the agency.
Career Opportunities Students are encouraged to explore opportunities through Red Hat's career portal and learn about various roles within the organization communities.
10:26am IST
Manifest E
Agent Security How do we identify compromised polluted autonomous agents within a swarm of AI agents operating towards a shared initially provided goal?
Ring Architecture How elevated memory access privileges could help understand the potential fault when malicious activity reaches the deeper memory layers?
Without Logging Identifying malicious autonomous agents without execution footprints can be quite the challenge with the entire ecosystem being treated as a black box.
Compromise Detection Determining memory access history, and isolating affected regions could help prevent further compromise, which was also in Anthropic's research.
10:48am IST
Manifest F
CentOS Evolution From having limited upstream contribution to having unlimited midstream exposure, CentOS Stream helped evolve the entire ecosystem.
Midstream Bridge CentOS Stream helps bridge Fedora Linux and Red Hat Enterprise Linux by being an intermediate platform for development and security.
10:56am IST
Manifest G
Personal Experience Using Fedora Linux first as daily drivers motivates people to contribute back whenever they face issues or identify opportunities in their tools.
Giving Back Support received by Fedora Project motivates people to contribute in whatever manner they can, while solving real world problem statements.
General Affordability In various government schools, free and open source software can make technology accessible to students' and teachers' existing devices.
GNU/Linux Entertainment Various people still depend on Microsoft Windows for graphic drivers and video games particularly from vendors like AMD and/or NVIDIA.
Community Driven Communities collaborate to address security issues and software bugs that have been identified by users who have faced similar incidents.
Starting Small People should not feel pressured to become core maintainers immediately when they could start small with fellow contributors to rely on.
11:20am IST
Manifest H
StratOS Linux Using Bedrock Linux to integrate components from multiple alternatives to allow users to combine packages, kernels, components in here.
Kernel integration Fedora Linux's official kernel was demonstrated to be integrated with custom dotfiles and SwayFX environment to include DNF installer.
11:26am IST
Manifest I
Battleship Gaming Gridlock, a battleship inspired videogame written purely in Rust and GTK4 UI with minimal memory footprint was demonstrated live.
Development Environment They mentioned how Fedora Linux enabled them to build on the most recent codebase and toolkit, with just how fast we ship the updates.
11:34am IST
Manifest J
Open Background With humble start from beginner alternatives to moving into NixOS from the first year of the college education, NixOS was used for four years.
Blue Experience After initial experiments with Manjaro Linux, Fedora Linux outgrew the popularity for its mature ecosystem and maintenance practices it has.
NixOS Adoption Finally settling into NixOS after years of distrohopping, it was realized that the NixOS workflow suits them the best with Fedora Linux after it.
Declarative Configuration Like NixOS, Fedora Linux's Atomic Variants also support declarative configuration, thus providing them alternatives for trying it again.
Contribution Potential Interest was expressed in helping Fedora Linux evolve more on system configuration drawing inspiration from contemporary alternatives.
Proposed Pathways With an encouragement to document ideas, identifying issues and opening discussions through the active Fedora Atomic forums, they departed.


 Installation: read the
 To be noticed :


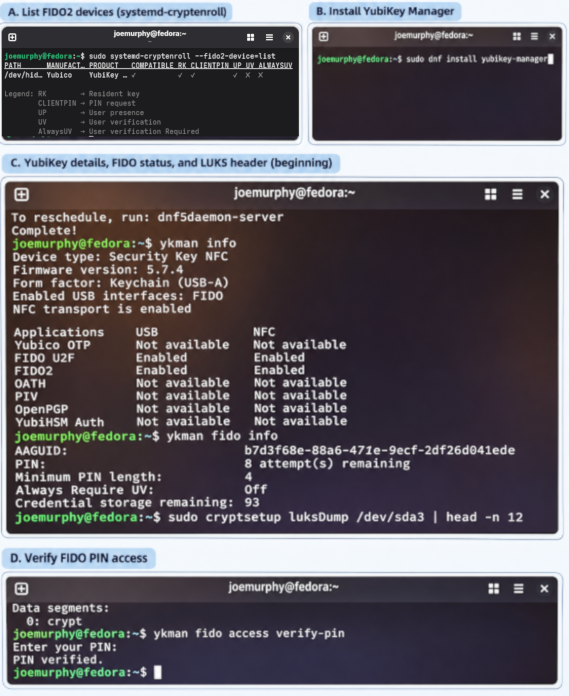
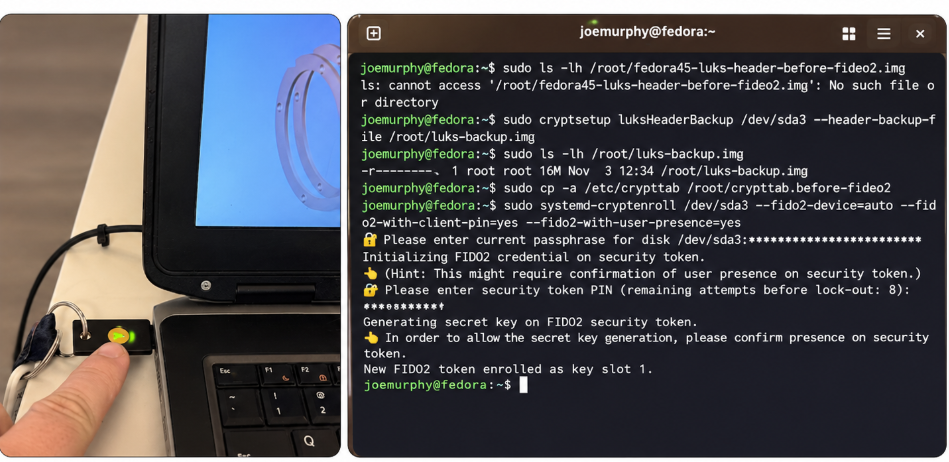
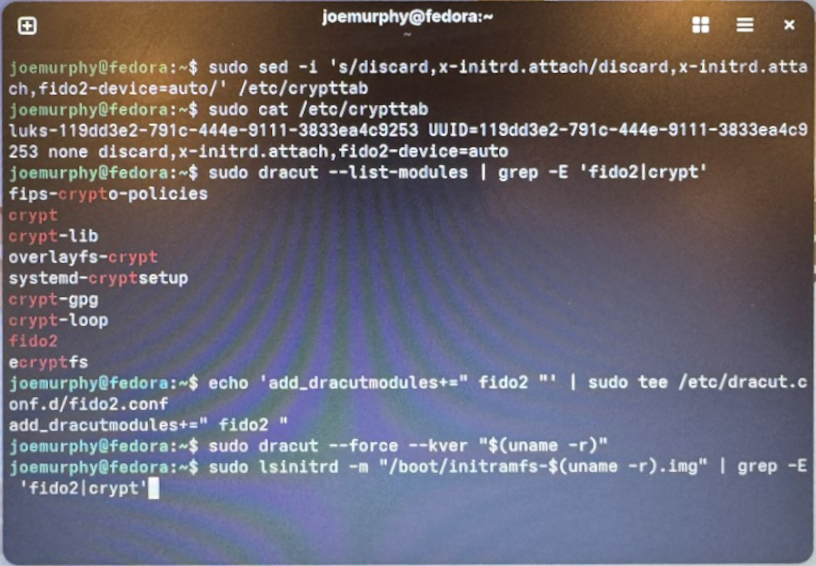

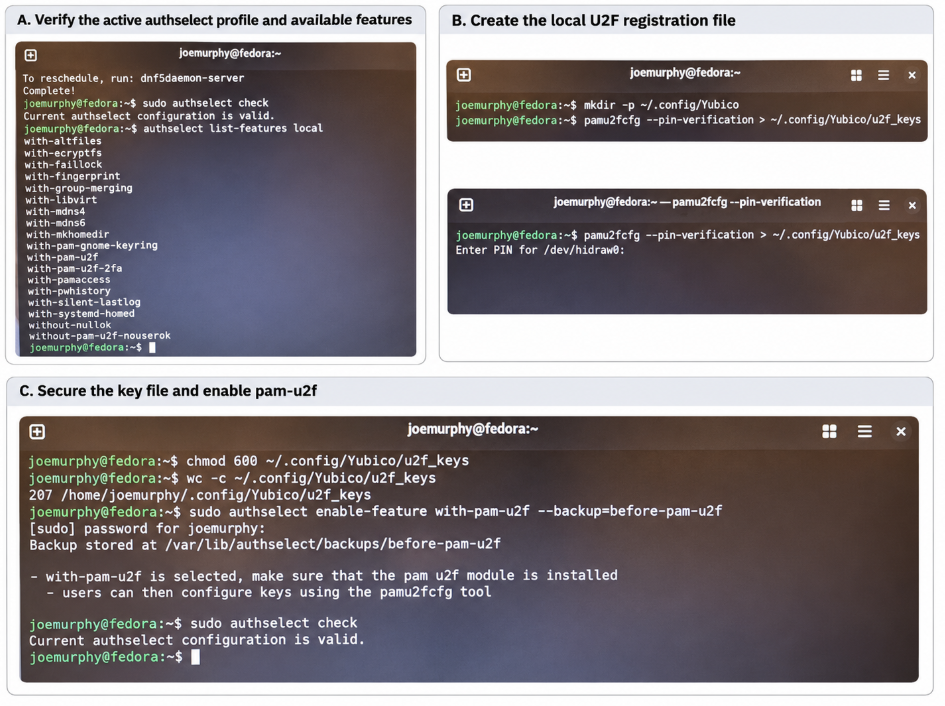
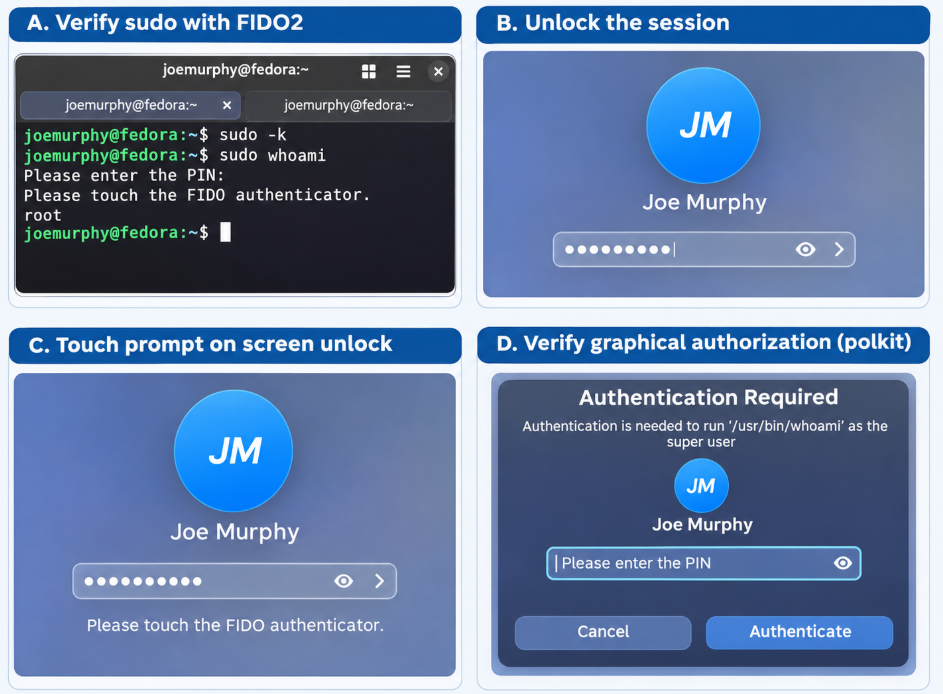


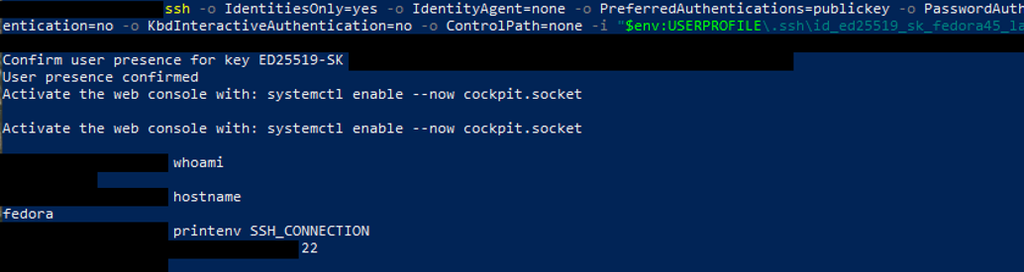




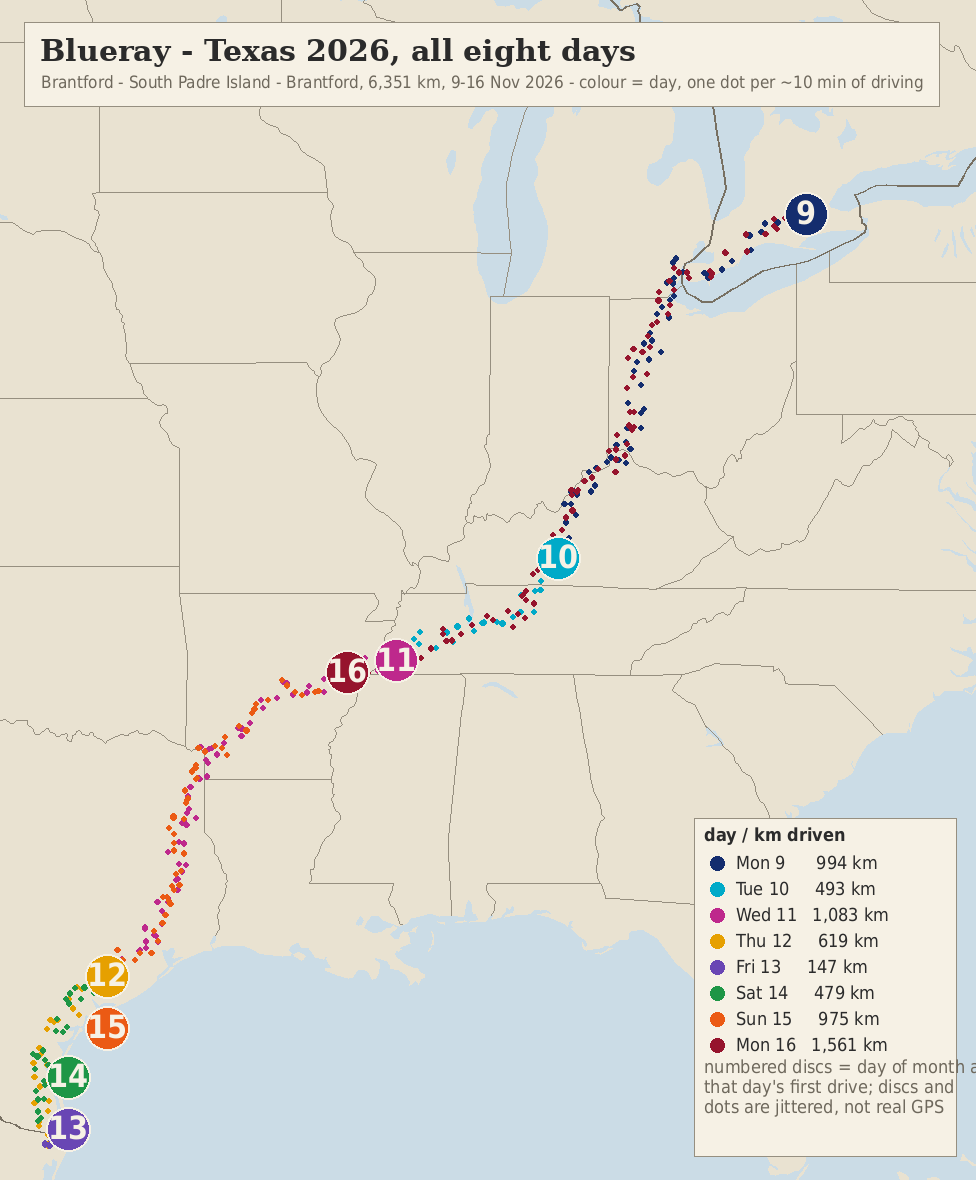
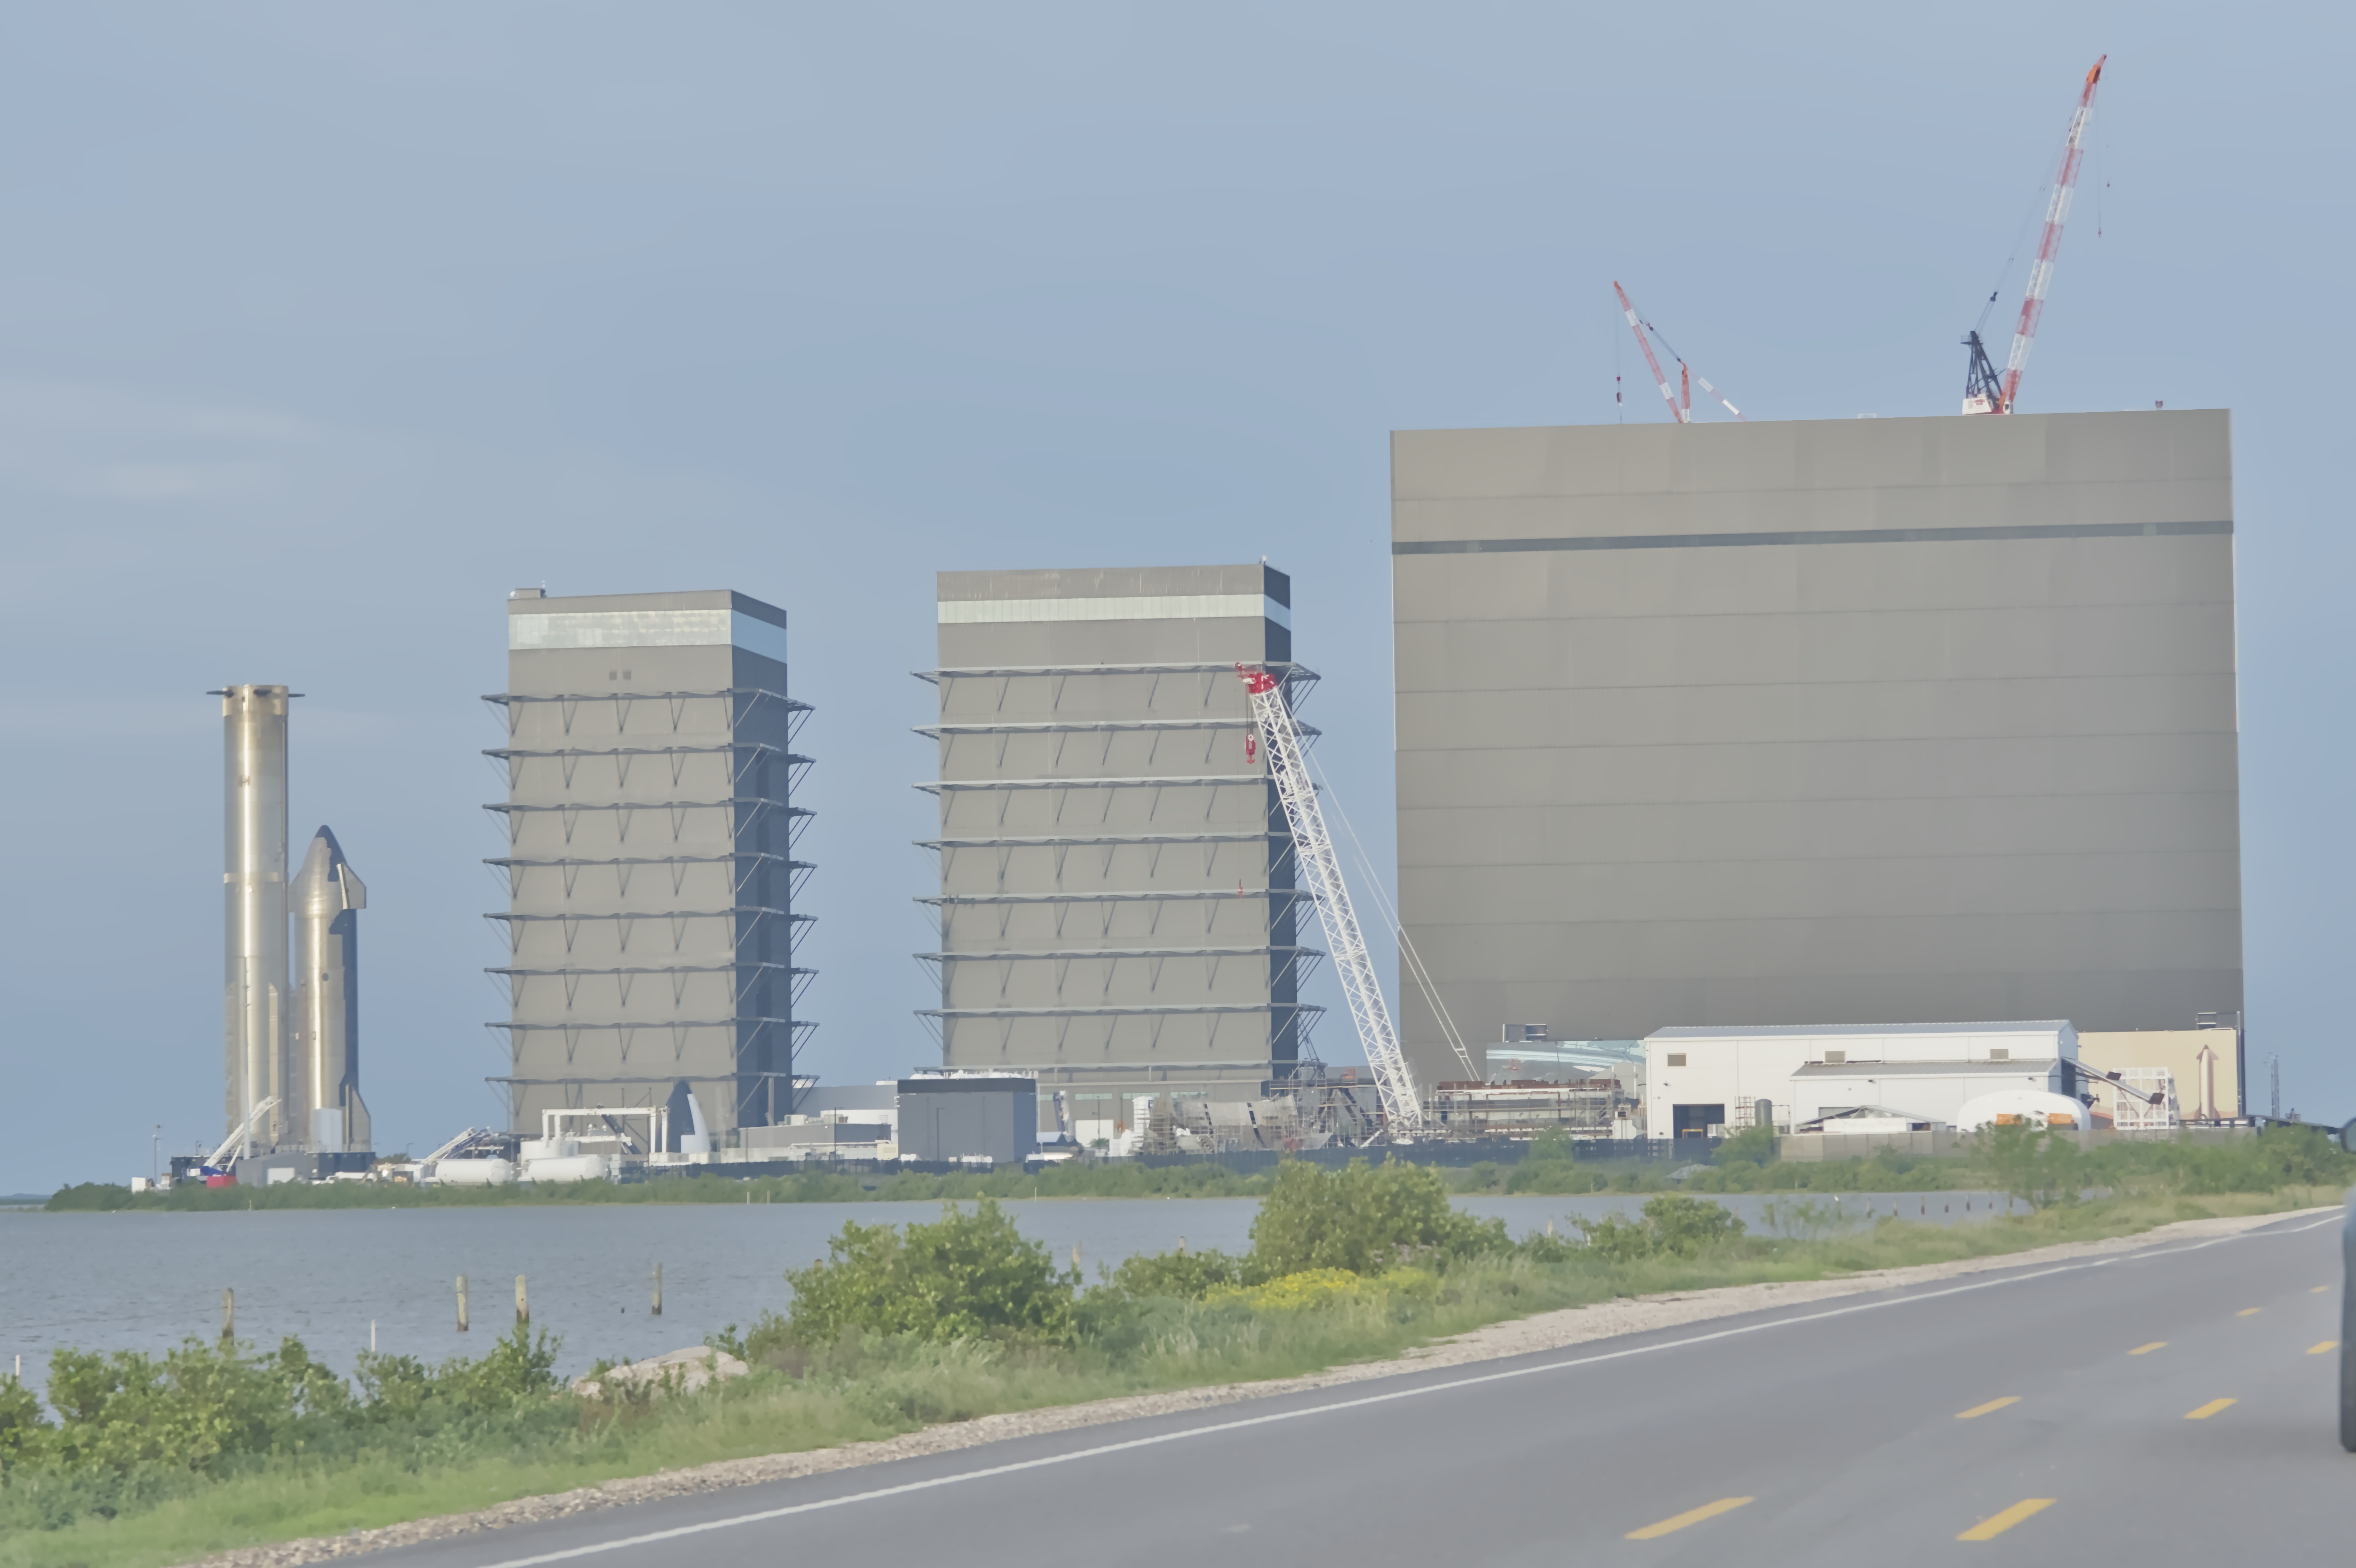
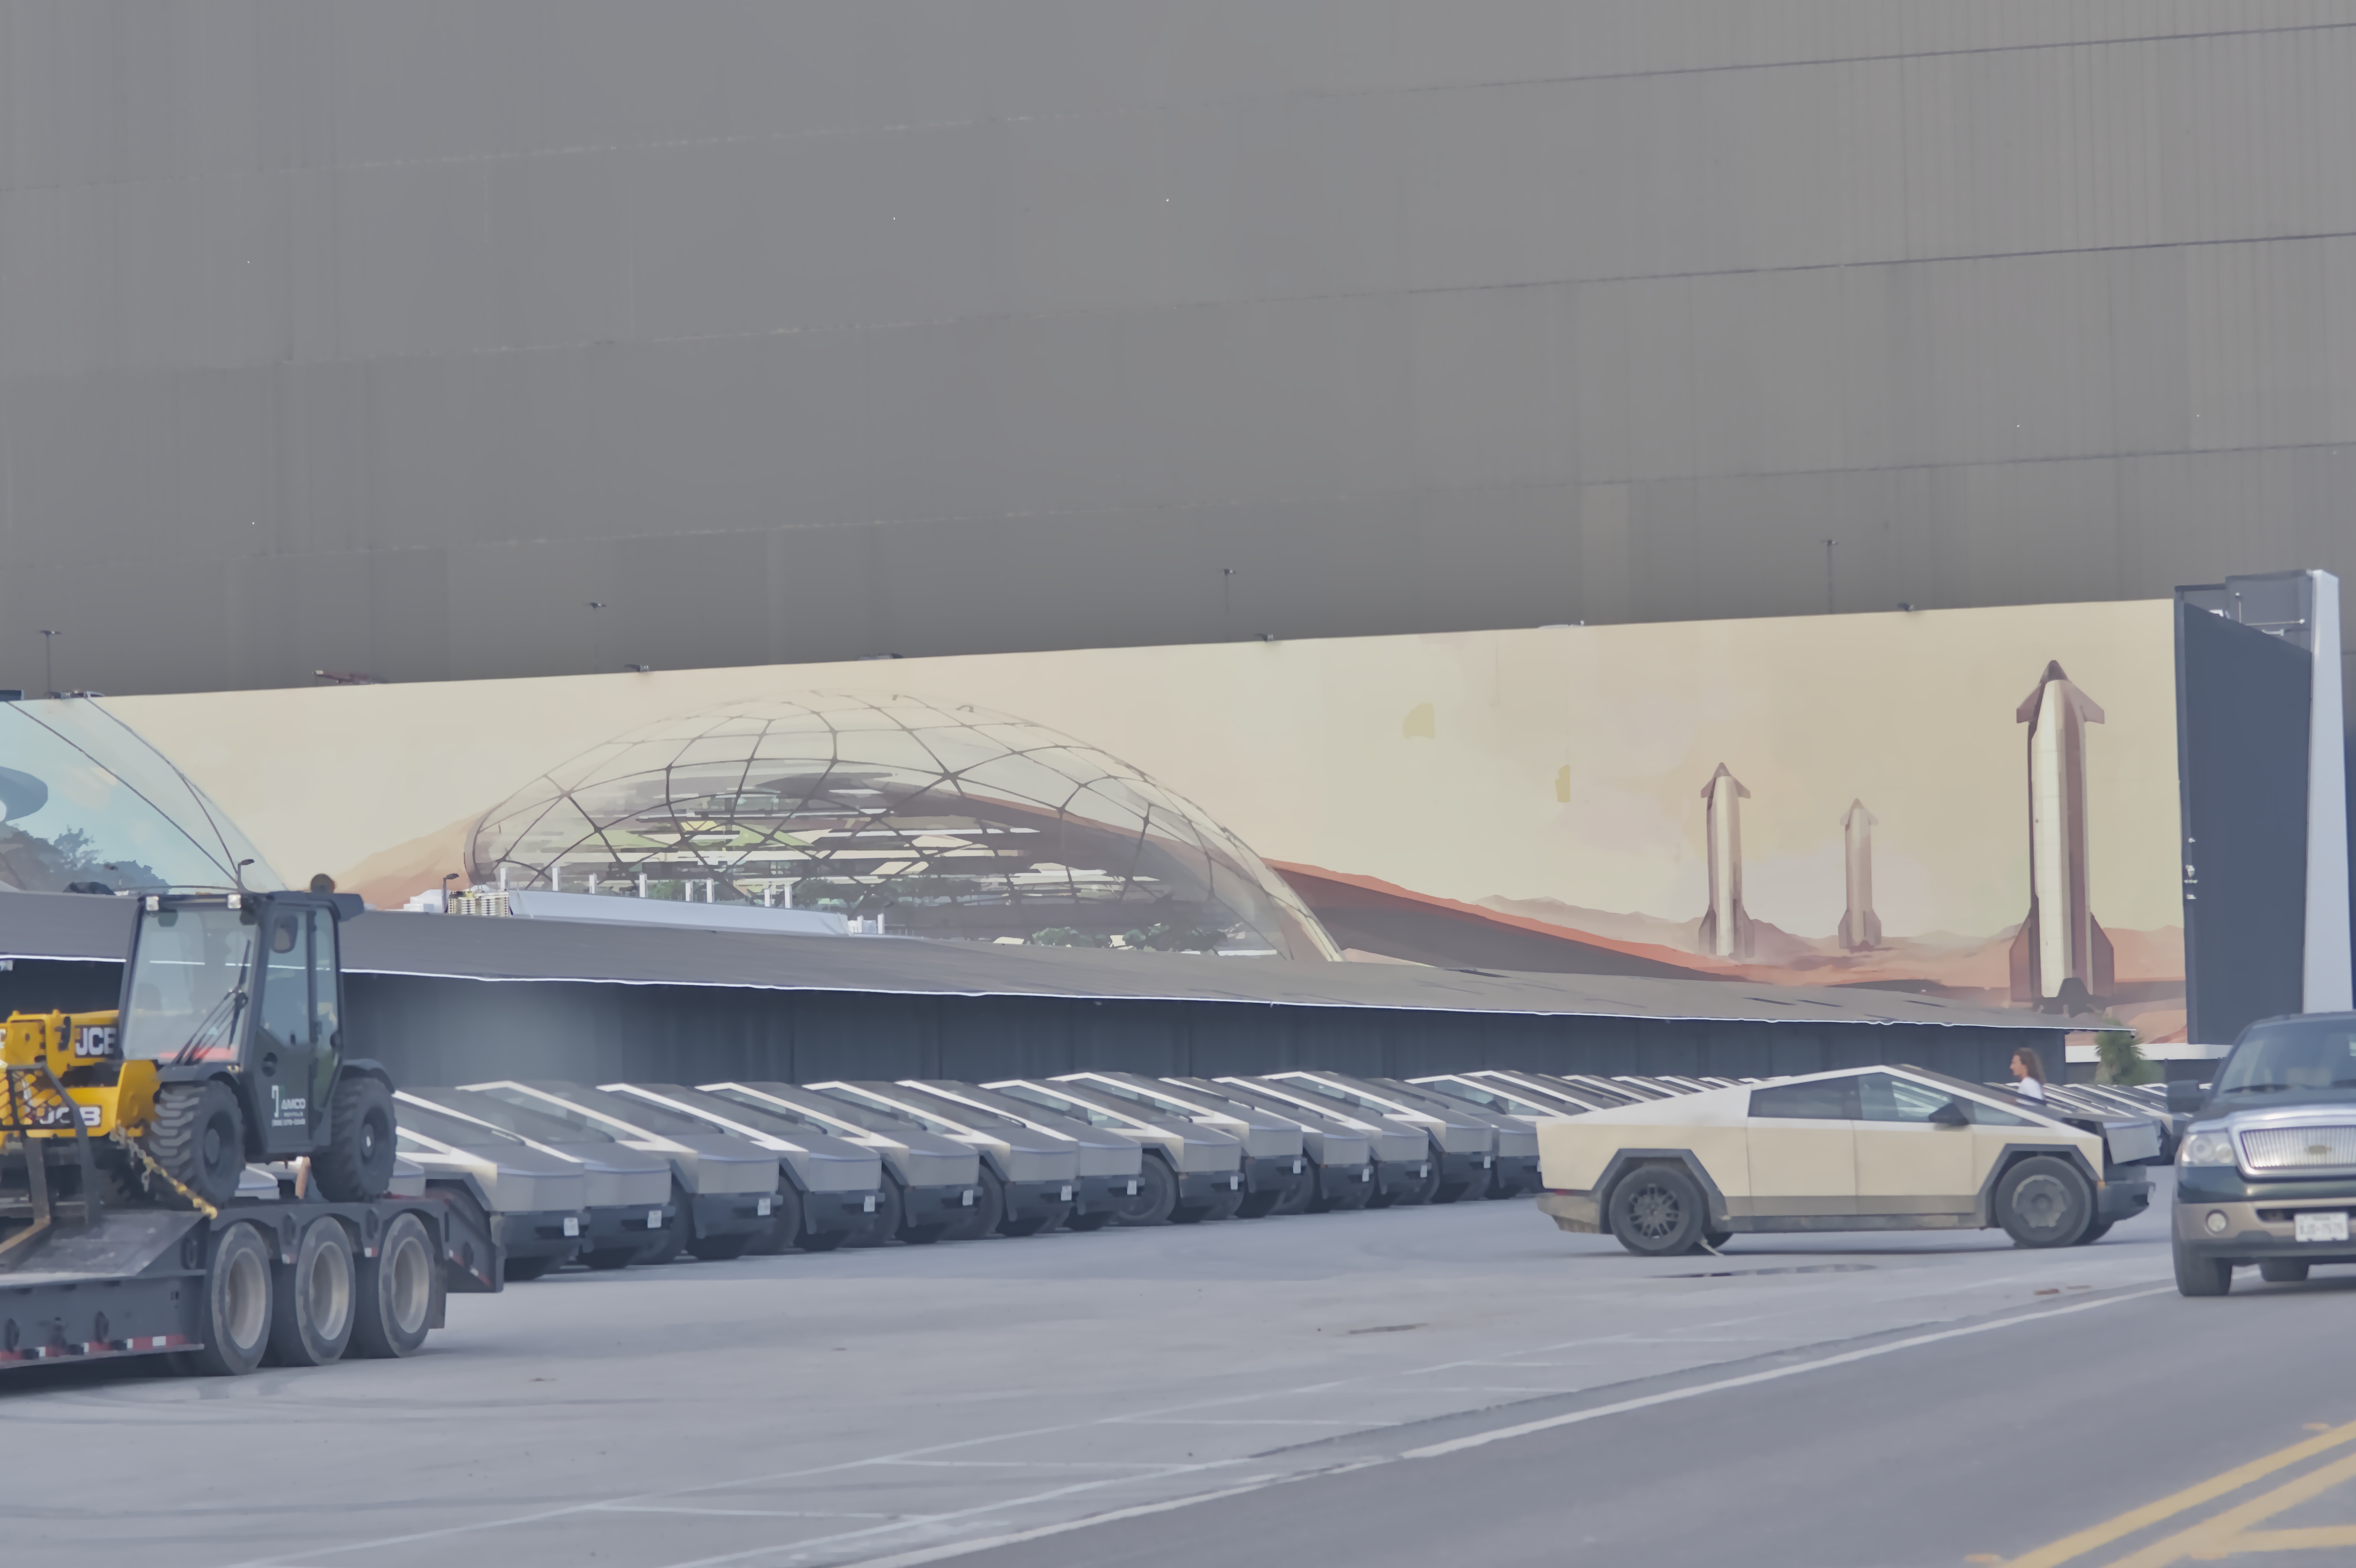
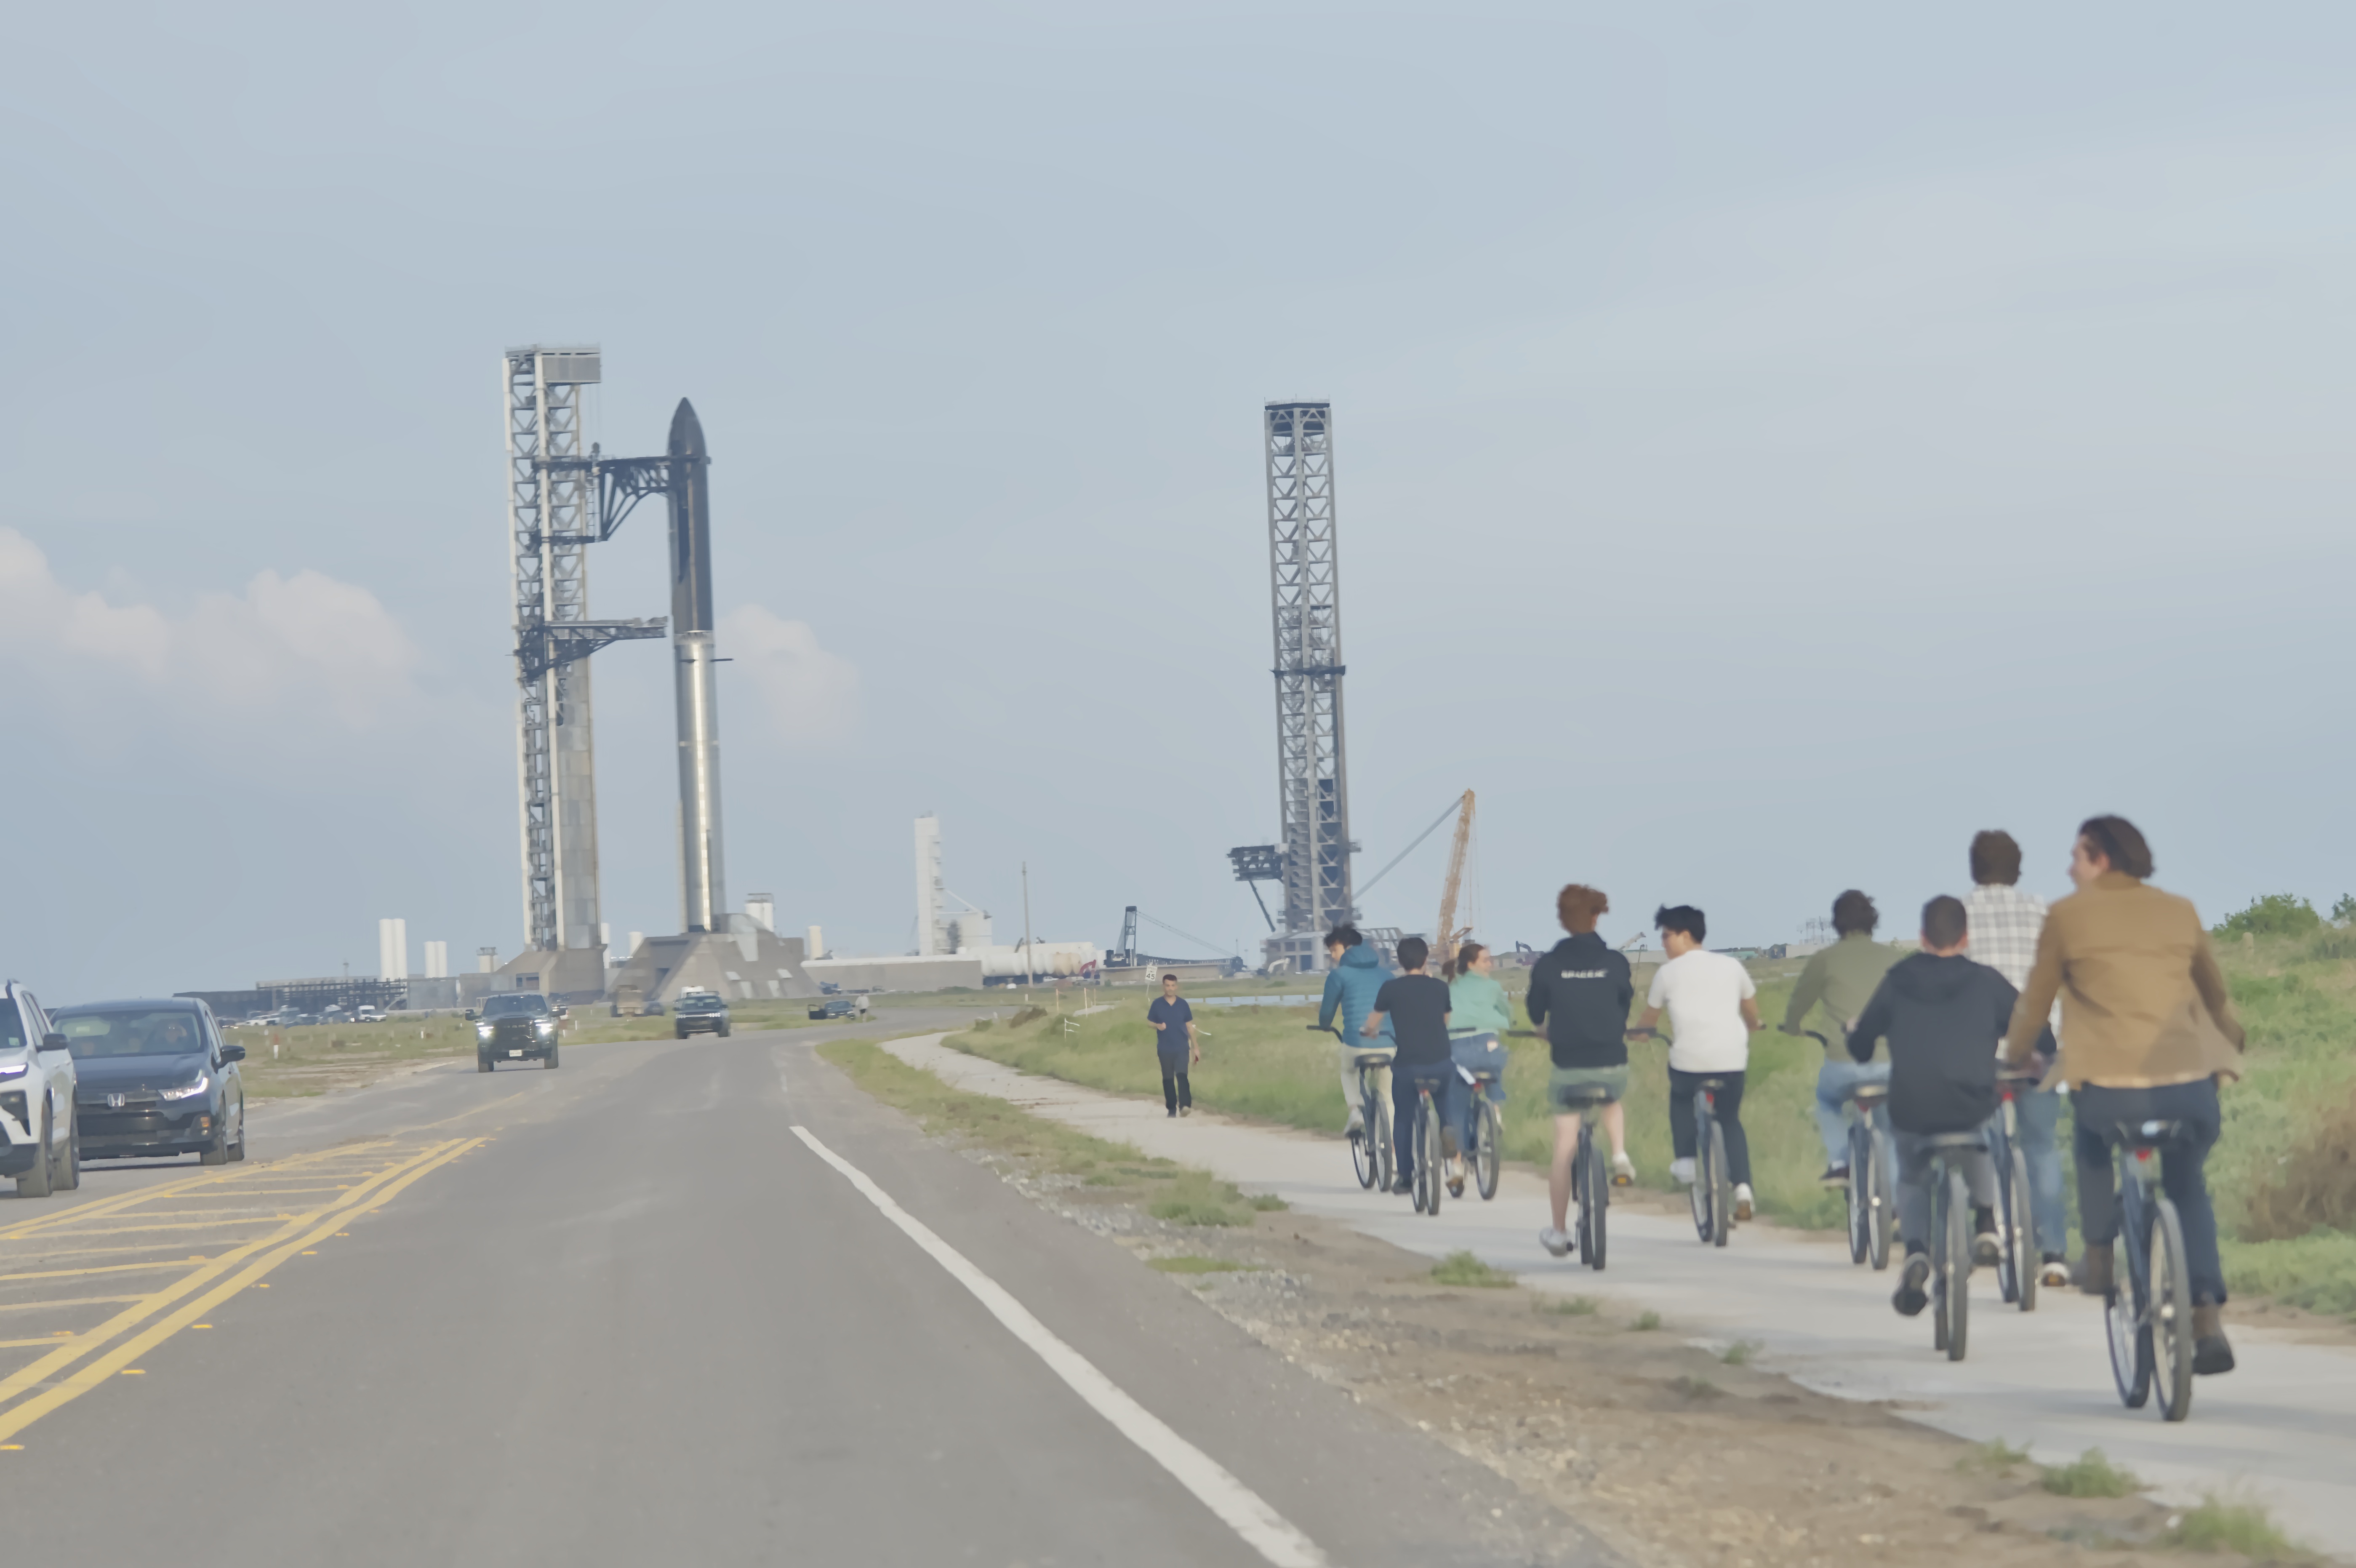
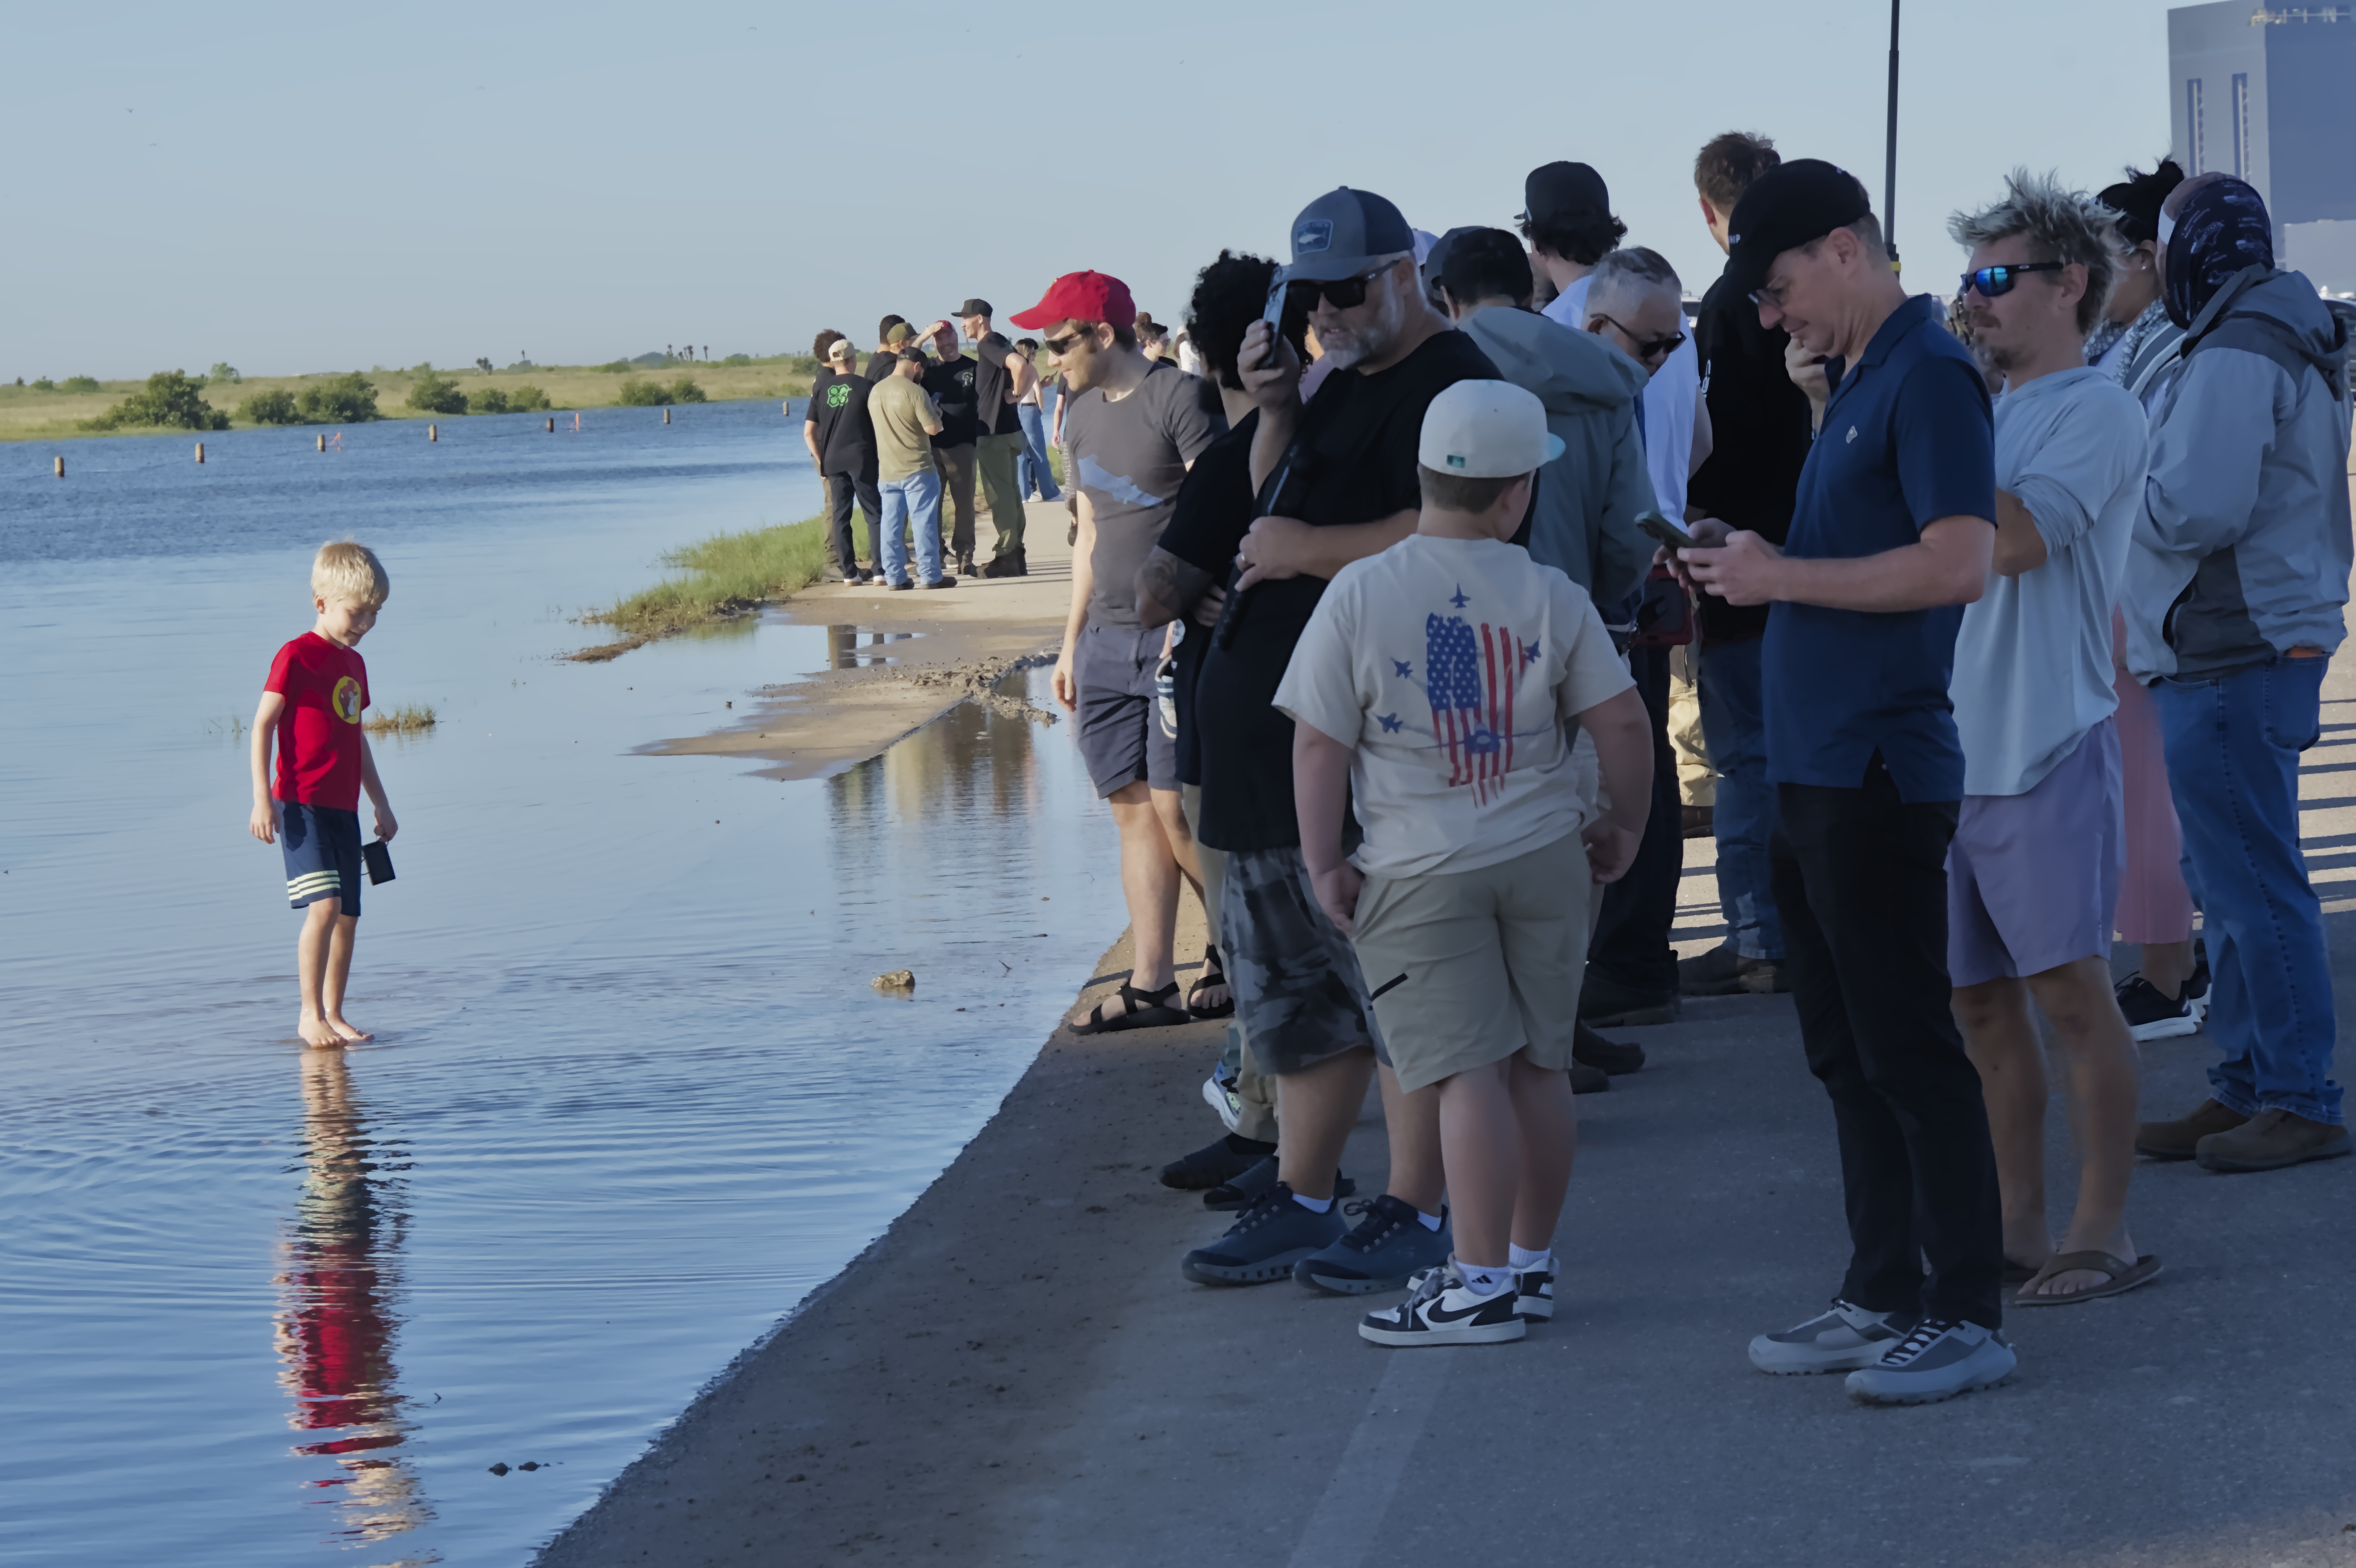
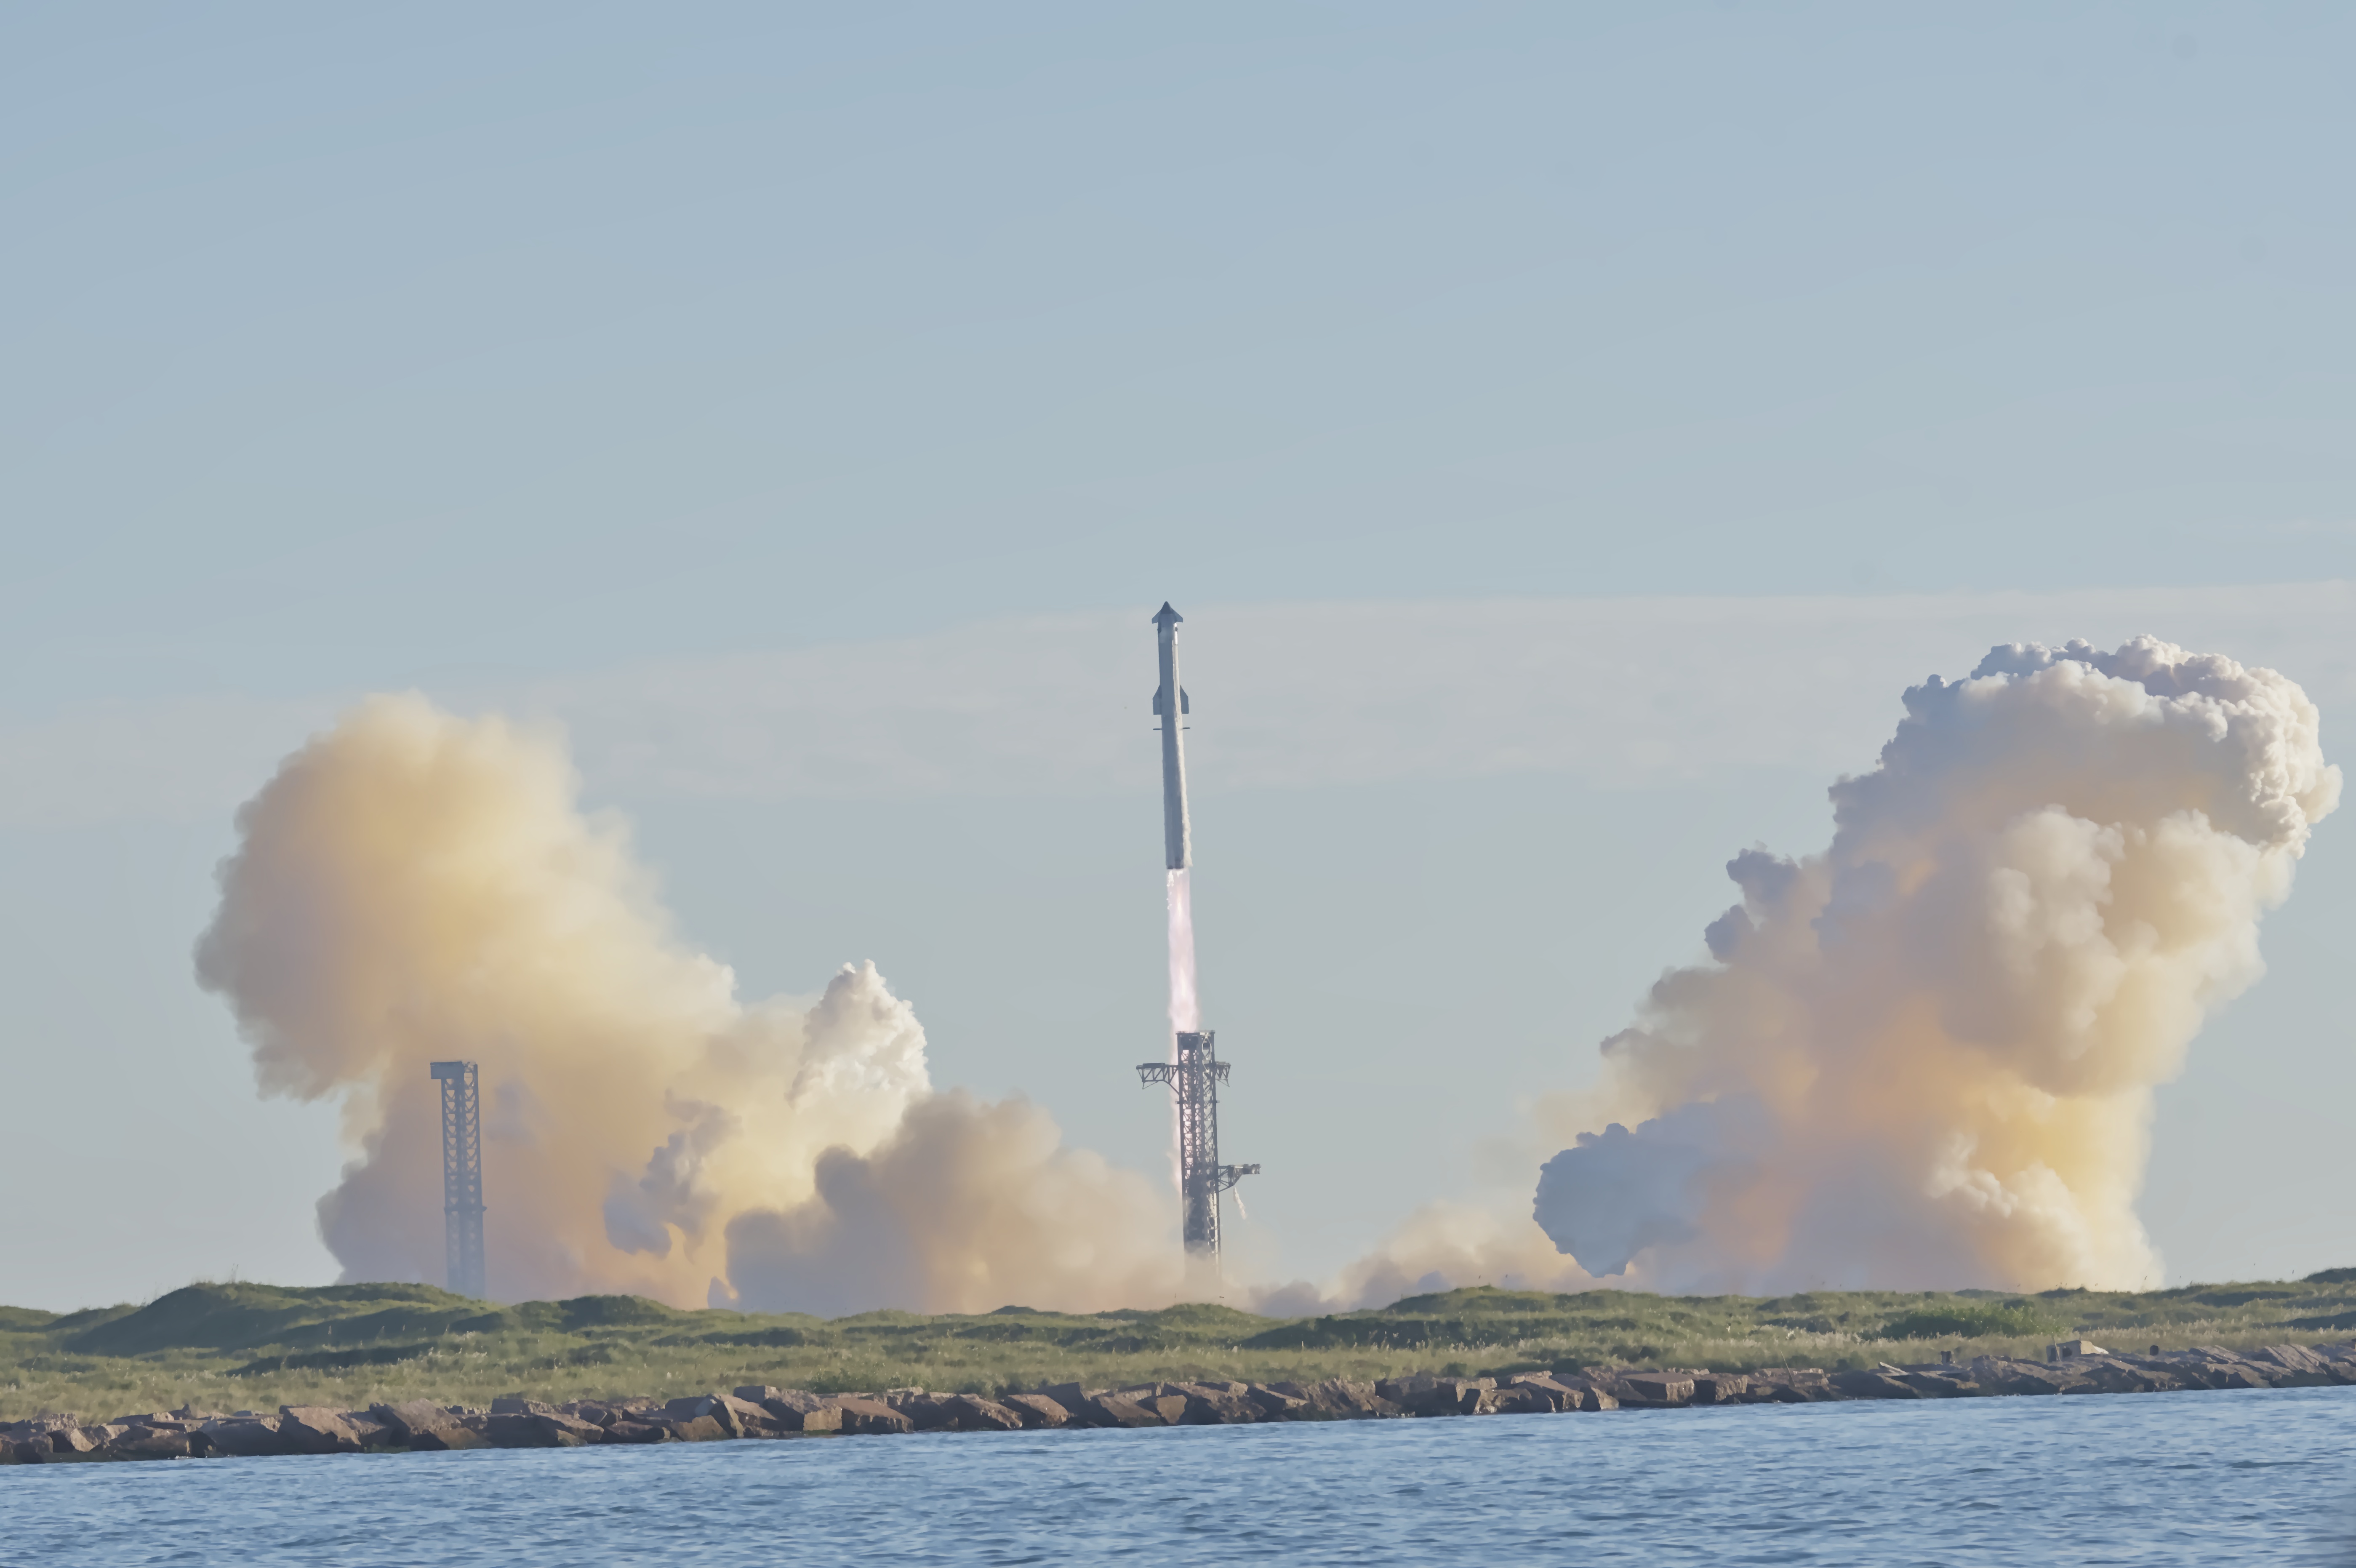
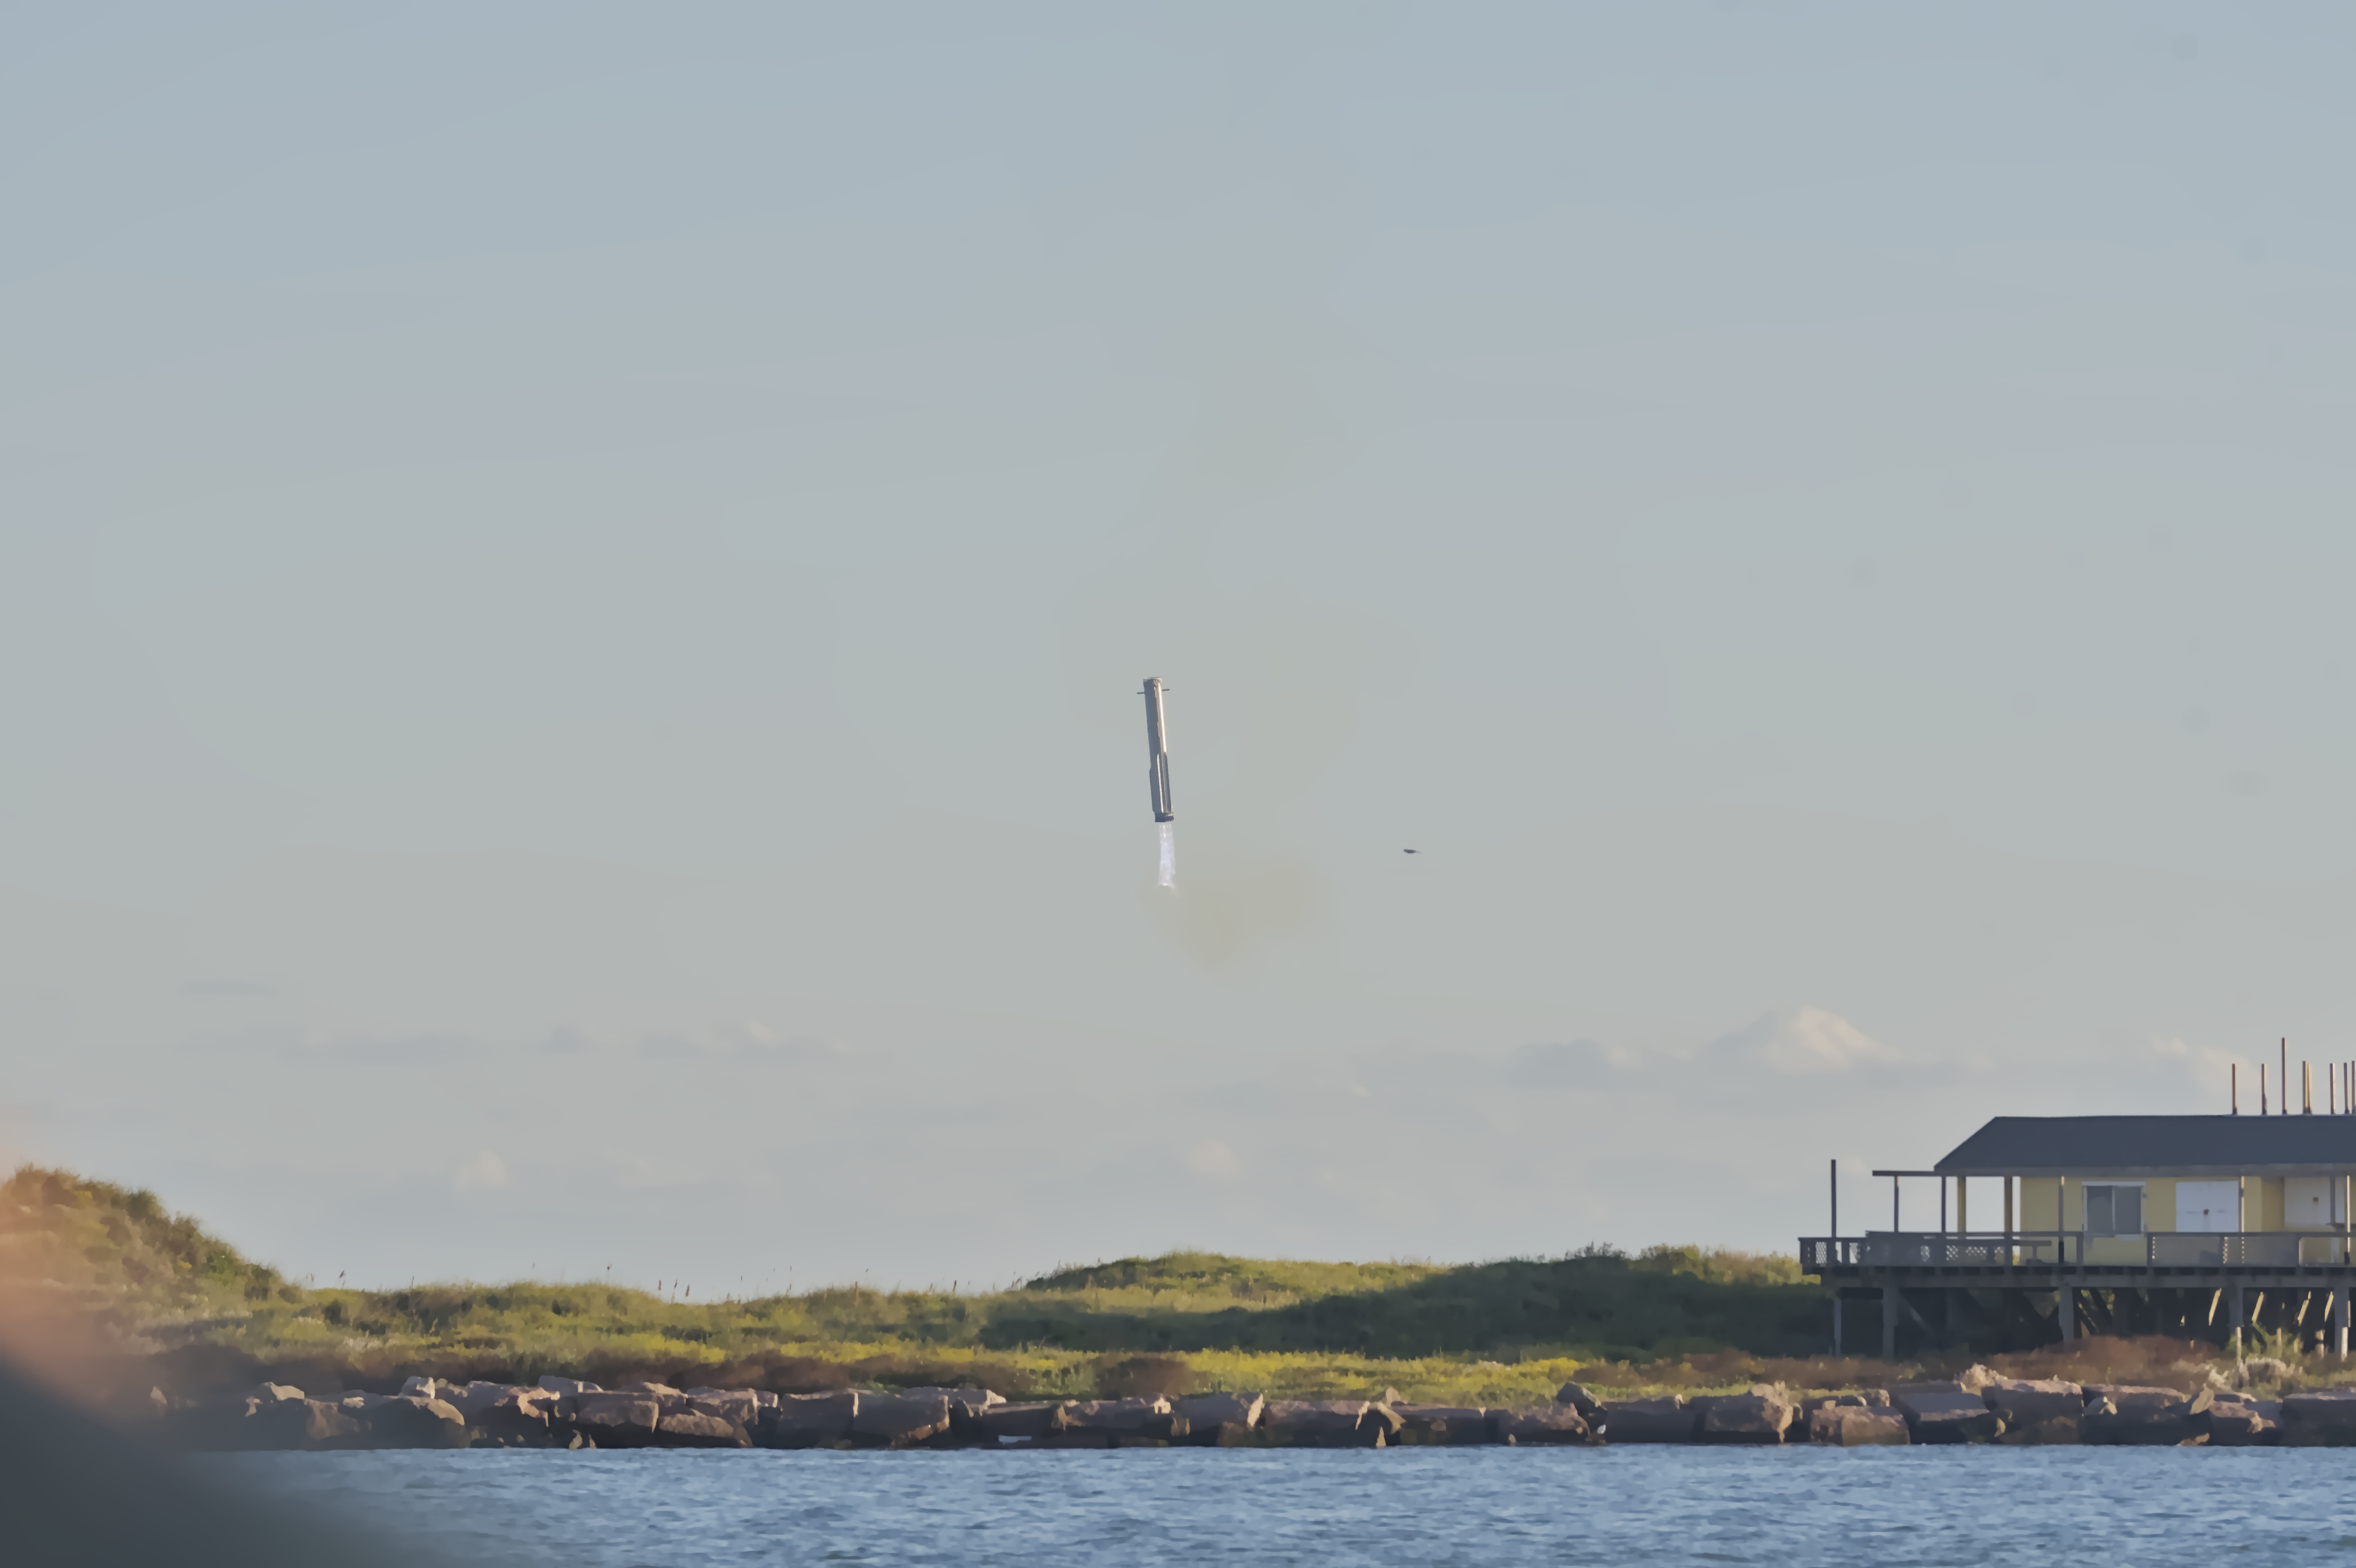
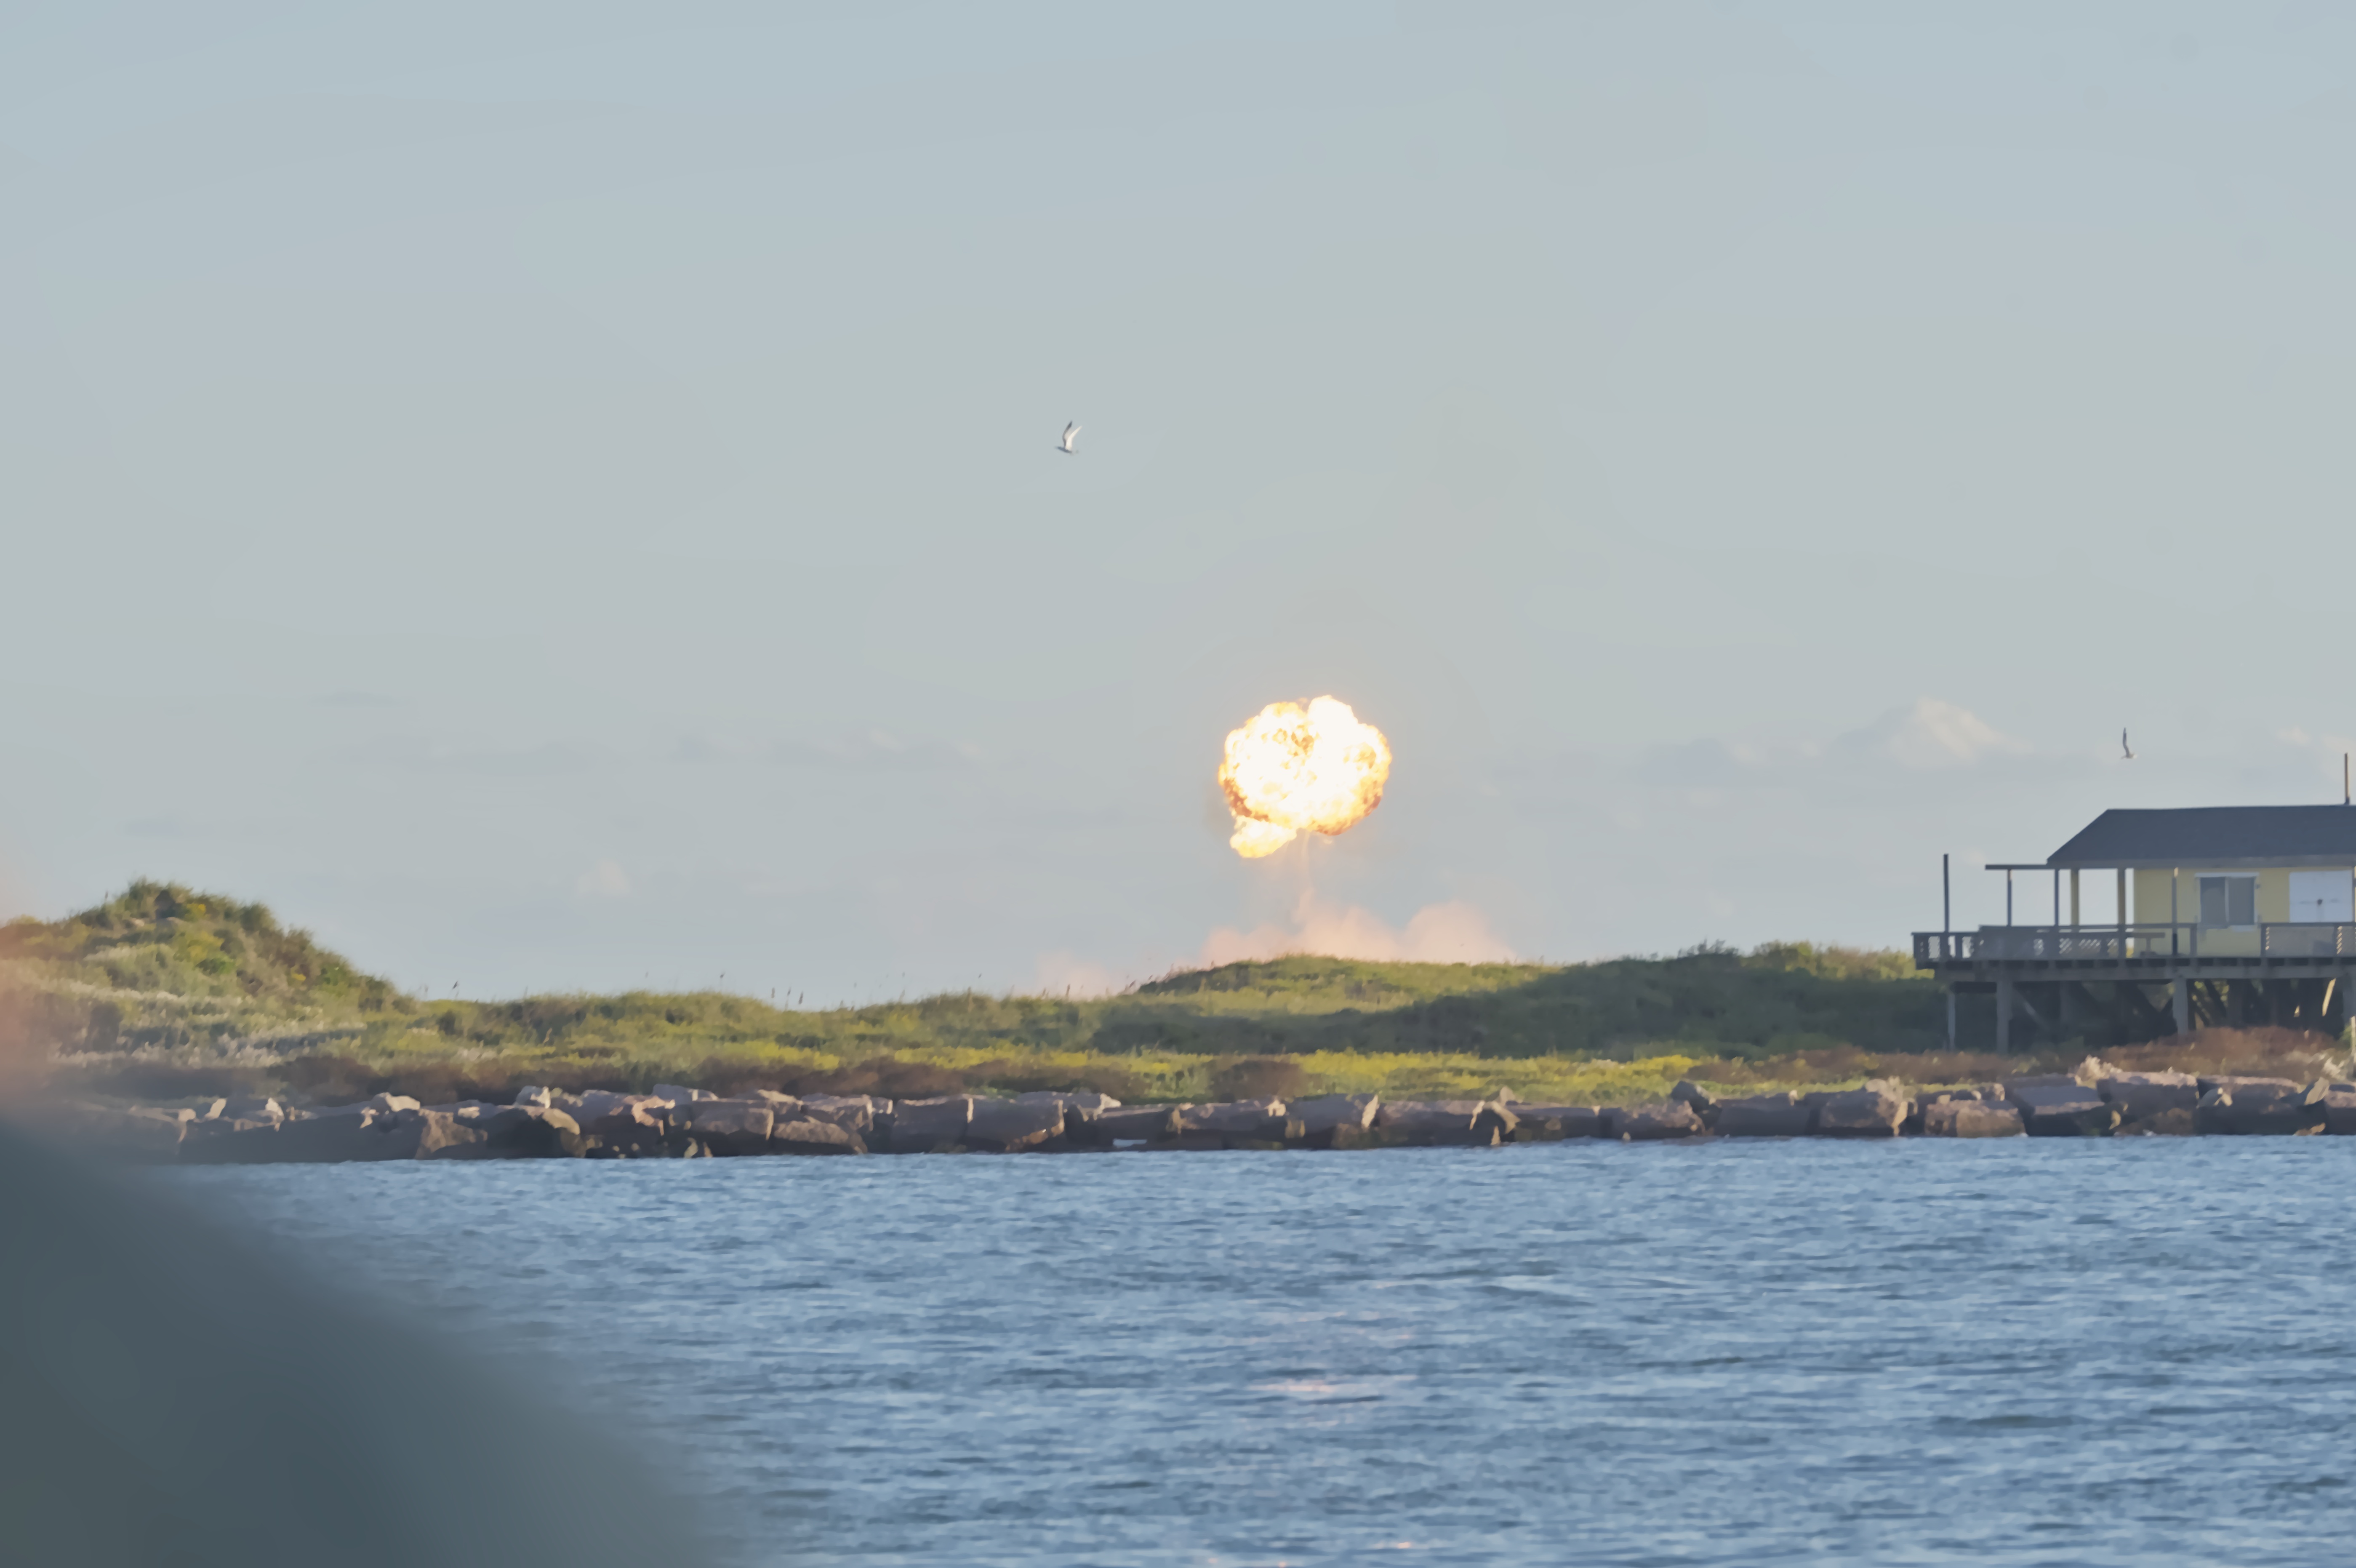
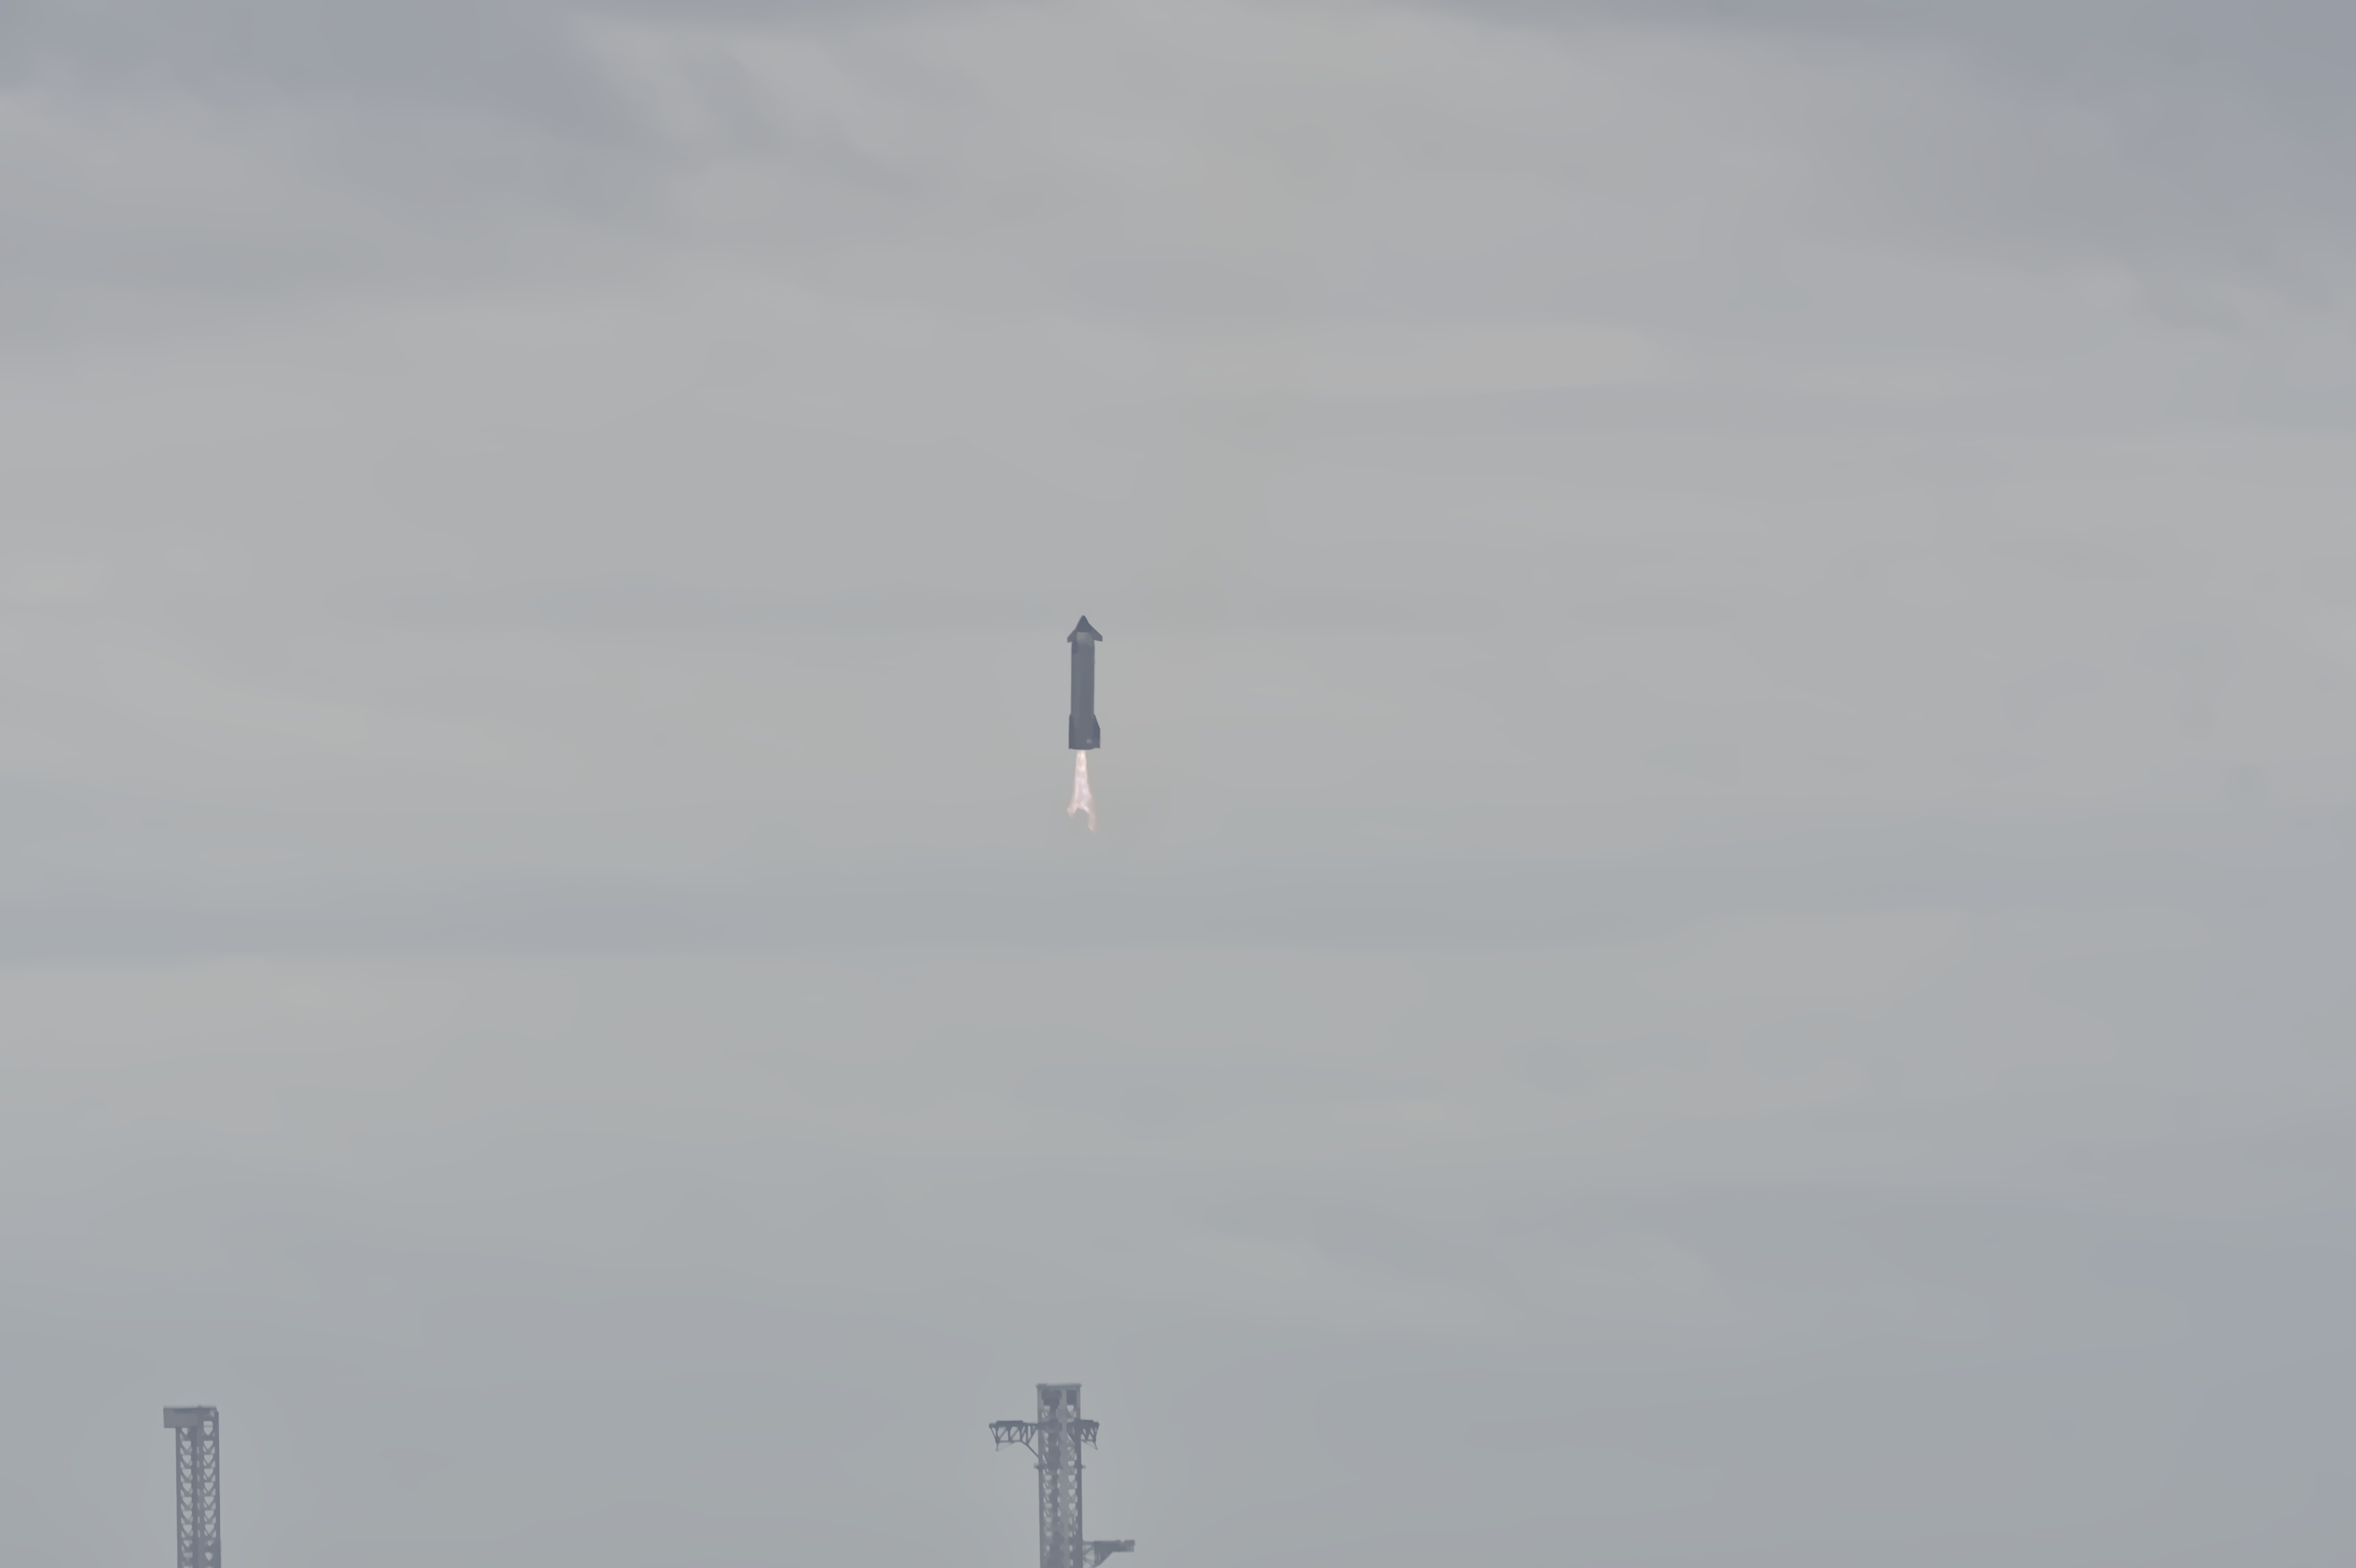
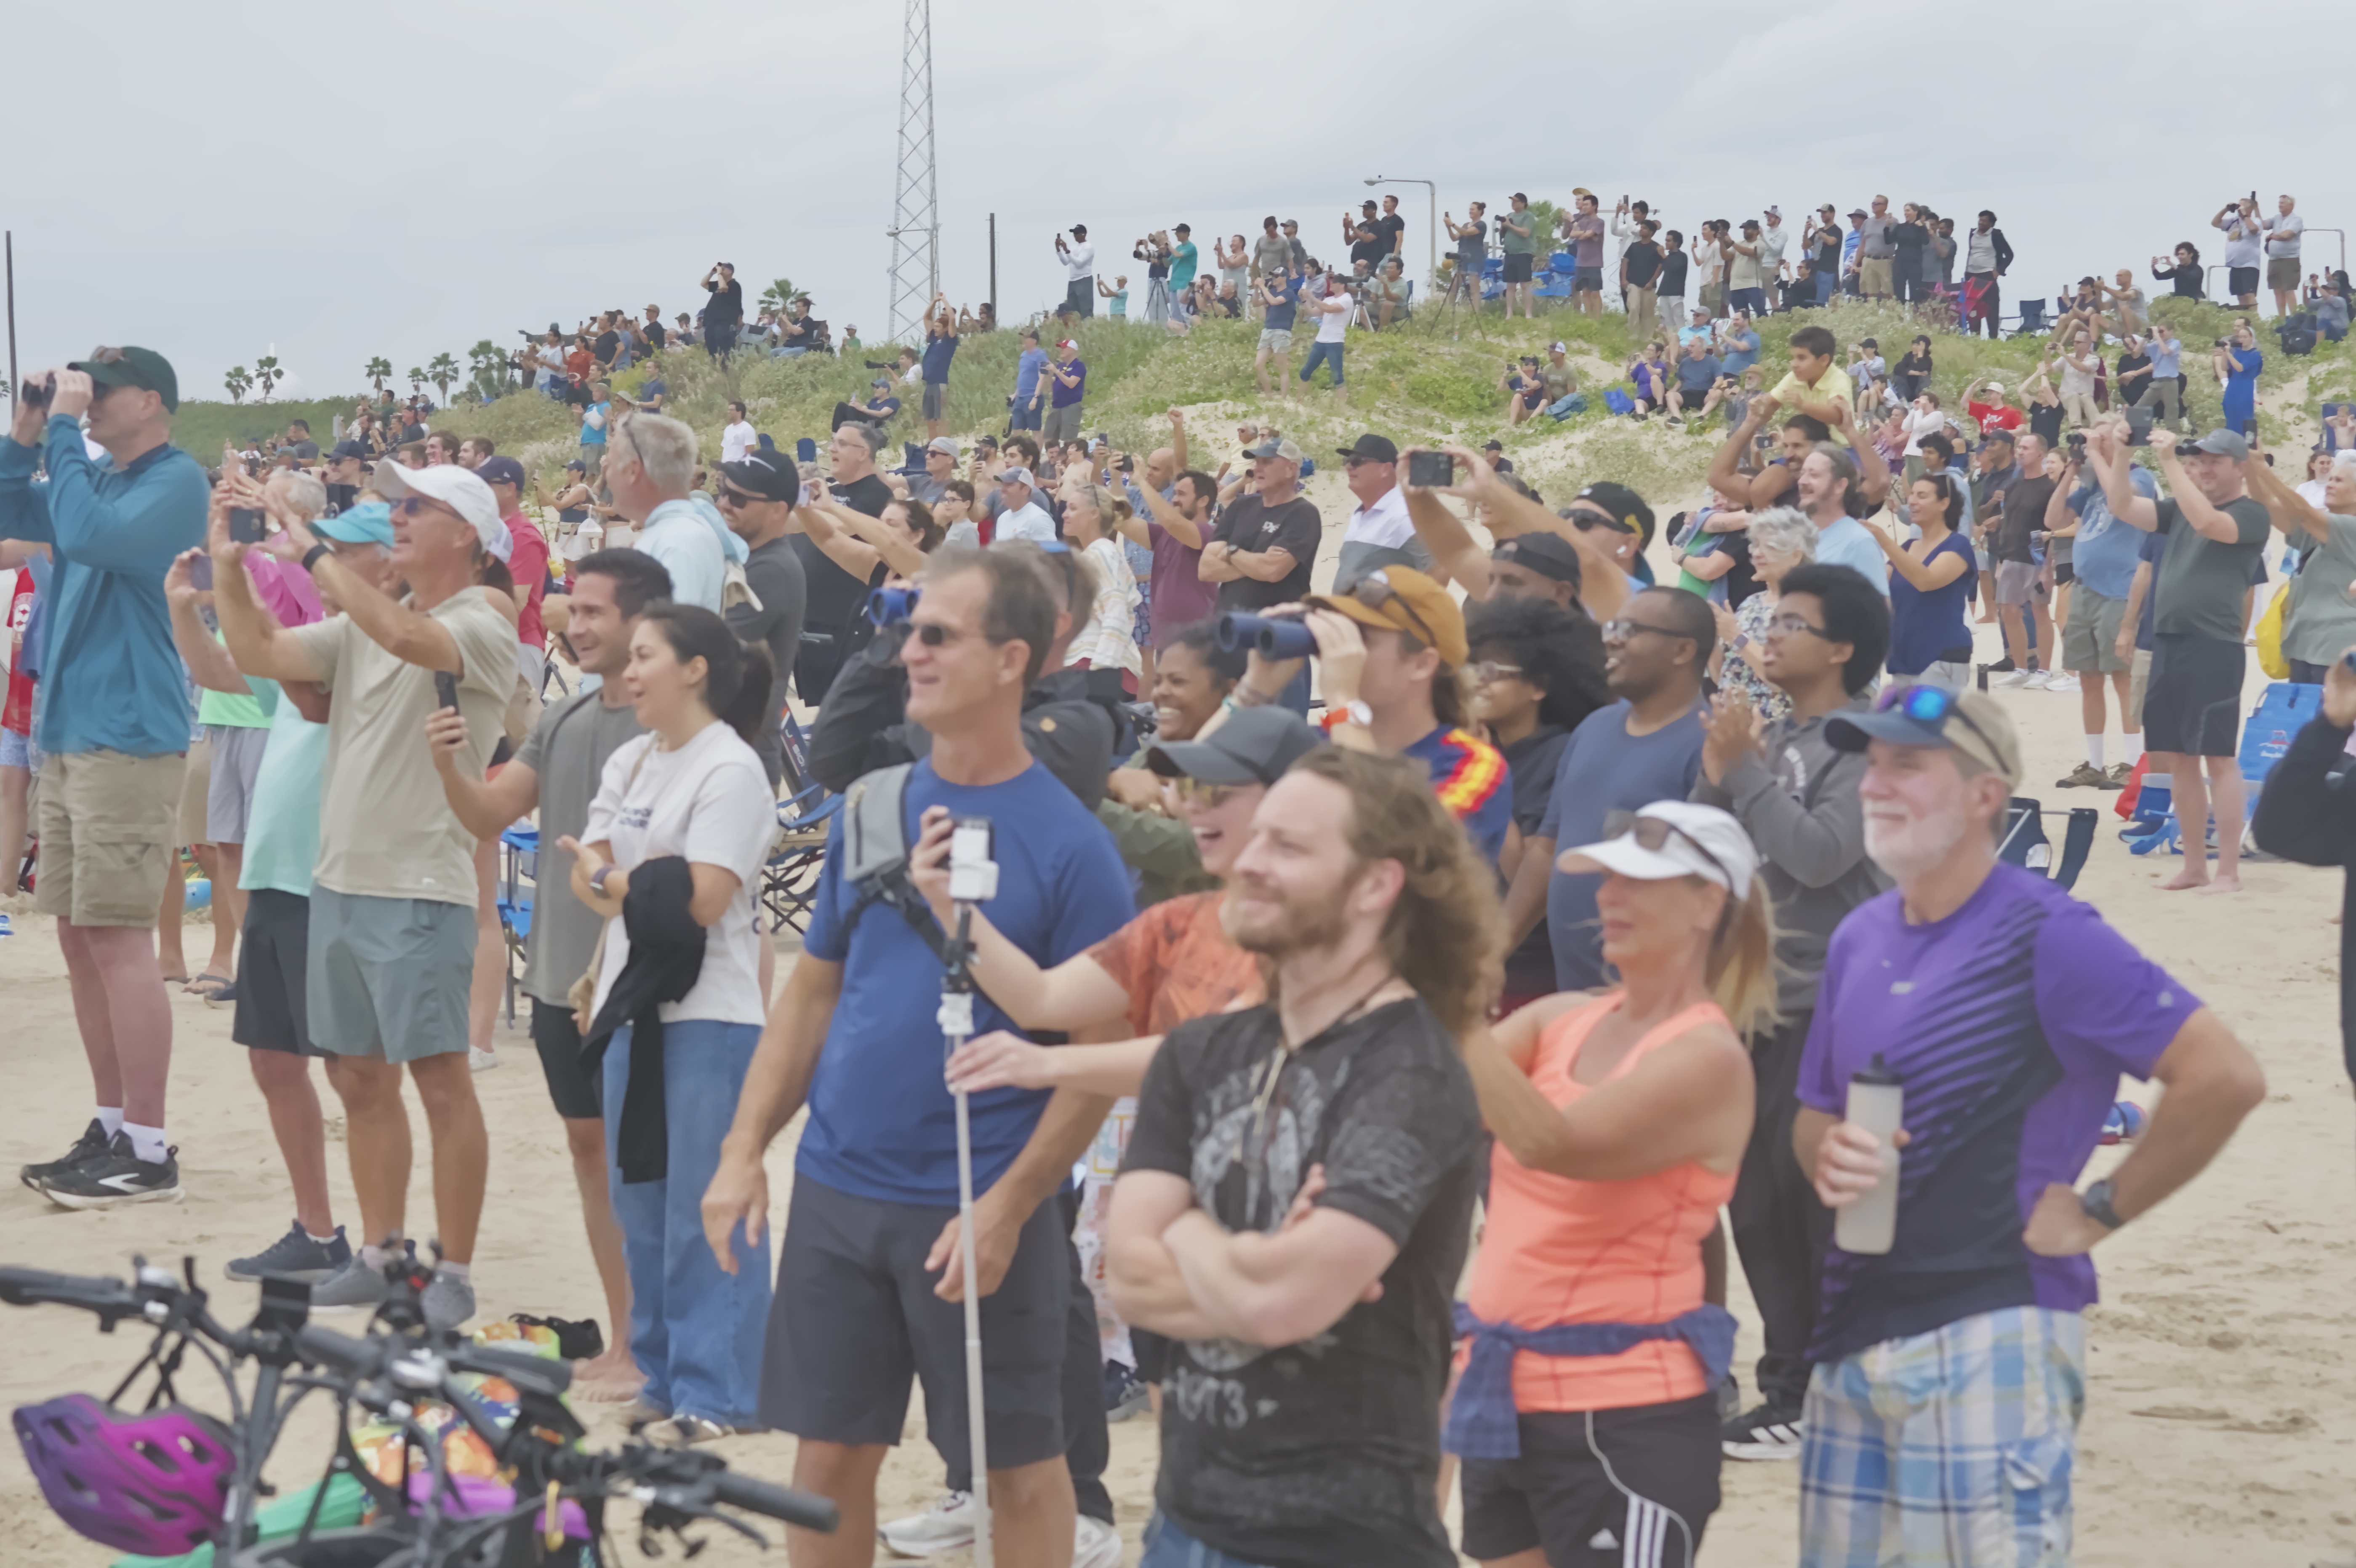
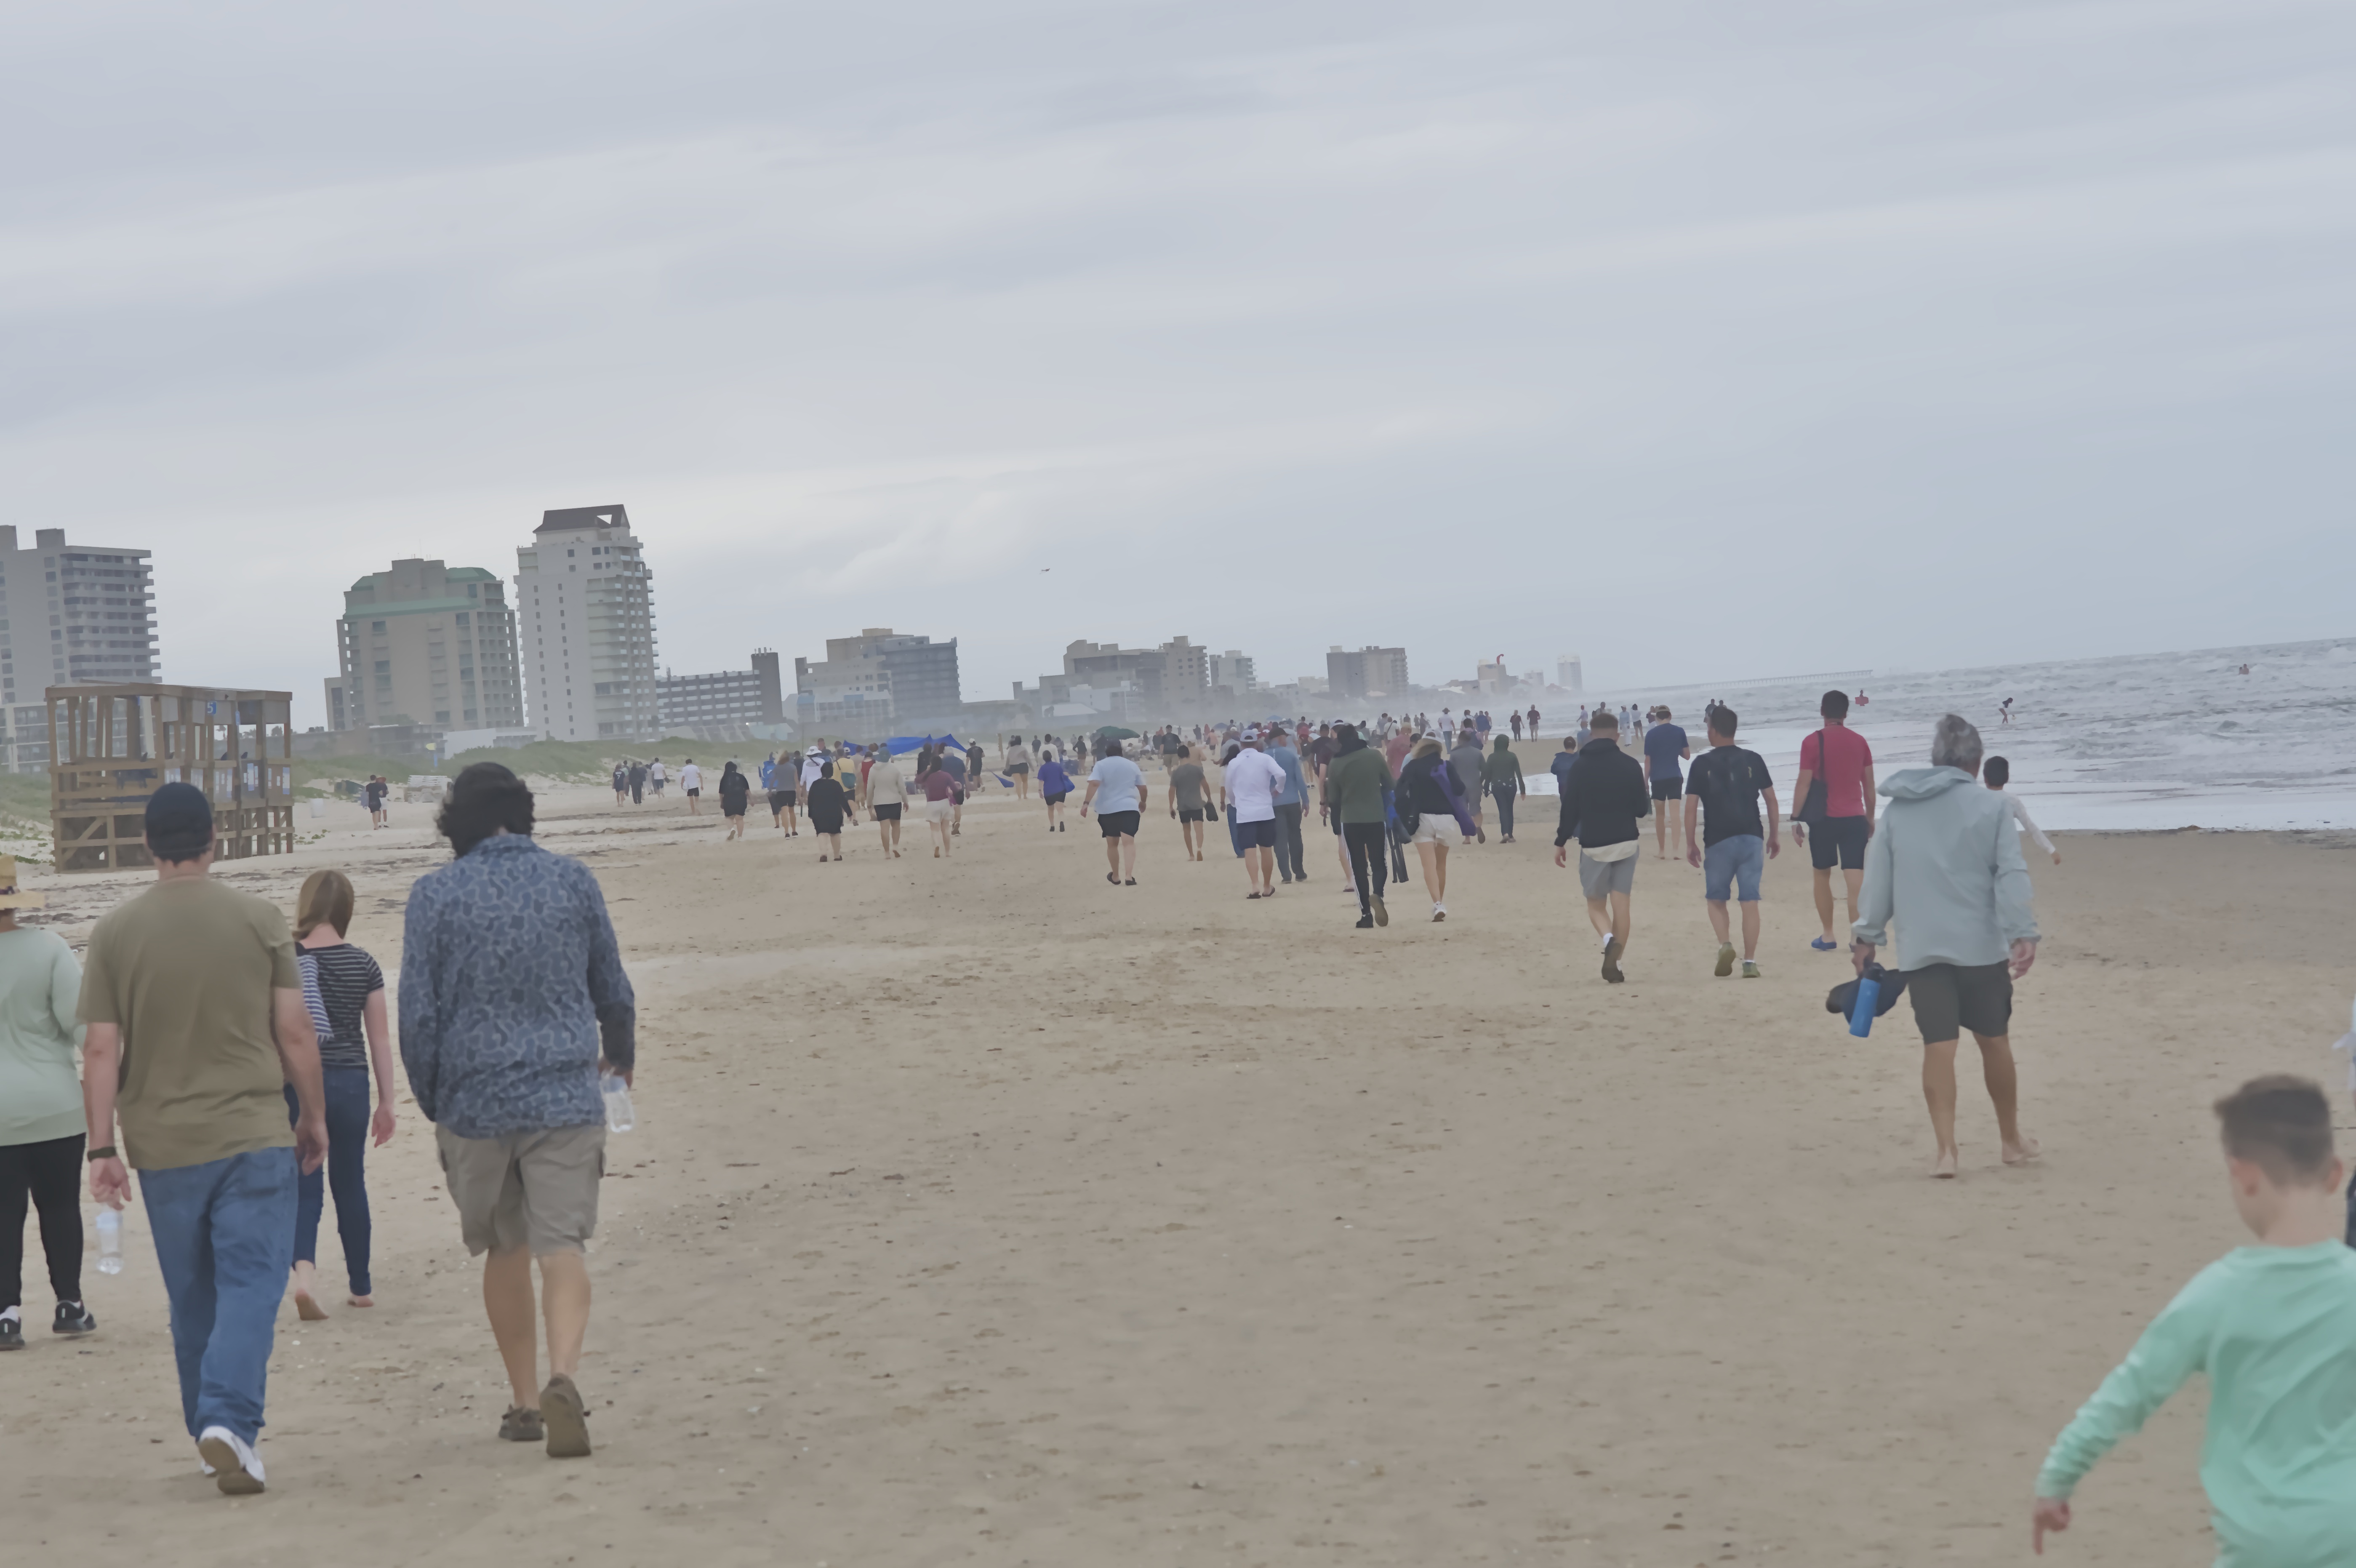
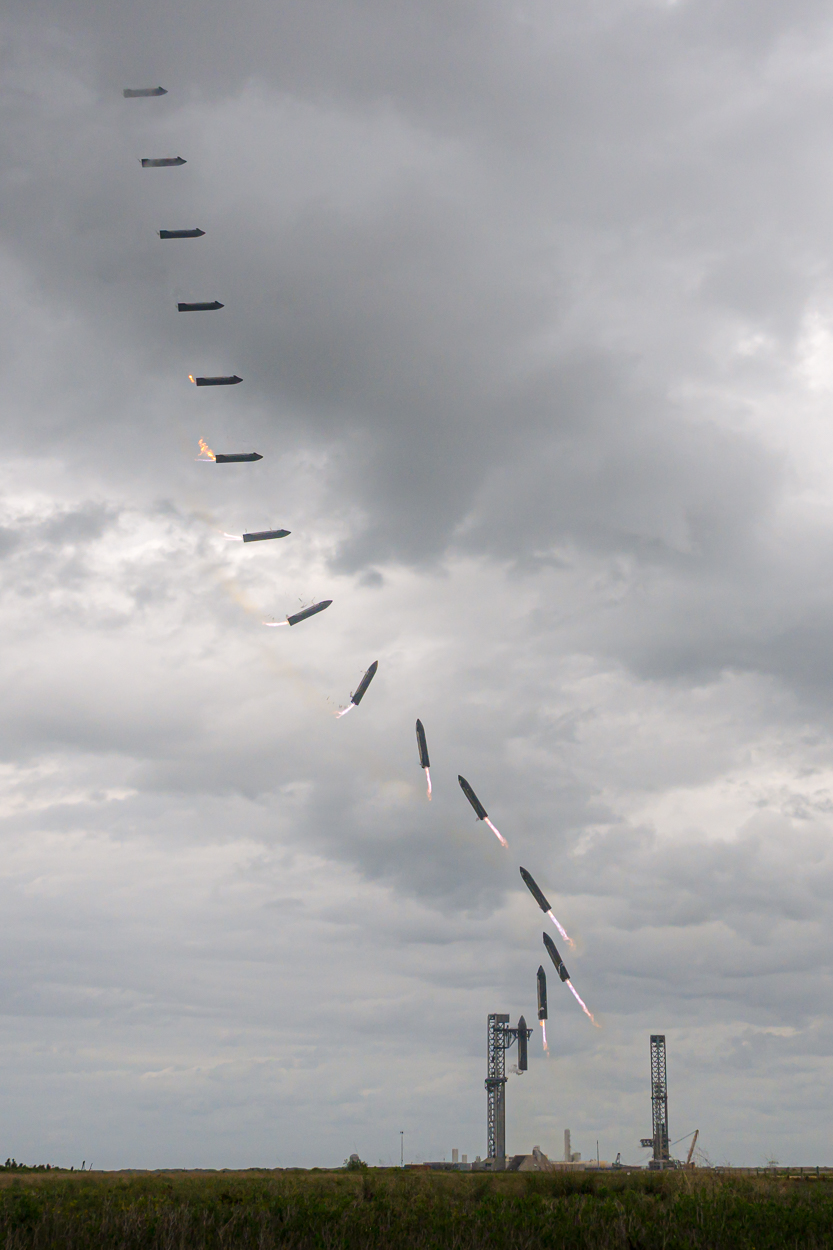




 You helped testing Fedora 50 i18n features
 You helped testing Fedora 49 i18n features
 You helped testing Fedora 48 i18n features
 You helped testing Fedora 47 i18n features
 You helped testing Fedora 46 i18n features
 You helped solidify the core for the Fedora 50 rebase!
 You helped solidify the core for the Fedora 49 rebase!
 You helped solidify the core for the Fedora 48 rebase!
 You helped solidify the core for the Fedora 47 rebase!
 You helped solidify the core for the Fedora 46 rebase!
 You helped solidify the core for the Fedora 45 rebase!